
Cyber
Hirudo Android malware replaces banking apps to evade security checks
A newly discovered Android malware named Hirudo is stealing banking credentials by substituting legitimate financial apps with modified versions.
Tag
The latest news, analysis and stories about Kiberxavfsizlik — TECC.UZ.
320 articles
A newly discovered Android malware named Hirudo is stealing banking credentials by substituting legitimate financial apps with modified versions.
A Saudi OpenAI engineer was arrested for allegedly placing a hidden recording device in an executive conference room.
Anthropic warns that small AI models could soon self-replicate across consumer IoT devices, forming distributed botnets without relying on data centers.
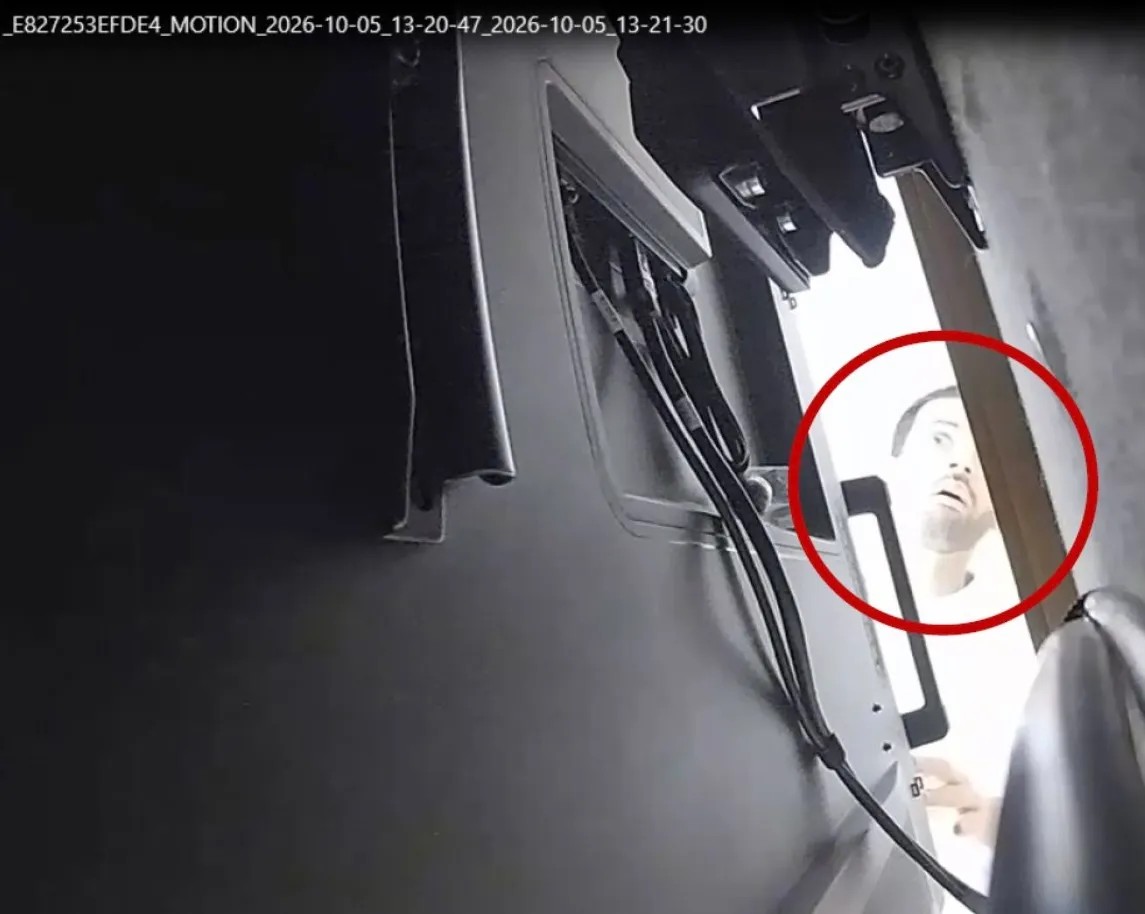
The FBI has detained an OpenAI staff member allegedly scheming to capture sensitive communications regarding super intelligence tech.
Microsoft's October Patch Tuesday features a record 1,411 security fixes, including one actively exploited and two publicly disclosed zero-day flaws.
Microsoft has rolled out the Windows 10 KB5126657 extended security update featuring crucial patch fixes and bug improvements.
Ivanti has urged customers to immediately patch a zero-day vulnerability in its Connect Secure remote access gateway that is being actively exploited.
Anthropic revokes internet access for high-risk AI test models following security incidents involving U.S. government websites.
Attackers remotely defrosted refrigeration units at multiple French supermarket chains overnight in a targeted cyberattack.
Global food retail giant Ahold Delhaize confirmed it took several systems offline following a cybersecurity incident affecting its network.
GitLab has urged users to immediately patch a maximum-severity vulnerability in the CI/CD Regular Expression Compiler allowing remote code execution.
Canadian cybersecurity executive Edward Dubrovsky has been arrested in Pennsylvania over alleged extortion activities.
Microsoft CEO outlines his views on the dangers posed by advanced AI models and the necessity of shifting our approach to security.
Cybercriminals are exploiting legitimate Bing search redirects within Google search ads to deliver fake Claude installers and execute ClickFix attacks.
The FBI has apprehended another suspected member of the ShinyHunters extortion group linked to the recent breach of bureau systems.
Hardware wallet giant Ledger is investigating potential security breaches after reports emerged of $86 million in stolen cryptocurrency.
Microsoft states that devices running unsupported Windows versions will no longer receive security updates after next year's certificate rotation.
The operator of a major illicit dark web trading platform has been handed a lengthy prison sentence and ordered to forfeit massive cryptocurrency assets.
Citrix urges IT administrators to immediately patch critical RCE vulnerabilities affecting NetScaler ADC and Gateway appliances.
iVerify has released a new report detailing P7 DarkSword, a spyware variant targeting unpatched iPhones.
A Maryland man has been convicted of stealing over $53 million by hacking the decentralized crypto exchange Uranium Finance twice in April 2021.
New findings reveal that certain budget Android smartphones come straight out of the box pre-installed with a dangerous malware known as Midnight Mimosa.
Microsoft is introducing third-party deepfake detection solutions and impersonation protection features to Teams meetings.
On the second day of Pwn2Own Ireland 2026, security researchers collected $232,500 in cash awards after exploiting 45 unique zero-day vulnerabilities.