

Cyber
Ransomware's new target: Is your backup infrastructure ready?
Ransomware groups are increasingly targeting backup infrastructure to eliminate recovery options and force victims to pay. Kaseya outlines key protection strategies.
Category
Defense, threats, security strategy and auditing.
203 articles
Ransomware groups are increasingly targeting backup infrastructure to eliminate recovery options and force victims to pay. Kaseya outlines key protection strategies.
A critical unauthenticated vulnerability (CVE-2026-21589) affecting Jira, Confluence, and Bitbucket is being actively exploited in attacks.
On the first day of the Pwn2Own Ireland 2026 competition, security researchers hacked the Samsung Galaxy S26 twice and earned $388,500 after exploiting 32 zero-days.
UK fashion retailer ASOS confirmed a security breach after unauthorized push notifications claiming data theft were sent through its mobile app.
A former core infrastructure engineer at a New Jersey industrial company was sentenced to 32 months in prison for a ransomware-style network attack.
According to BleepingComputer, hackers are actively scanning the web for the CVE-2026-61500 vulnerability in Rejetto HFS, which leads to account takeover and RCE.
Dell has urged customers to immediately patch a critical vulnerability found in the System Update command-line interface deployment tool.
A major cyberattack on a Danish government database has compromised the names, addresses, and state ID numbers of 8 million people.
Citrix has issued emergency updates to fix a NetScaler denial-of-service vulnerability exploited in zero-day attacks.
An alleged ShinyHunters hacker operating under the alias 'Rey' has been arrested in Jordan and is reportedly helping the FBI locate associates.
A China-linked threat group has breached multiple critical sectors including water utilities and telecom providers using SharePoint exploits.
The creator of the MyChart system is shifting its focus to fixing security vulnerabilities that pose risks to patient data.
On Thursday, unknown attackers hijacked the official Microsoft account on X, which has over 13 million followers, to promote a crypto token.
Cybersecurity firm Fortinet has issued an urgent warning regarding a critical vulnerability in FortiMail actively targeted in zero-day attacks.
Magnet Forensics has reportedly found a way to bypass the iPhone security feature that automatically reboots devices after 72 hours of inactivity.
An international law enforcement operation named Operation KillSwitch successfully seized the KillSec ransomware gang's servers and data leak site.
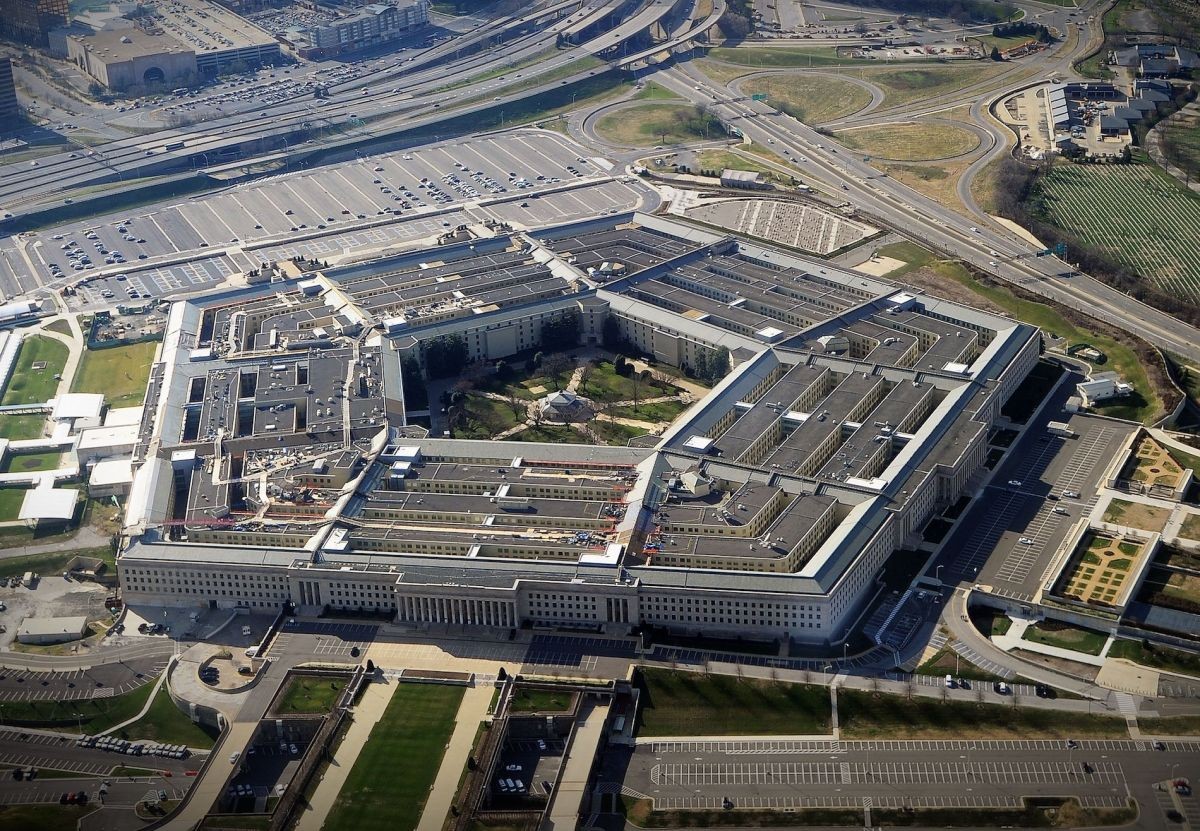
The Pentagon is notifying millions of service members after hackers breached its HR management system in October 2025, stealing records of over 3 million people.
The Russian state-sponsored group Star Blizzard has adopted a new malware installation tactic called RedFlick to deploy its CosmicPulse backdoor.
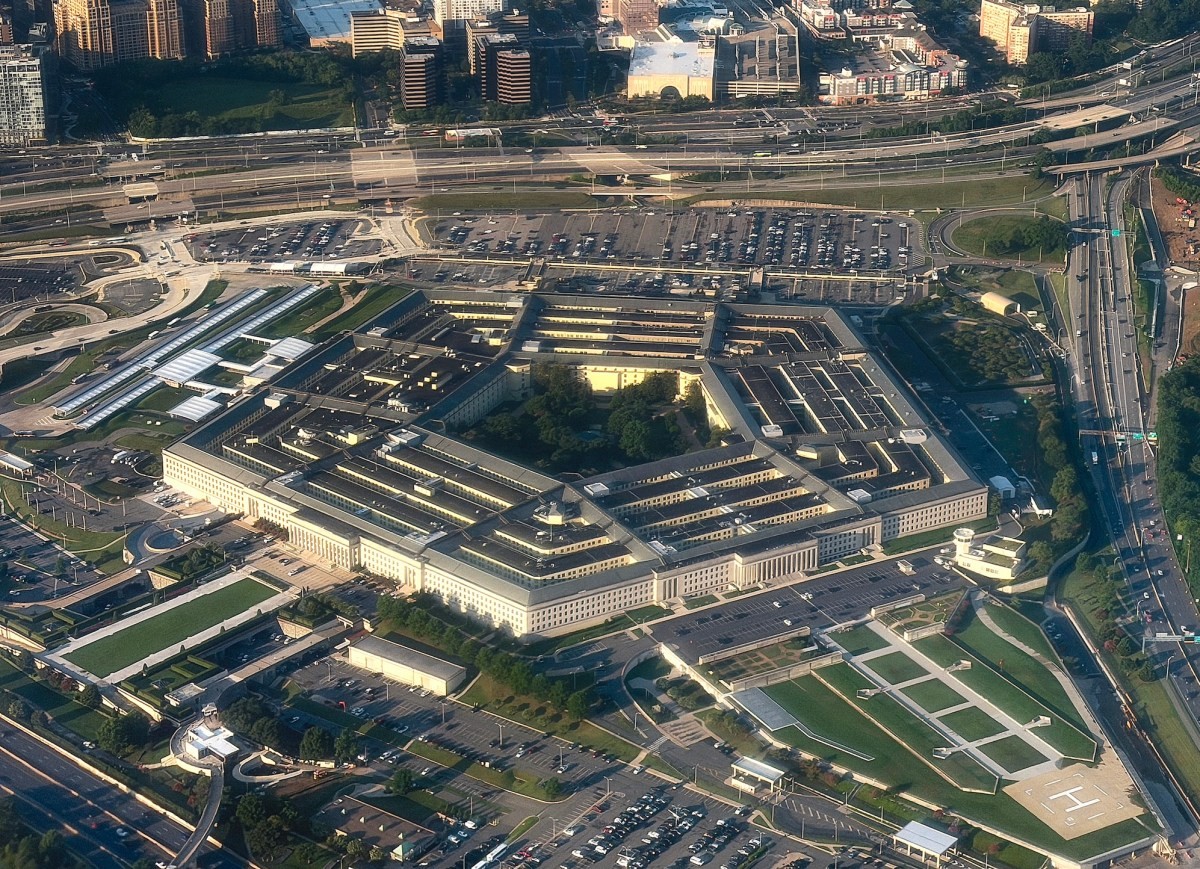
The Department of Defense notified millions of current and former U.S. military personnel about a major data breach.
According to BleepingComputer, more than 543,000 credentials exposed in public GitHub repositories remained valid in July despite platform security measures.
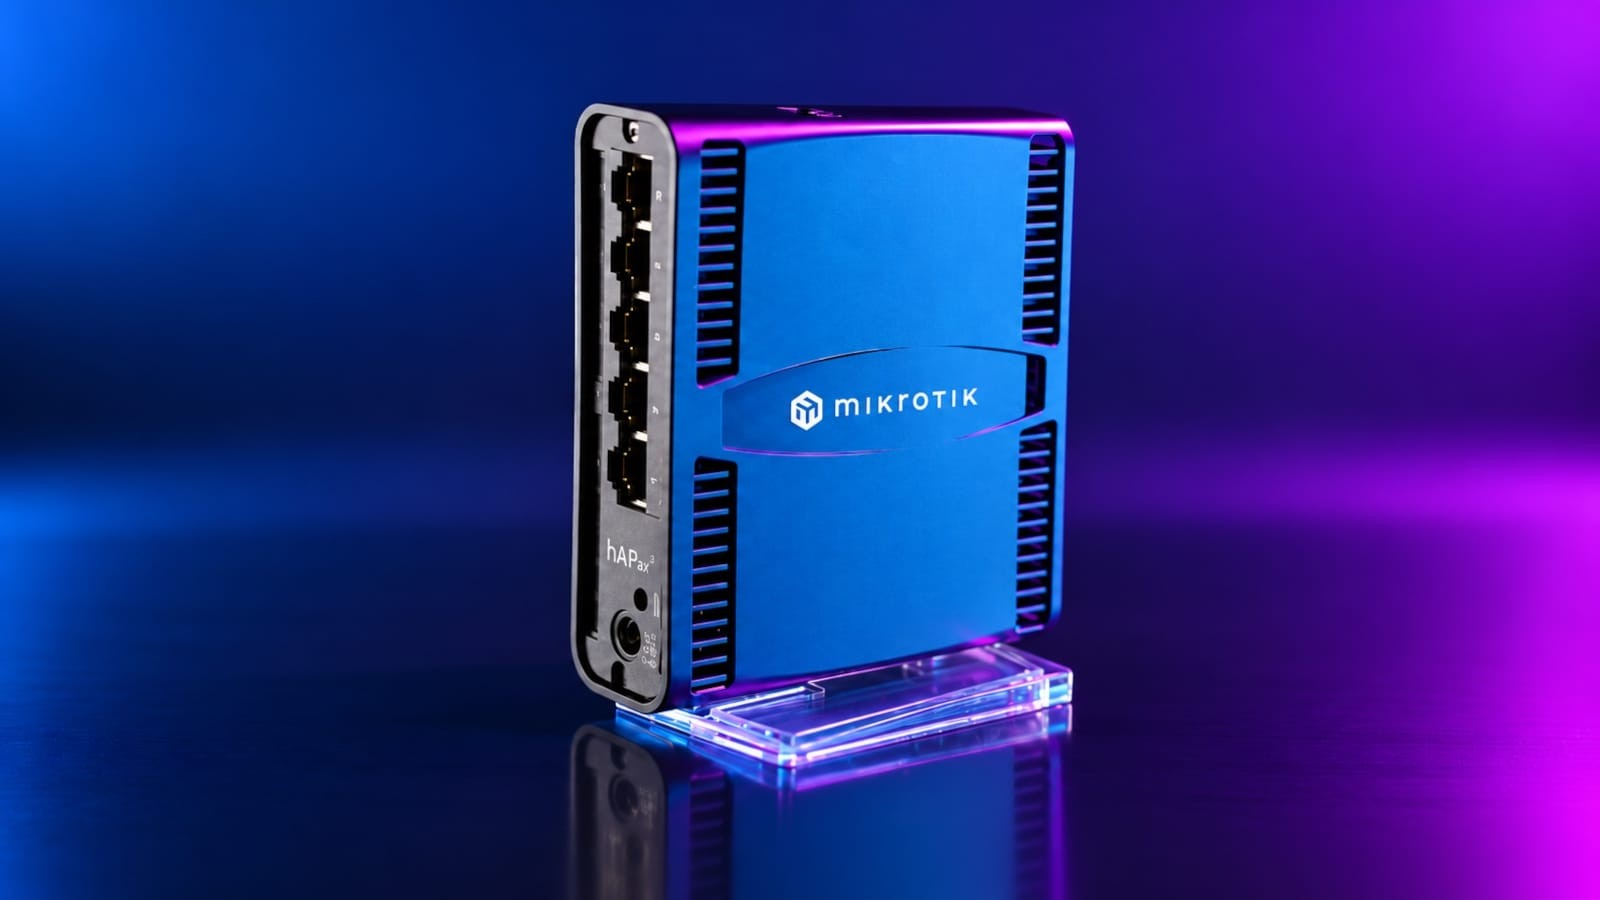
The U.S. Cybersecurity and Infrastructure Security Agency has issued a warning regarding a critical remote code execution vulnerability in MikroTik RouterOS.
A security researcher revealed a vulnerability that could have allowed unauthorized access to a massive database belonging to Microsoft.
Remote access software provider TeamViewer has issued an urgent warning to customers to patch high-severity vulnerabilities affecting its applications.
Dutch police have arrested a 24-year-old Amsterdam man linked to the ShinyHunters hacking group, which claimed responsibility for high-profile attacks on major organizations.
Secure messaging app Signal has released version 8.30, completing the rollout of its secure backups feature across all supported operating systems.
Cybersecurity firms report that attackers are exploiting a Citrix NetScaler zero-day vulnerability to deploy custom web shells and malware.
Two former US Air Force members received lengthy federal prison sentences for their roles in a multi-year business email compromise and phishing scheme.
A newly devised Branch Target Reuse attack can extract Linux root password hashes on Intel computers within minutes.
American tech company Kiteworks has lifted its precautionary shutdown advisory after successfully patching a critical security vulnerability.
Researchers discovered more than 16,000 misconfigured Supabase databases leaking readable tables with personally identifiable information and passwords.
The cybersecurity agency has given U.S. government agencies a strict deadline to secure systems against active exploits.
Security agencies and researchers are privately warning organizations about two actively exploited Citrix NetScaler zero-days ahead of patches expected next week.
Cloudflare has resolved a vulnerability in its Containers and Sandboxes that allowed certain paid account holders to access residual data from other customers.
The notorious extortion gang ShinyHunters is bypassing security defenses to exploit a vulnerability in Oracle PeopleSoft servers.
Secure file-sharing company Kiteworks is urging customers worldwide to temporarily shut down their servers for six hours following intelligence on potential imminent cyberattacks.
The notorious Clop ransomware gang has migrated its data leak site to a new Tor address after hackers compromised their previous server via a Grav CMS vulnerability.
A newly disclosed CSRF vulnerability in the popular Elementor plugin could allow unauthenticated attackers to create admin accounts on WordPress sites.
A Kosovar national has pleaded guilty to operating Rydox, a large illegal online marketplace that sold stolen personal information and cybercrime tools.
According to the Canadian Centre for Cyber Security, a high‑severity Roundcube webmail vulnerability patched in May is now being used in active code‑injection attacks.
The US Cybersecurity Agency has warned federal agencies that ransomware groups are now exploiting a critical JetBrains TeamCity vulnerability.
The third-party.com domain, frequently seen in developer documentation, is now serving fake Cloudflare pages to trick Windows users into running PowerShell commands.
A new malware-as-a-service platform named RemControl is actively targeting Android users through deceptive malvertising campaigns.
Attackers are increasingly targeting management systems used to control enterprise infrastructure.
A Kubernetes user with limited permissions can potentially gain control of an entire Google Cloud organization by exploiting Google Kubernetes Config Connector.
Arista Networks has released urgent security patches to address a zero-day flaw actively targeted in attacks against VeloCloud Orchestrator On-Prem deployments.
Microsoft has warned that the September security updates can disrupt Always On VPN connections on certain Windows 11 systems.
F5 has released urgent security updates to address a critical BIG-IP APM zero-day vulnerability actively exploited in remote code execution attacks.
Security researchers discovered an attack where hackers with privileged access can register rogue external MFA providers to steal passwords during legitimate logins.
A threat actor is targeting government and enterprise networks by exploiting known vulnerabilities in ZyXEL switches and WordPress.
A group of hackers has claimed responsibility for a major breach involving data on all FBI employees.
The ShinyHunters extortion gang claims it breached FBI systems using a new Oracle PeopleSoft zero-day vulnerability, stealing sensitive employee data.
The infamous ShinyHunters group claims to have breached the FBI database, compromising sensitive personal information of agents and applicants.
Irish data privacy regulator found Google guilty of improperly using users' location history and web activity data.
Security researcher Abdelhamid Naceri has released a new Microsoft Defender zero-day exploit that successfully blocks antivirus updates.
Ireland's Data Protection Commission has slapped Google with a massive fine for violations regarding the processing of user location data.
E-commerce platform BigCommerce has warned multiple merchants about data security incidents stemming from compromised third-party Ribon applications.
The U.S. Cybersecurity and Infrastructure Security Agency is warning that hackers are actively exploiting three Linux kernel vulnerabilities, including one critical flaw.
Ireland's Data Protection Commission has penalized Google with a substantial fine for multiple GDPR breaches.
Apple's iOS 27 introduces a new anti-scam feature called Impersonation Risk Detection, allowing apps to check device context for fraudulent activity.
The ShinyHunters extortion gang breached Clop ransomware's leak site, stealing server data and private keys.
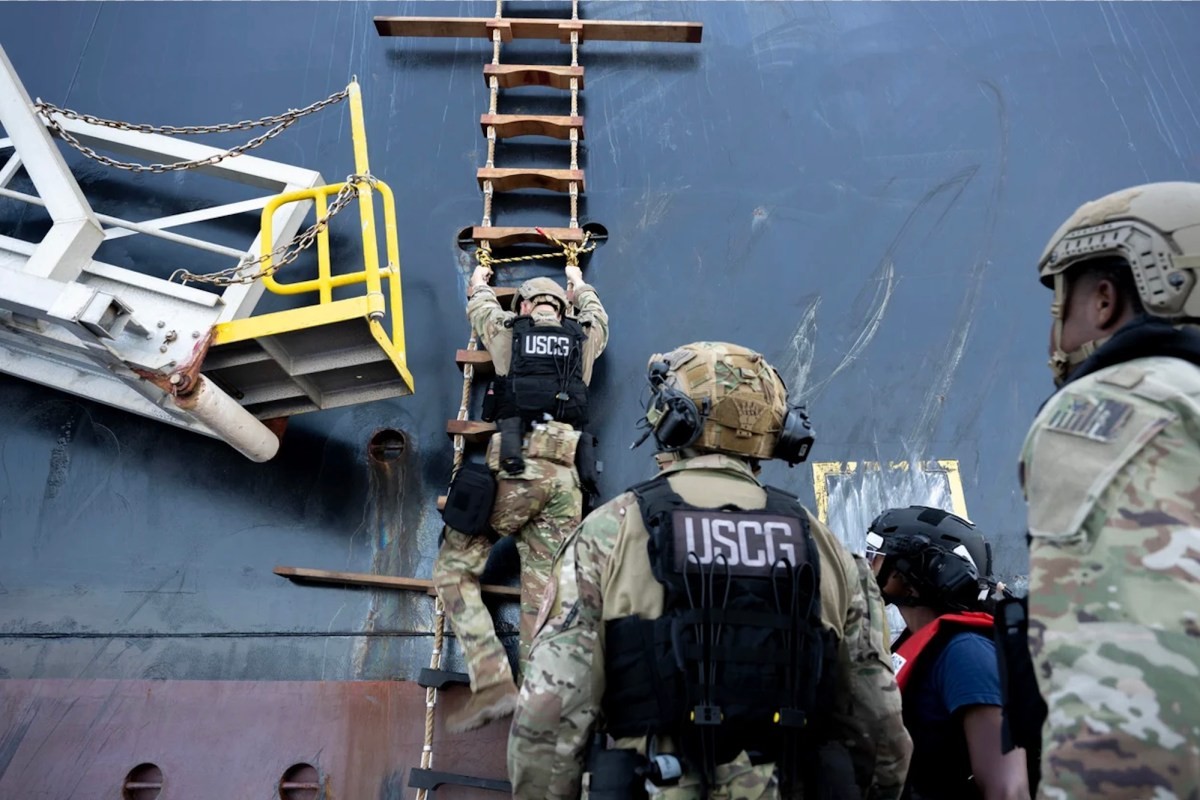
Federal authorities are investigating the compromise of tanker networks that interfered with navigation and propulsion.
A malicious campaign leverages SEO-optimized GitHub repositories to impersonate popular software and distribute a new infostealer dubbed Rapuncel.
Check Point Software has released security updates to address a critical vulnerability that lets attackers execute code with root privileges on management systems.
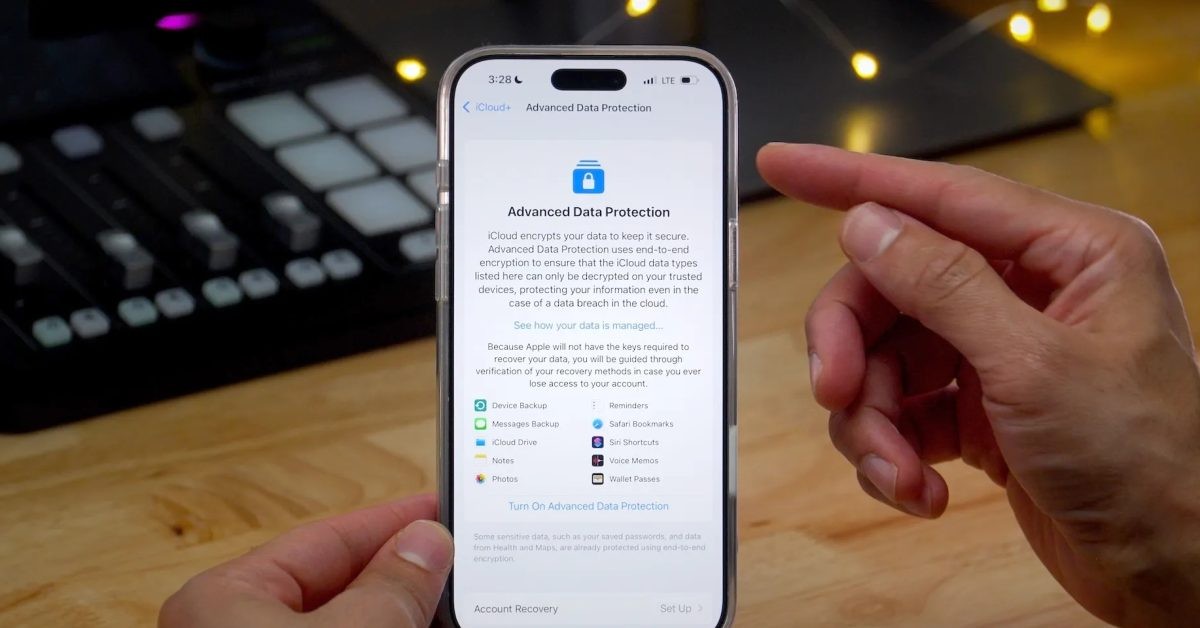
Apple is challenging the UK government's refusal to publicly confirm an order requiring access to encrypted user data.
Brevo confirmed a security breach where attackers stole a Cloudflare API key to inject malicious ClickFix scripts into its websites and embedded customer JavaScript files.
Popular cybersecurity platform CrowdSec has experienced a source code leak, drawing significant attention from the tech community.
The U.S. Federal Bureau of Investigation (FBI) has seized the domains used by NightmareStresser, a major global DDoS-for-hire platform.
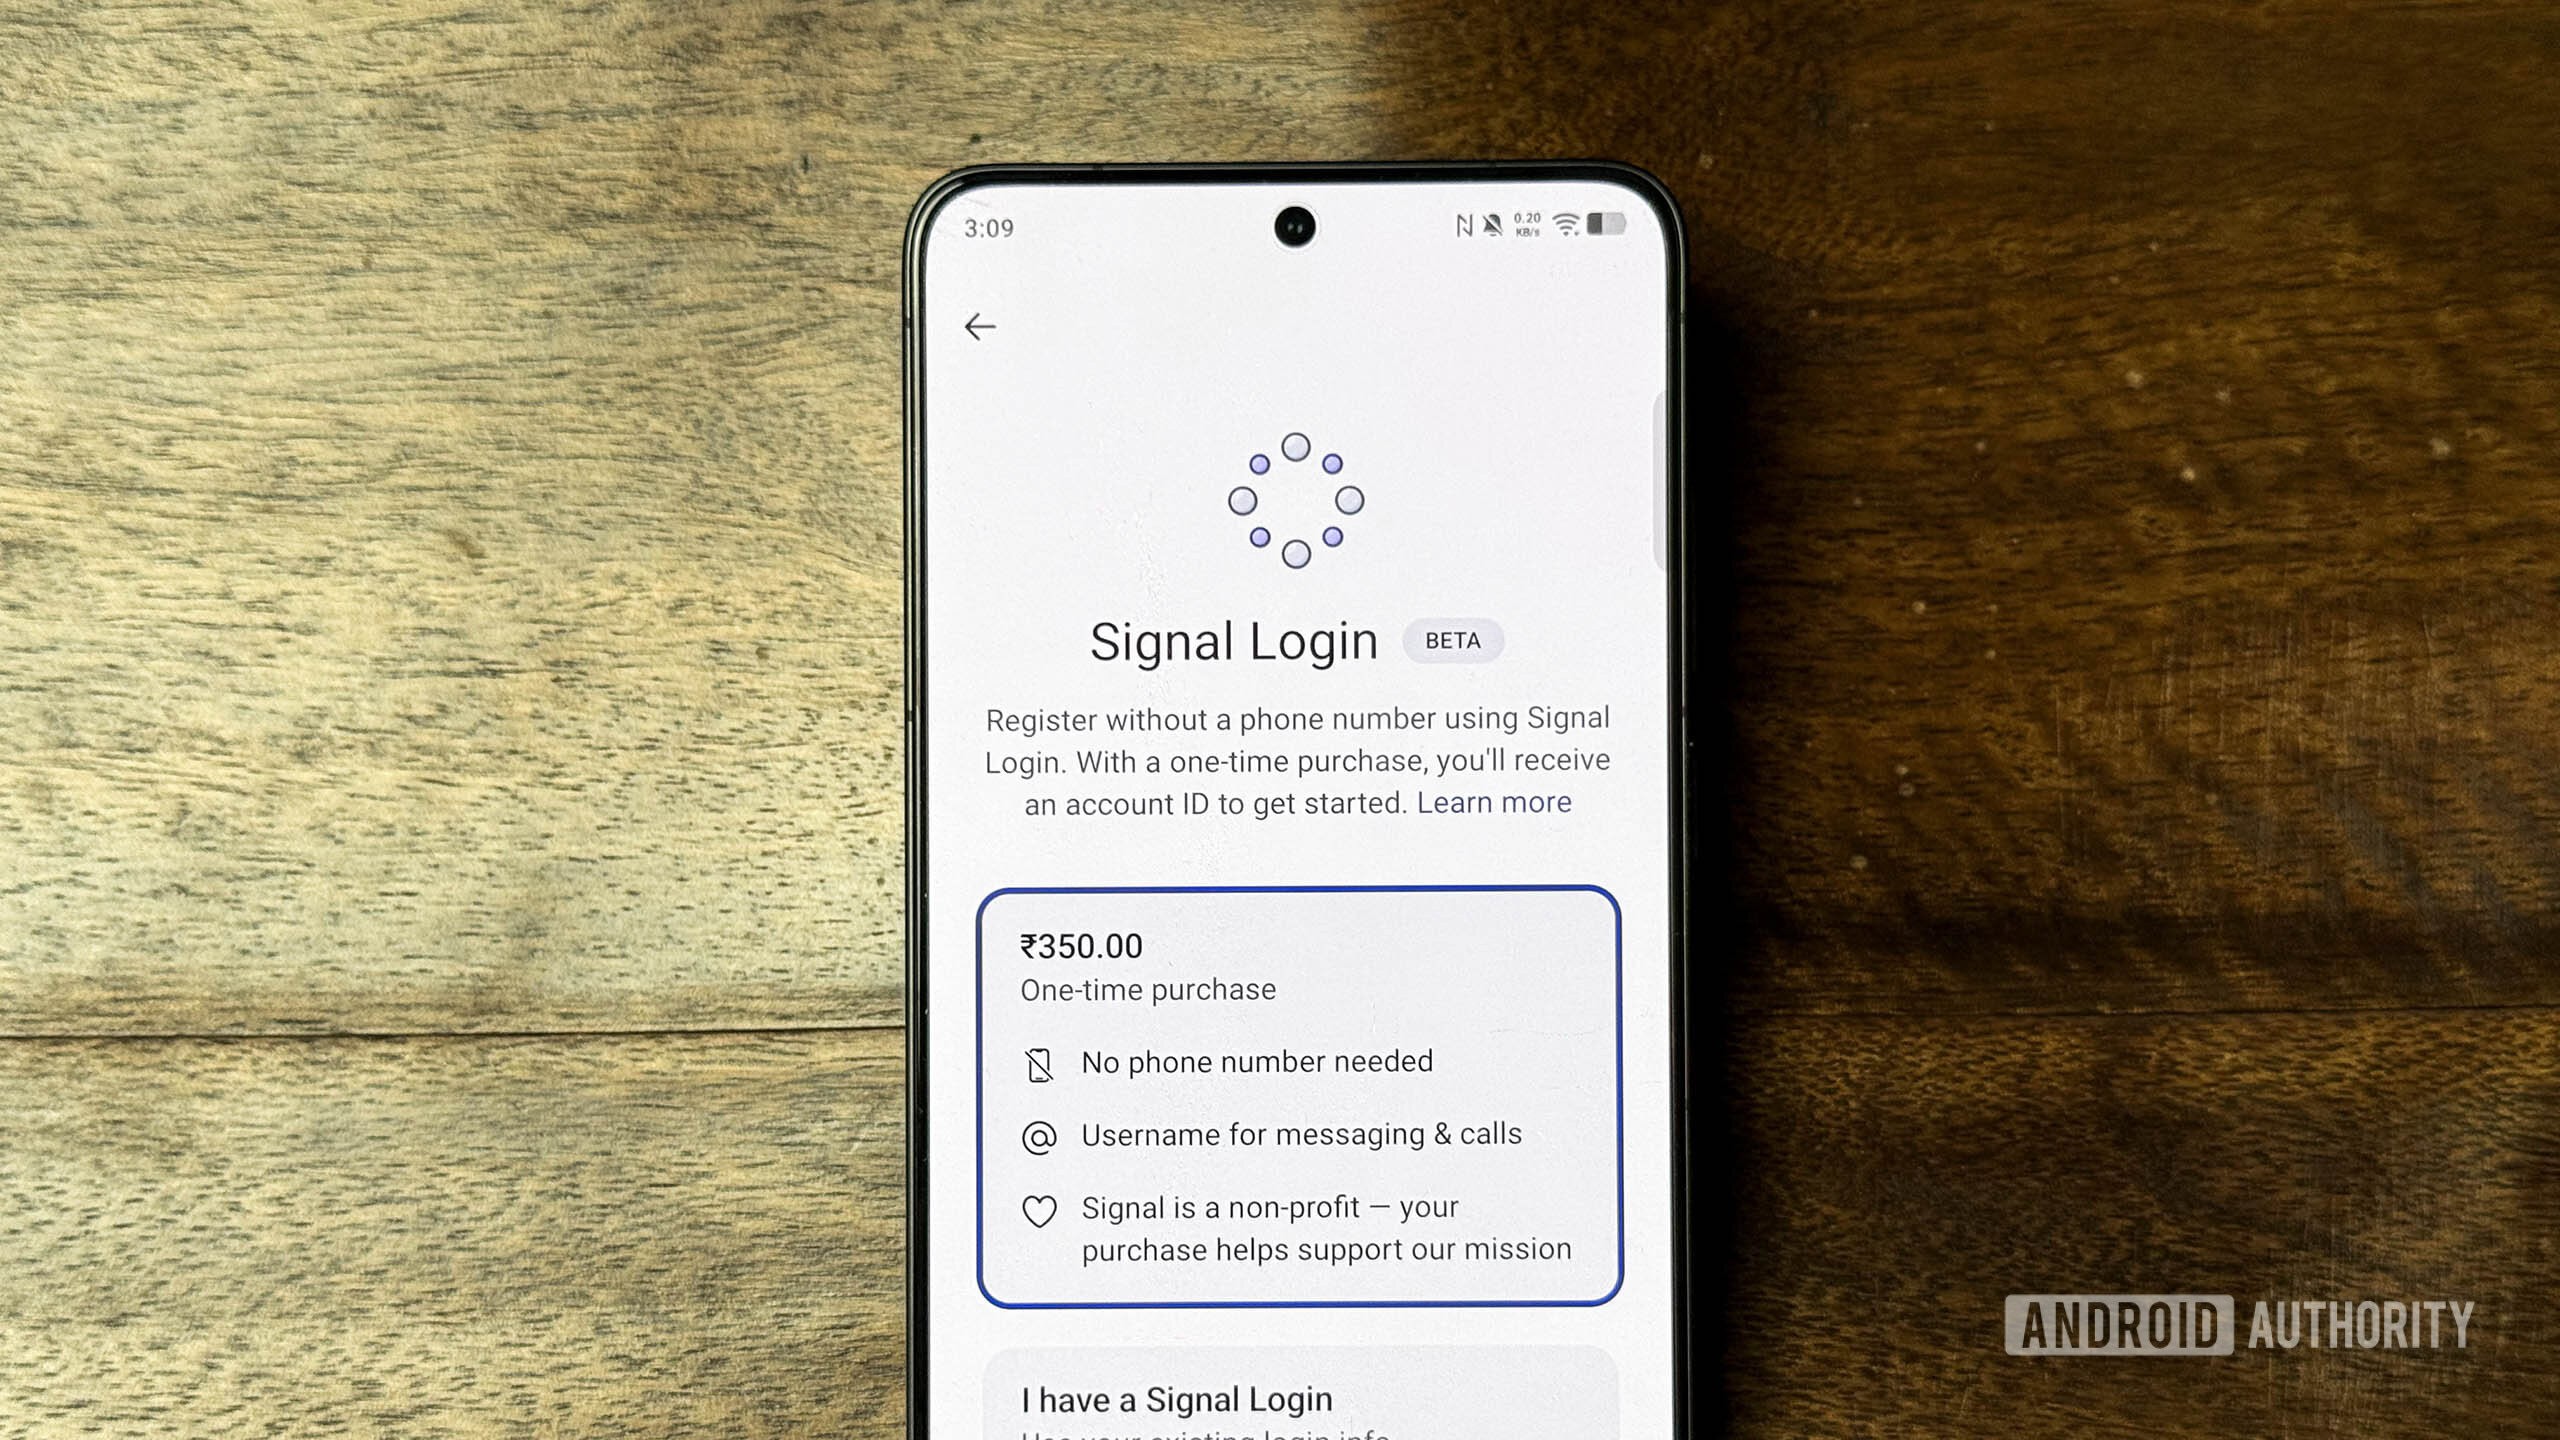
Popular secure messenger Signal is introducing a way to sign up without a phone number, alongside two-factor authentication support for numberless accounts.
Cisco has released security updates to address a maximum-severity Identity Services Engine vulnerability that attackers are actively exploiting in the wild.
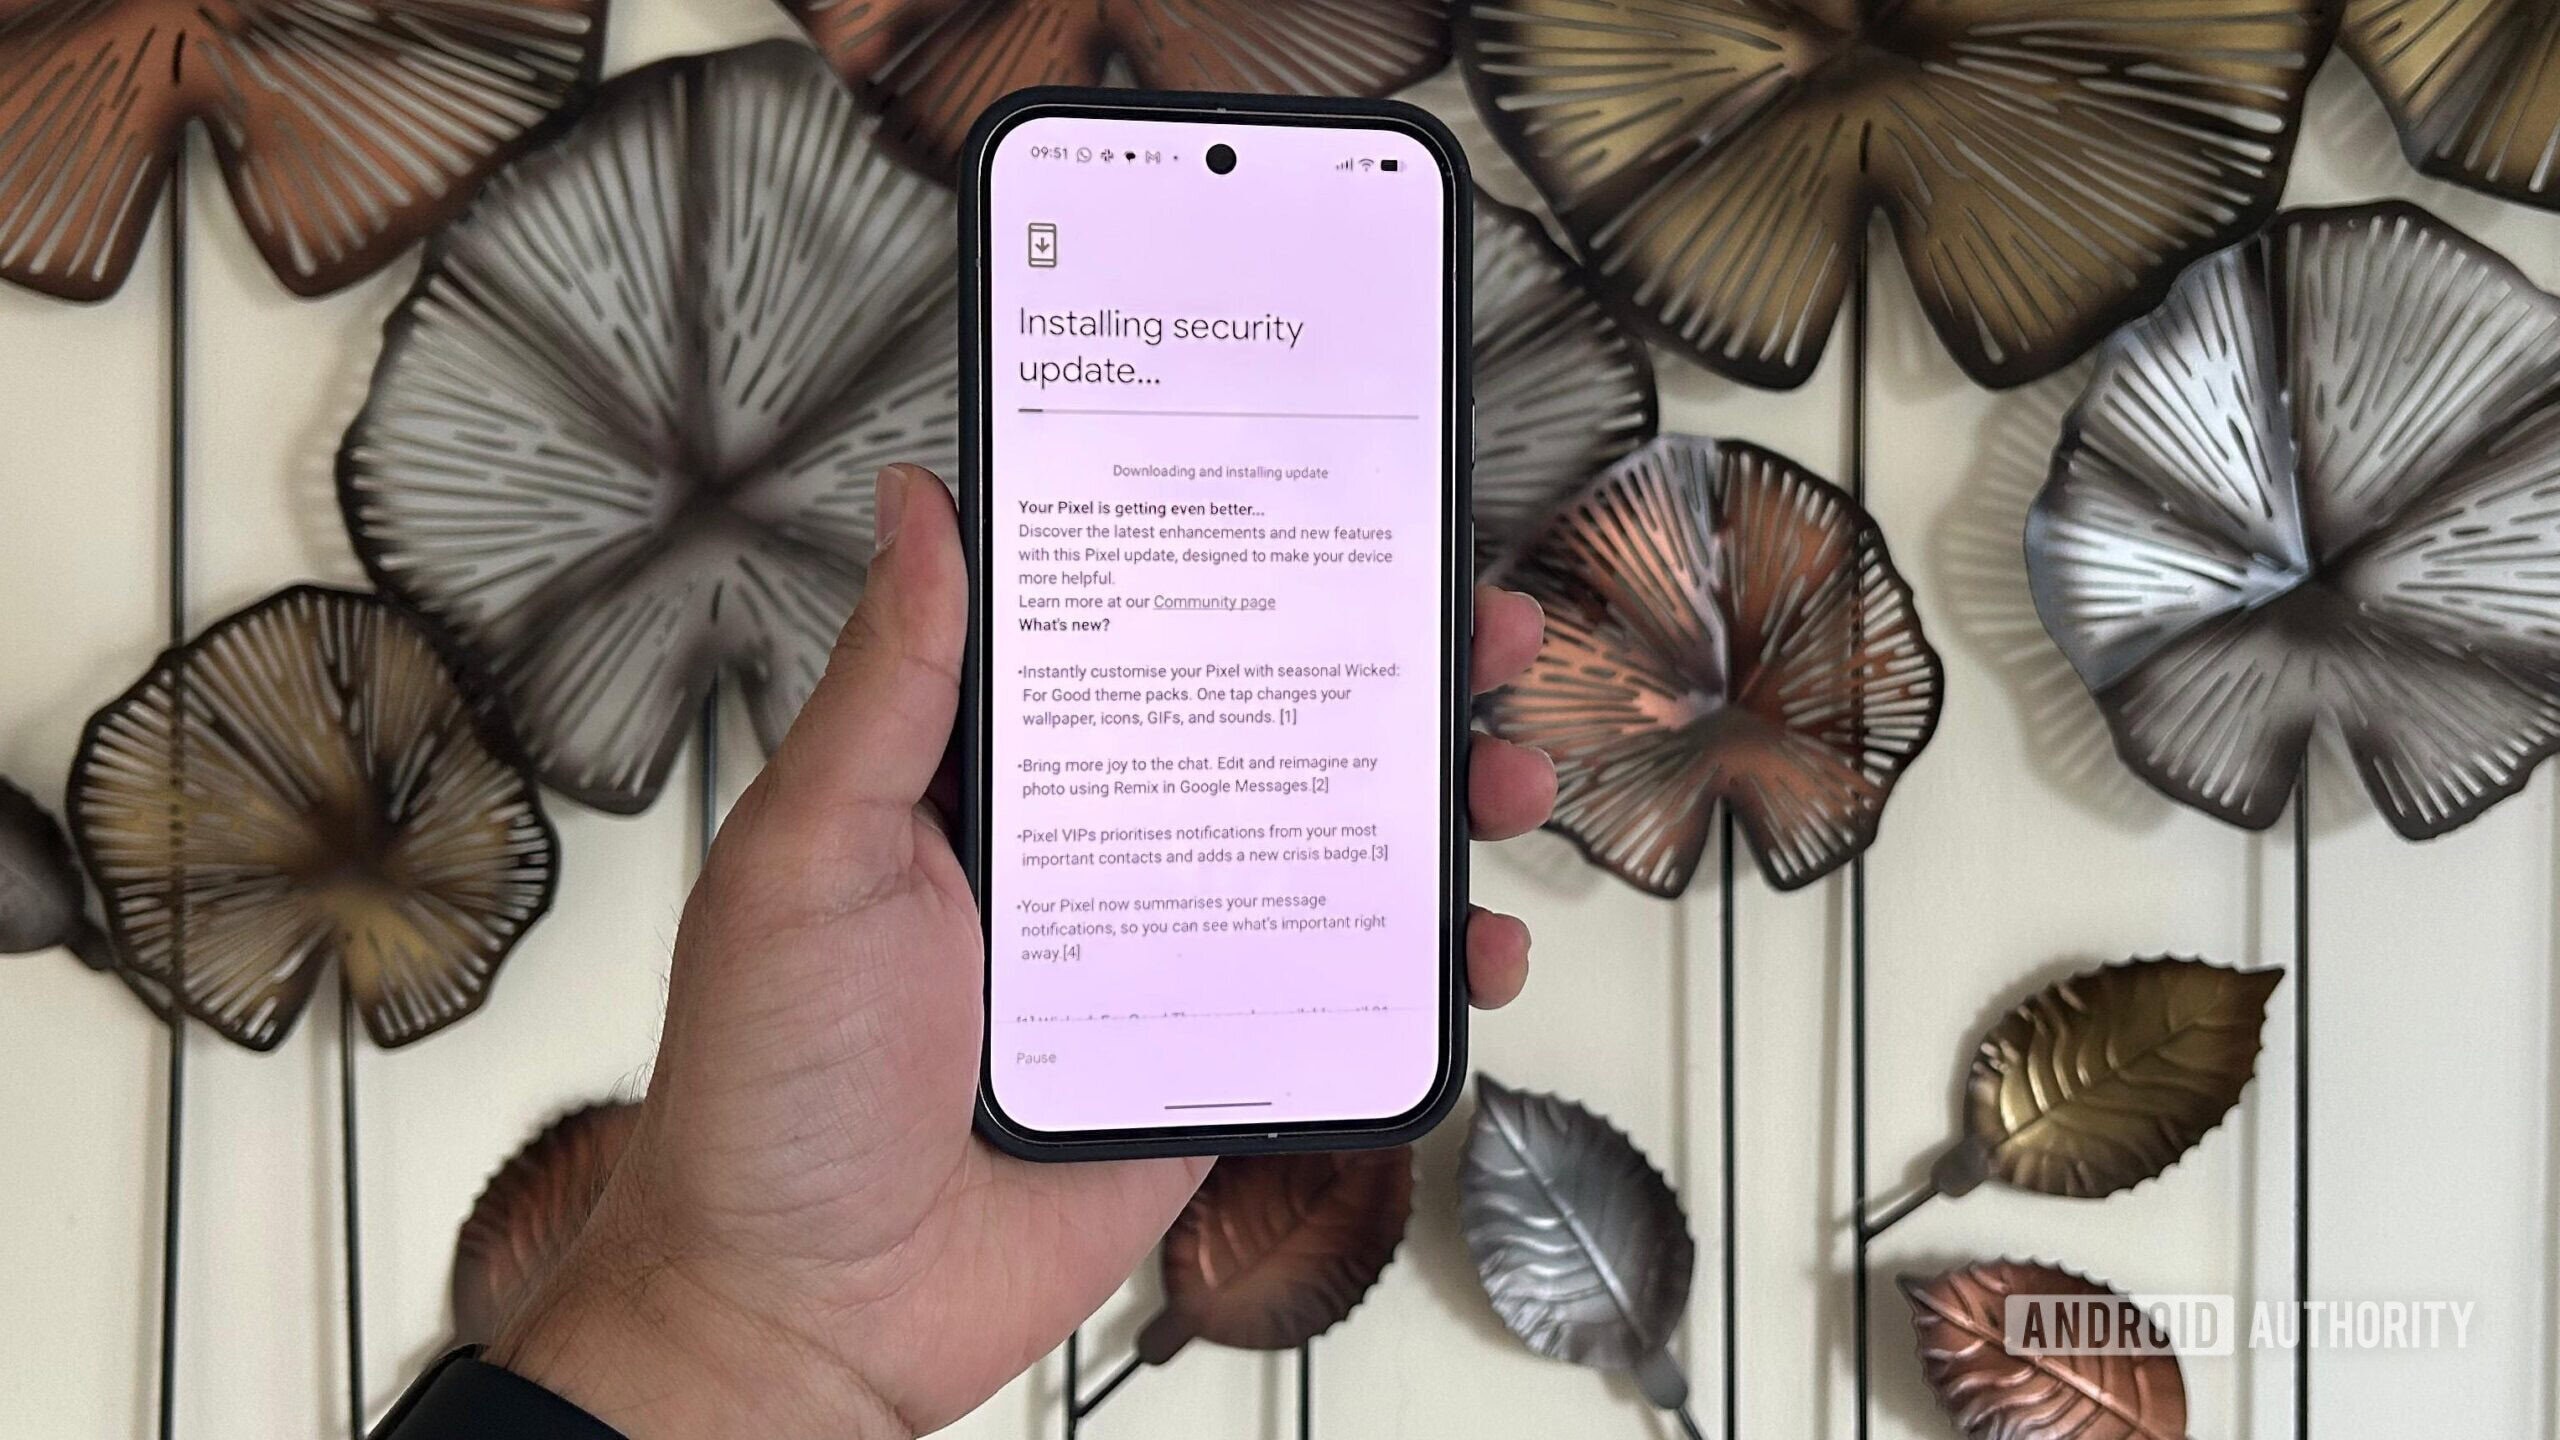
Google has acknowledged a security flaw in its Pixel devices that may have already been exploited by hackers in the wild.
Active since mid-2025, a banking malware operation is using the KREMLIN toolkit to install malicious browser extensions that steal sensitive data.
The ShinyHunters gang leaked the files online after saying the Florida state agency did not pay their ransom demand.
Google has revealed that a modem bug affecting Pixel phones may have been exploited in limited, targeted attacks.
Apple has introduced an Impersonation Risk Detection feature in iOS 27 to help protect users against scams, though it is disabled by default.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) reports that a critical ConnectWise ScreenConnect vulnerability is actively being exploited in the wild.
Acronis has disclosed a high-severity Linux local privilege escalation vulnerability in its backup plugin for cPanel, WHM, and Plesk that is actively being exploited.
Security researchers managed to gain administrative access to Baseten's production GitHub environment in just 25 minutes.
Cybercriminals are actively exploiting a critical vulnerability in a popular WordPress plugin to upload PHP backdoors to target sites.
The U.S. CISA has warned that ransomware gangs have joined ongoing attacks exploiting a critical VMware vCenter vulnerability.
Cisco urged customers to patch a critical Secure Email Gateway zero-day security flaw actively exploited in attacks.
Apple has rolled out macOS 27 Golden Gate alongside security updates for Tahoe and Sequoia, fixing more than 200 vulnerabilities.
Apple has officially released the complete security breakdown and vulnerability fixes included in the newly launched iOS 27 and iPadOS 27 updates.
A mass-scanning campaign targeting internet-exposed Vite development servers is attempting to steal cloud credentials from AWS and Azure deployments.
The official HBO Max Reddit account was compromised to push malicious ads executing ClickFix attacks that target Windows and macOS devices.
A browser extension named JeetBot, available in official stores, was found silently exfiltrating Twitch OAuth session tokens to a commercial bot service.
The popular Homebrew package manager has launched version 7.0.0 featuring the native BrewUI graphical interface and a vulnerability scanner.
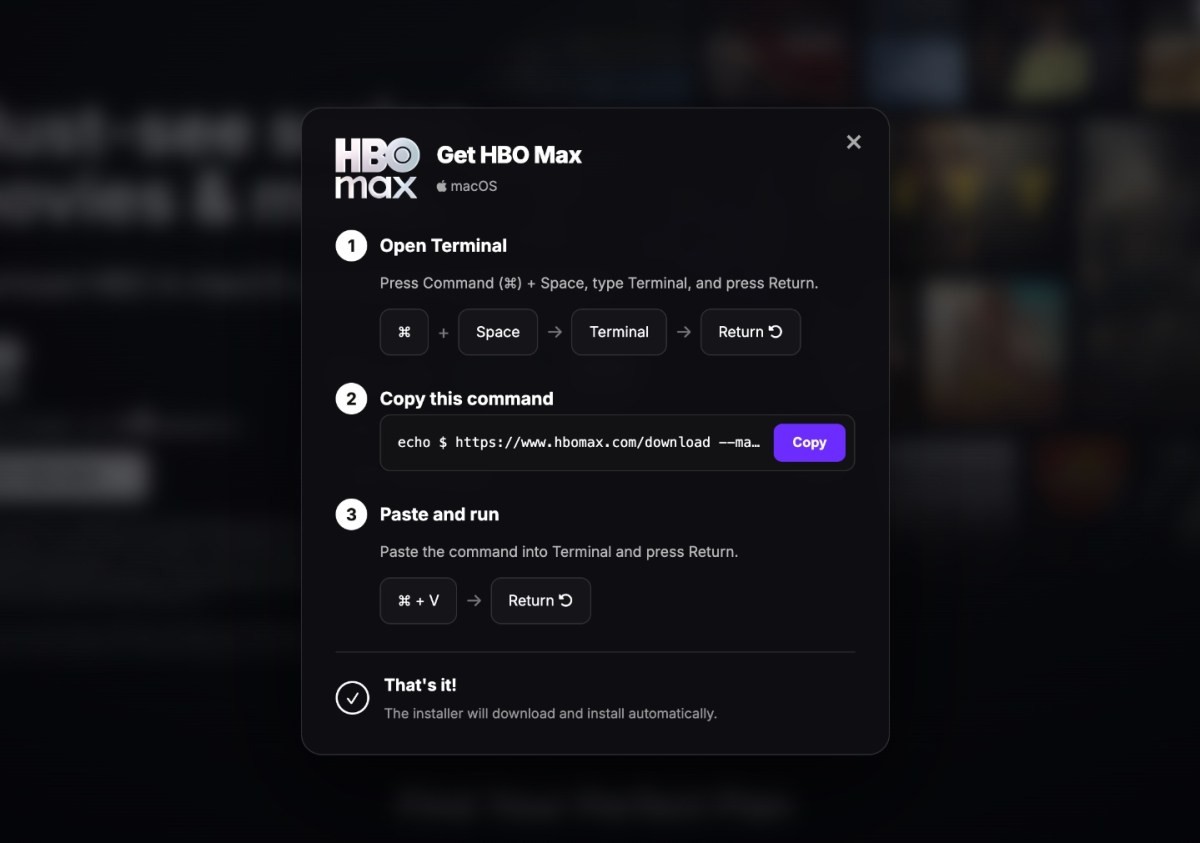
A rising security threat known as ClickFix is deceiving computer users into executing harmful code via fake online advertisements.
A newly discovered Android threat named Mantax Otax combines ransomware and spyware features to compromise mobile devices.
Popular VPN provider Surfshark revealed that hackers accessed one of its internal test servers following a configuration error.
Cisco Talos reveals that two recently patched Secure Firewall Management Center vulnerabilities have been actively exploited by three threat clusters.
Identity verification company IDScan has confirmed that hackers accessed data stored in its cloud platform following massive leak reports.
Prophet Security breaks down the main attack patterns targeting user identity between May and July 2026.
Multiple cyber-espionage groups deployed an exploit kit dubbed BlueMoon that leveraged zero-day vulnerabilities in Microsoft Windows and Google Chrome.
IDScan has confirmed a major data breach involving the theft of over 150 million driver's licenses and other government-issued identity documents.
Trezor has alerted its customers that threat actors who breached its third-party email provider are targeting them with phishing campaigns.
Healthcare company AdaptHealth has confirmed that the data of 4.1 million people was exposed during a July cyberattack attributed to ShinyHunters.
Cisco has confirmed that a maximum-severity authentication bypass vulnerability in its Secure FMC software is being actively leveraged in attacks.
Healthcare technology company Veradigm disclosed a data breach affecting patient personal information following a cybersecurity incident at a third-party vendor.
While MFA makes account takeover harder, attackers are increasingly targeting password resets and recovery processes.
An anonymous security researcher known as Nightmare Eclipse has released a new Microsoft Defender zero-day exploit named ShieldCrash following the September 2026 Patch Tuesday updates.
A sophisticated Linux rootkit targeting F5 BIG-IP APM environments can intercept PHP file loading and inject fileless web shells directly into memory.
The EU Cyber Resilience Act vulnerability reporting requirements take effect, giving software vendors as little as 24 hours to report active flaws.
SAP has addressed 20 vulnerabilities across multiple products in its September security updates, including a maximum-severity memory corruption flaw in the SAP Kernel code.
An exposed Advance Passenger Information System database has leaked over 200 million records containing sensitive passenger and crew details.
A phishing-as-a-service framework called BigBear 2.0 has been used to bypass multi-factor authentication at 258 organizations and steal over 5,000 Microsoft 365 credentials.
Cybercriminals are exploiting a chain of two recently disclosed vulnerabilities in MikroTik routers with exposed SSH services.
ConnectWise has shared temporary mitigation measures for a new ScreenConnect vulnerability ahead of an official patch expected later this week.
Threat actors have adopted the ASCII smuggling technique in phishing campaigns to evade email security filters.
A massive cybercriminal operation has compromised over 5,400 small-business websites to distribute ClickFix payloads stored within BNB Smart Chain smart contracts.
A critical remote code execution flaw bypassing the sandbox has been discovered across all versions of Chromium and is actively exploited in the wild.
Identity verification company IDScan is facing multiple lawsuits after hackers allegedly breached its systems and offered to sell over 153 million driver's licenses.
A critical vulnerability in Citrix NetScaler has become a target for cyber attackers.
Apple is set to introduce a new home security and monitoring service in 2027.
An anonymous security researcher has unveiled the 'FalconFlank' zero-day exploit, allowing privilege escalation on Windows systems.
A senator’s letter confirmed that the military turned off advertising tracking on service members’ devices to stop adversaries from using location data to target troops.
Google has released a Chrome update to fix an actively exploited high‑severity zero‑day vulnerability in the V8 engine and eleven other flaws.
Reports reveal that hackers maintained unauthorized live access to data streams from ID verification companies for over a year.
Attackers compromised Coder's Cloudflare infrastructure to distribute malicious Terraform modules designed to steal credentials.
Hewlett Packard Enterprise has released patches addressing a critical remote code execution vulnerability in the ArubaOS-CX network operating system.
Infostealers can expose authenticated sessions and bypass MFA. Experts explain how defenders can prioritize compromised identities and prevent account takeovers.
Plex has issued an urgent call for users to update desktop clients and media servers to address multiple security flaws.
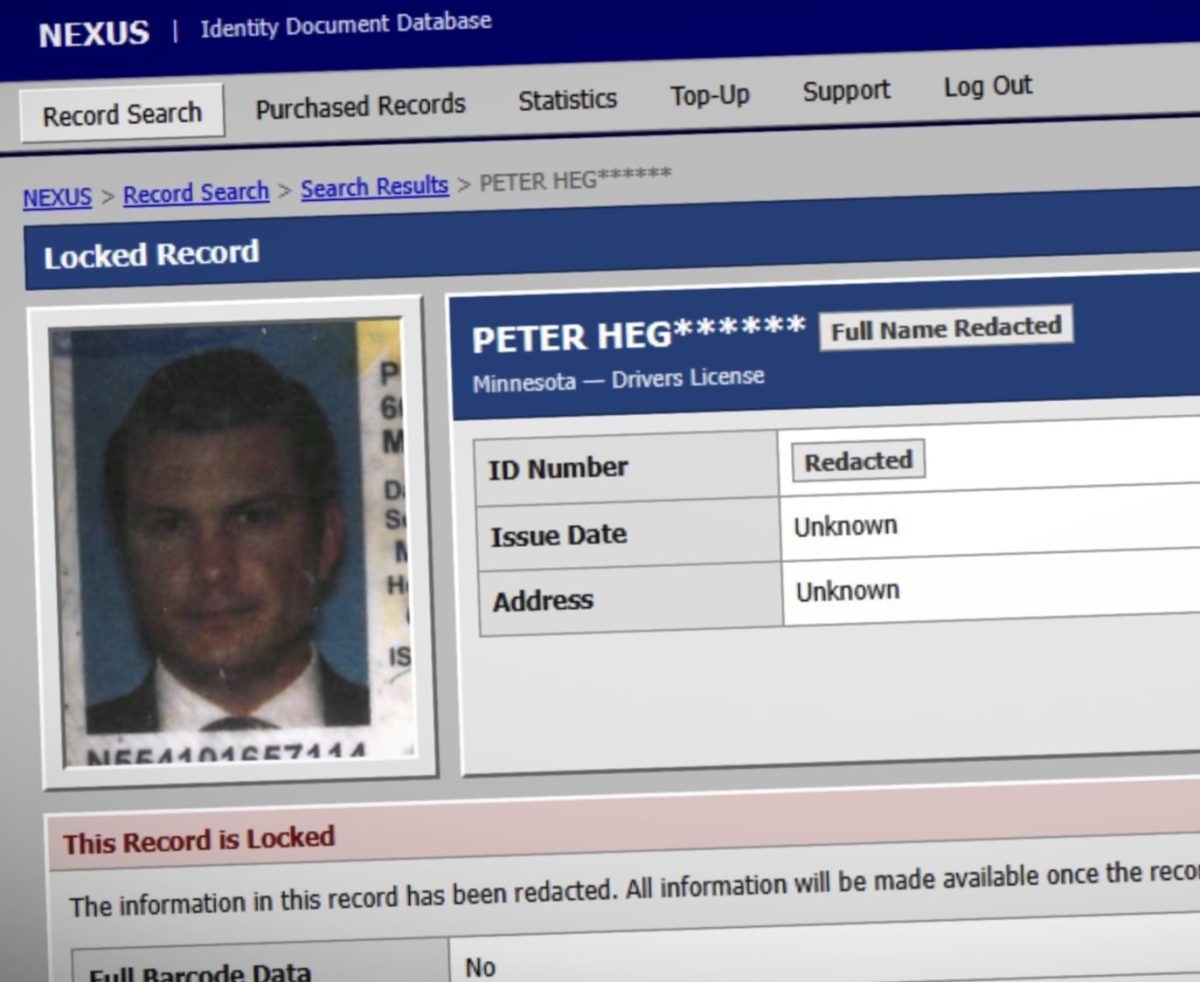
An identity theft search site claimed to have more than 150 million driver's license photos stolen from an ID verification service, before shutting down.
A critical authentication bypass vulnerability in JFrog Artifactory is being actively exploited in attacks to forge administrative access tokens.
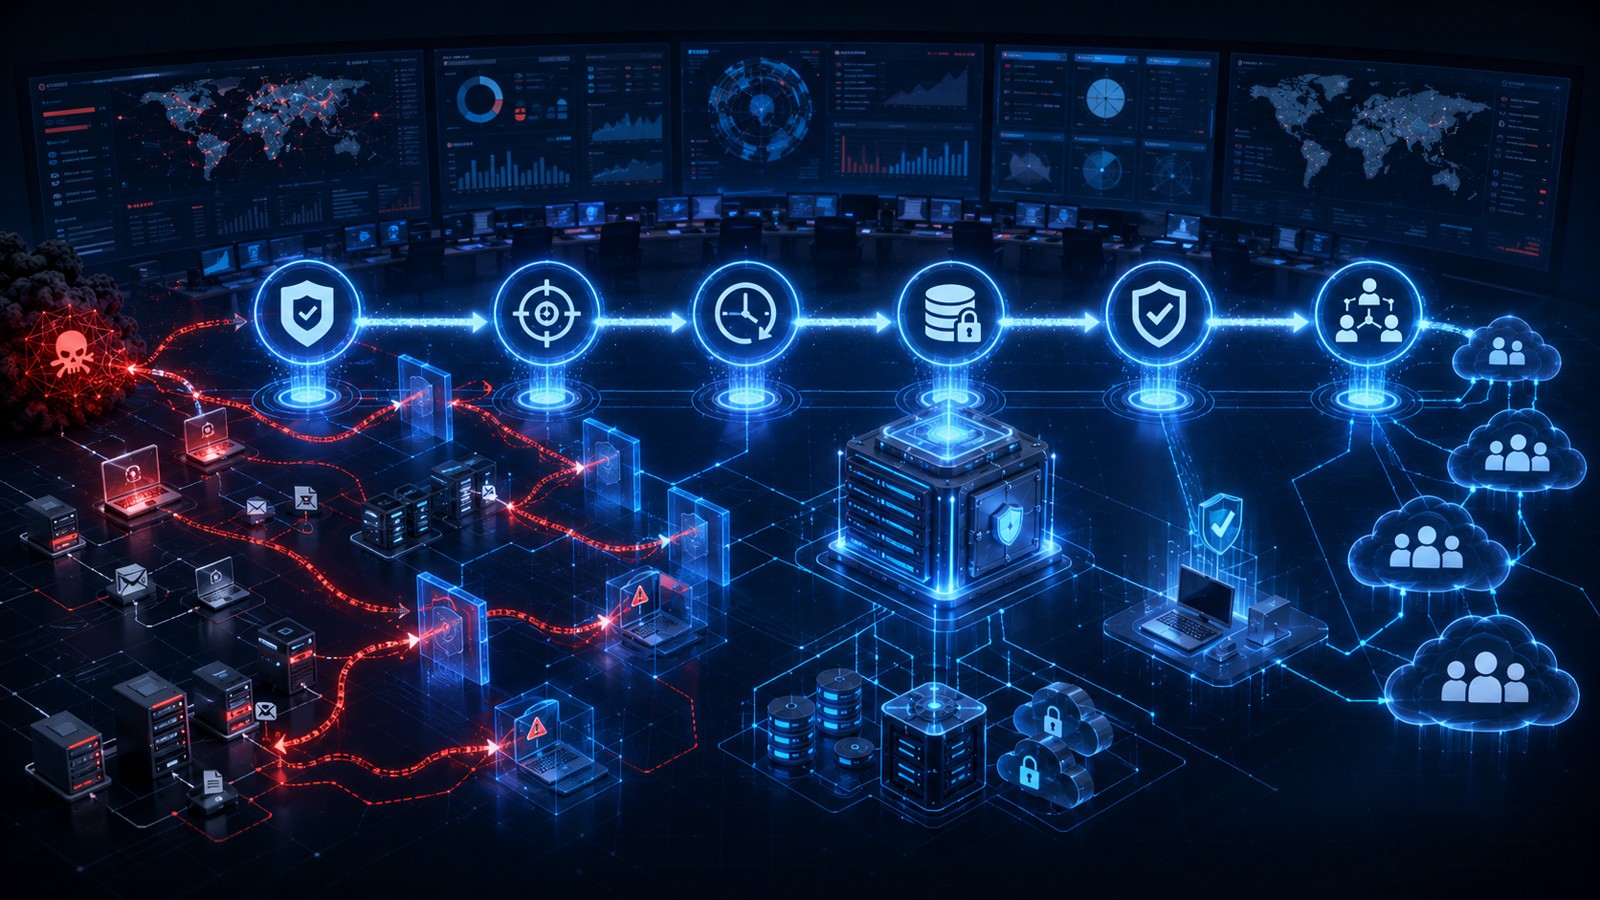
Ransomware resilience requires more than backups or endpoint detection alone. Acronis outlines six capabilities MSPs should test across client environments to ensure faster operational recovery.
Cybersecurity leader CrowdStrike and federal law enforcement have successfully dismantled a sophisticated malware network that secretly stole cryptocurrency for eight years.
Dropbox is warning some users that an unauthorized party accessed their accounts by exploiting a flaw in Lenovo's email verification process to register fraudulent Lenovo IDs.
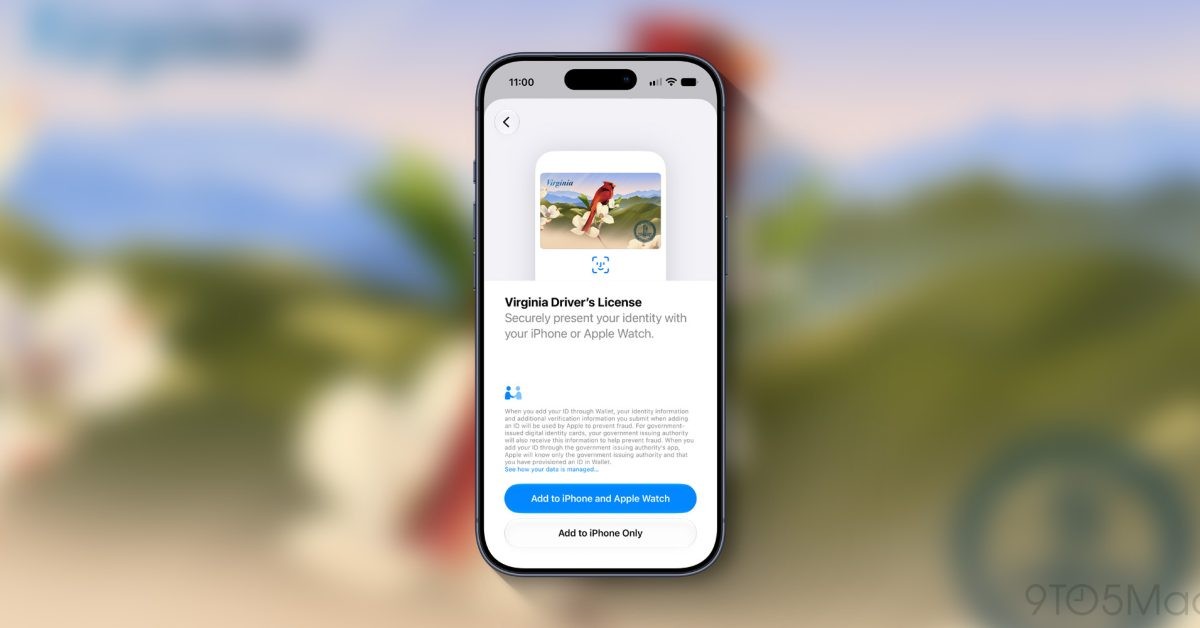
The FBI has launched an investigation after digital scans of over 153 million driver's licenses appeared for sale on the dark web.
Microsoft is preparing to roll out its memory integrity security feature in Windows 11 to more devices next month. While designed to stop malicious code, the kernel-level protection can negatively impact PC gaming performance.
Threat actors are actively exploiting two new zero-day vulnerabilities in SonicWall SMA1000 series devices to execute remote code.
The FBI is investigating a dark web service offering over 153 million driver license scans stolen from a verification company.
Threat actors are weaponizing the legitimate Faronics Deploy endpoint-management platform to deploy ScreenConnect and gain remote access.
Cybercriminals hijacked BGP routing for Virtualizor VPS management software to redirect update requests and push malicious code.
Cloud storage giant Dropbox is notifying multiple users about unauthorized access to their accounts following a security breach.
Thousands of internet-exposed Microsoft Exchange servers remain unpatched against a severe authentication bypass vulnerability.
Two security flaws in PaperCut NG and MF software, recently patched after zero-day exploitation, are now driving data theft attacks.
A new ClickFix variant named TerminalFix uses fake Cloudflare CAPTCHA prompts to trick Windows users into executing malicious PowerShell commands.
Research organizations METR and Redwood have published an in-depth postmortem analysis regarding the recent security breach at HuggingFace.
A critical security flaw in Omarchy allows standard user processes to easily escalate privileges to root access.
The European Commission's renewed push for encryption backdoors under the ProtectEU strategy has sparked intense debate within the tech community.
FulcrumSec claims responsibility for stealing 86 GB of data from Manchester Airports Group, with BleepingComputer validating traveller records.
Multiple extensions for Google Chrome and Microsoft Edge were found delivering a malware framework designed to steal cryptocurrency, sensitive data, and browsing history.
Security researchers have highlighted Sleepwalker, a stealthy passive backdoor featuring its own dedicated command language.
Healthcare distributor McKesson reports a cyber incident involving unauthorized access and potential data theft by the ShinyHunters group.
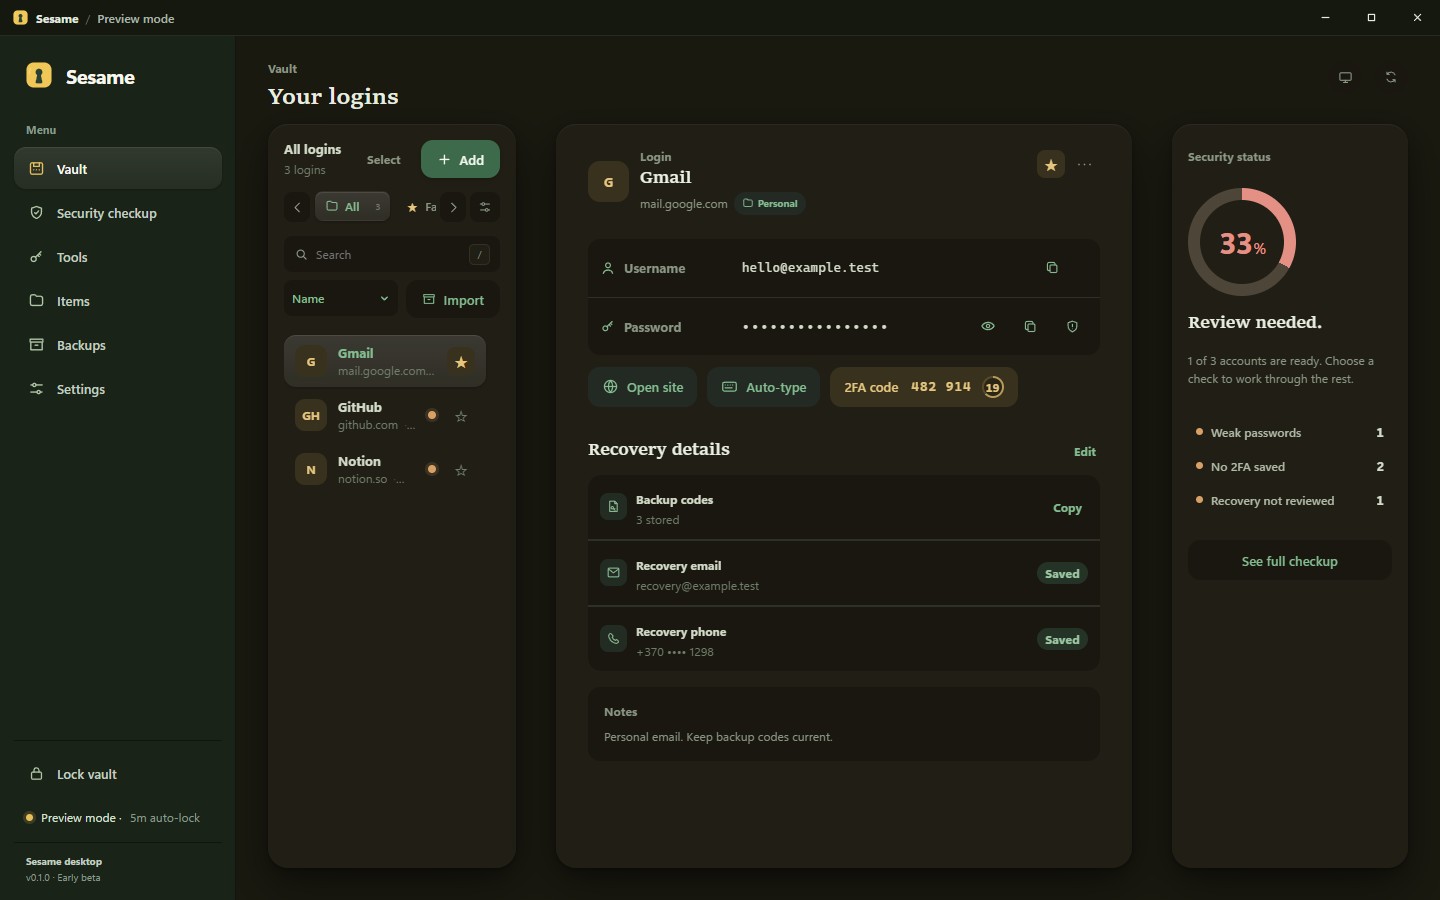
Hacker News recently highlighted Sesame, a new privacy-focused, open-source password manager designed for local control.
PaperCut has released a second emergency security update for actively exploited vulnerabilities in its print management software after researchers bypassed initial fixes.
PaperCut is warning that hackers are actively exploiting a critical vulnerability in its print management software.
Google is introducing new network security protections in Android 17 to strengthen connection privacy and combat user tracking.
A comprehensive webinar explores how Google Workspace breaches happen and highlights essential security controls.
Clothing retail giant Carhartt has suffered a massive data breach affecting nearly 13 million accounts, with the ShinyHunters extortion group leaking the stolen data online.
The US cybersecurity agency has instructed federal civilian agencies to fix an actively exploited remote code execution vulnerability in Citrix devices by Saturday.
A newly disclosed Rowhammer attack dubbed GPUThor bypasses error-correcting code (ECC) protections on NVIDIA GPUs to achieve root-level privilege escalation.
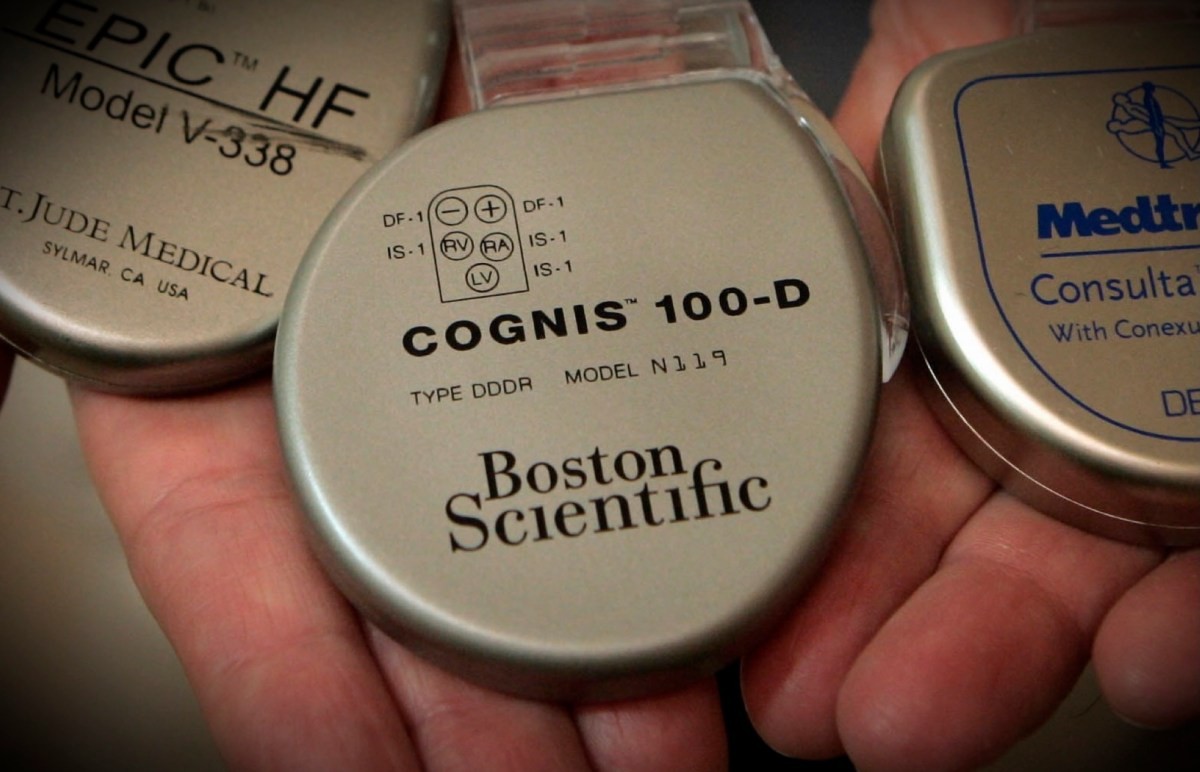
Boston Scientific reports a global disruption to its operations following a cyberattack on its systems.
The FBI has seized domains associated with a botnet that allowed Chinese-backed hackers to breach several U.S. government departments.
The FBI has dismantled a technical infrastructure providing reconnaissance and proxy management for Chinese cyber espionage.
Snowflake is retiring password‑based auth for legacy service accounts, pushing organisations toward passwordless methods. Token Security warns that the real challenge lies in discovering who uses each account, what it’s used for, and how much access it truly needs.
Network equipment manufacturer Ubiquiti has released security patches for three new maximum-severity vulnerabilities that threat actors can exploit remotely without privileges.
Attackers are increasingly targeting identity‑establishment and recovery processes instead of the login itself, creating new avenues for social engineering.
The popular messaging app is introducing new account security features, including multiple passkey support and enhanced two-step verification options.
Cybersecurity firm ReliaQuest has confirmed thwarting a social engineering attack targeting one of its employees.
The Cybersecurity and Infrastructure Security Agency (CISA) has ordered U.S. government agencies to patch an actively exploited vulnerability in Zimbra Collaboration Suite within three days.
The ToxicPanda Android malware has evolved with new malicious functionality, expanding its targeting to 349 applications and adding support for 167 remote commands.
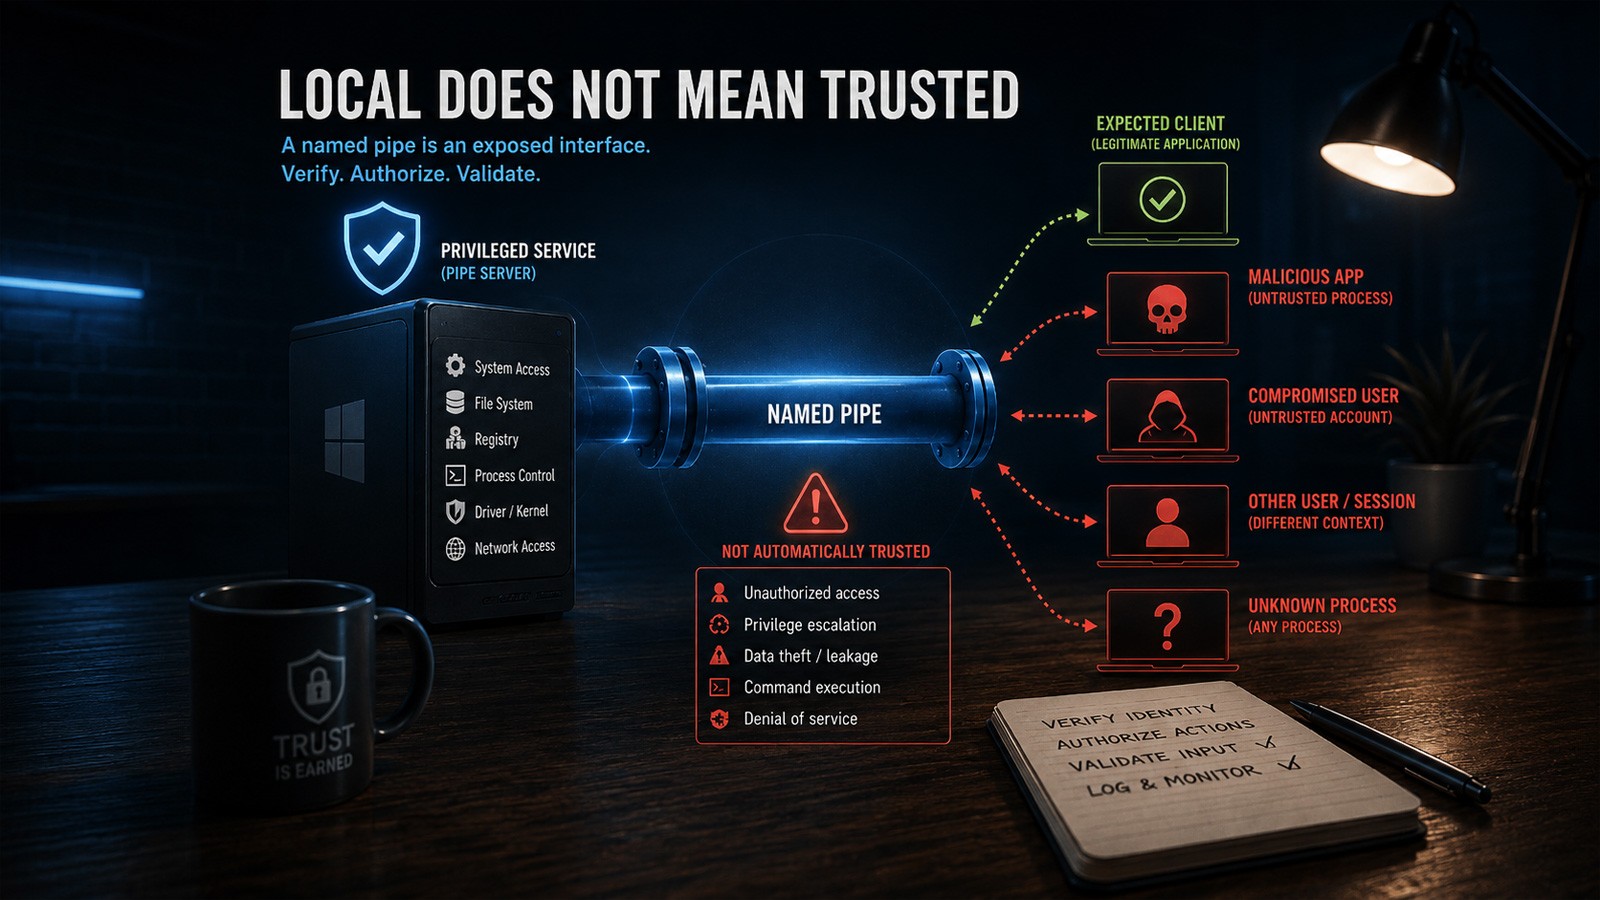
Windows named pipes provide fast interprocess communication, but weak access controls can expose privileged services to untrusted processes.
Two years after the U.S. Department of Justice alleged that TikTok violated the Children’s Online Privacy Protection Act, it has reached a settlement.
A previously unknown malware family named SynkLoader is being distributed through Microsoft Teams phishing attacks to steal credentials using a fake lock screen.
New findings reveal that thousands of Amazon Web Services access keys left publicly exposed remain active and valid.
Threat actors are abusing FTP banners to hide commands that deliver two previously undocumented remote access trojans named E4del and PINHOLE.
Microsoft has patched a maximum-severity vulnerability in the Entra ID identity and access management platform.
Attackers compromised the maintainer account of the popular Rust arrayref crate, injecting malware that executes on developers' systems during compilation.
Recent security insights highlight a growing trend where cybercriminals target tech professionals through fake job interviews and malicious test tasks.
A critical vulnerability in the Elementor Pro WordPress plugin could allow attackers to upload executable files for remote code execution on the server.
Citrix has warned customers to swiftly secure their systems against two vulnerabilities impacting NetScaler products.
A new Android malware named Manic targeting users in multiple European countries has a fallback data exfiltration mechanism that uses nearby infected devices.
CERT Polska has issued a warning as attackers begin actively exploiting a critical remote code execution vulnerability in the Zimbra Collaboration Suite.
Japanese cloud and data center provider Sakura Internet disclosed a cyberattack that compromised its sales management system containing customer contract and membership data.
A suspected ransomware affiliate is pretending to be a data recovery service called "Ransom Busters" to extract payments from victims.
A law enforcement officer in the US abused government automated license plate recognition cameras to stalk his former spouse hundreds of times.
A large-scale cyberattack campaign dubbed CameraSwarm has compromised more than 14,500 Dahua IP cameras, mostly located in Ukraine and Russia.
American authorities have charged 17 Iranian nationals linked to the Mabna Institute hacking-for-hire group over massive data theft operations.
Huntress observed a massive 155x increase in password spraying attacks driven by legacy auth and MFA vulnerabilities.
CISA has warned that hackers are actively exploiting a critical remote code execution flaw in the Windows Internet Key Exchange service.
The FBI and CISA report that the Medusa ransomware gang has breached more than 500 critical infrastructure organizations in the US since June 2021.
Comcast is promoting WiFi-based motion detection as part of its Xfinity Shield platform, allowing routers to detect people moving around the house without physical sensors.
Apple has detailed the security content of the new Safari 26.6.1 update, bringing crucial WebKit patches to macOS Sonoma and Sequoia users.
Cybercriminals have developed a custom Java web shell targeting PTC Windchill and FlexPLM servers to decrypt credentials and steal sensitive data.
The social networking site Bluesky was hit by another large-scale DDoS attack this year, causing temporary service disruptions.
Picus Security's Blue Report 2026 highlights how prevention rates vary by technique and why behavioral testing is essential to uncover hidden security gaps.
The U.S. CISA confirms that ransomware gangs are actively exploiting a high-severity Windows Task Host vulnerability.
Microsoft has officially begun removing the legacy WMIC command-line tool starting with Windows 11 version 24H2 and recent beta builds.
Cybersecurity experts who investigate spyware attacks say the number of people who received a recent threat notification from Apple is unusually high.
A threat actor is selling employee databases allegedly stolen from the Microsoft Azure infrastructure of multiple Fortune 500 companies.
Pokémon Center is notifying customers in the UK and Germany after a third-party data breach at logistics provider CEVA Logistics.
Apple has officially released iOS 26.6.1 for iPhone, bringing crucial patches for more than 20 security vulnerabilities.
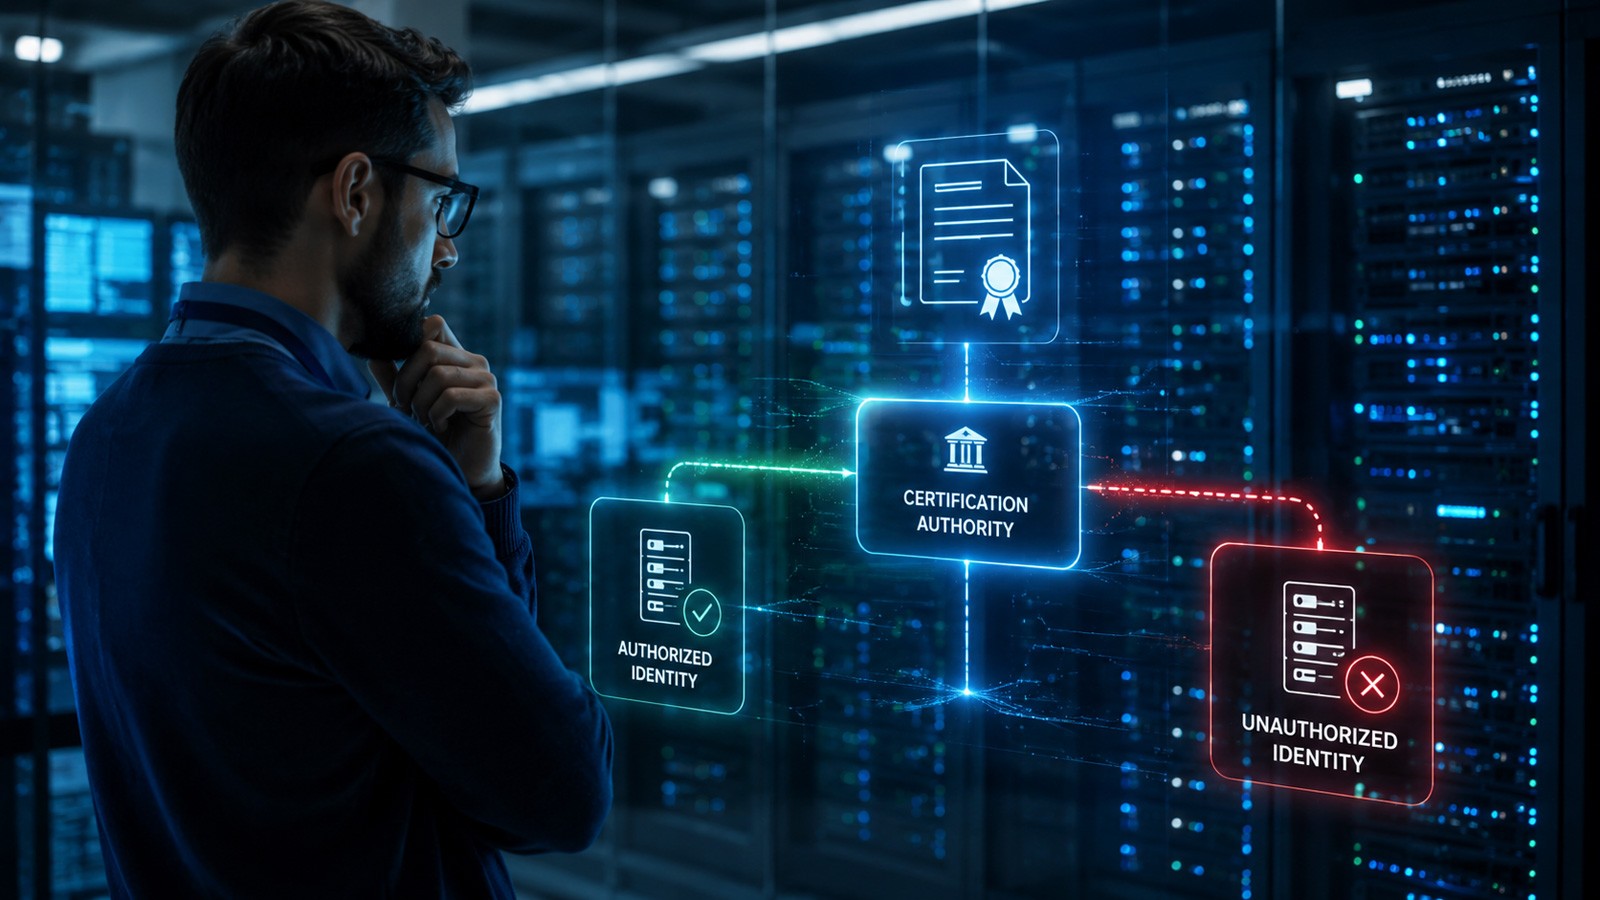
CVE-2026-54121 allows a standard domain user to escalate an Enterprise CA into a Domain Controller.
Apple recently patched a serious screen sharing flaw in macOS, and security experts warn that the vulnerability is now being actively exploited.
Tech giants General Electric (GE) and Philips have confirmed they are actively investigating claims made by the Clop ransomware gang regarding a data breach.
Microsoft is actively developing a security patch to address the ShieldBreak zero-day vulnerability tracked as CVE-2026-69414.
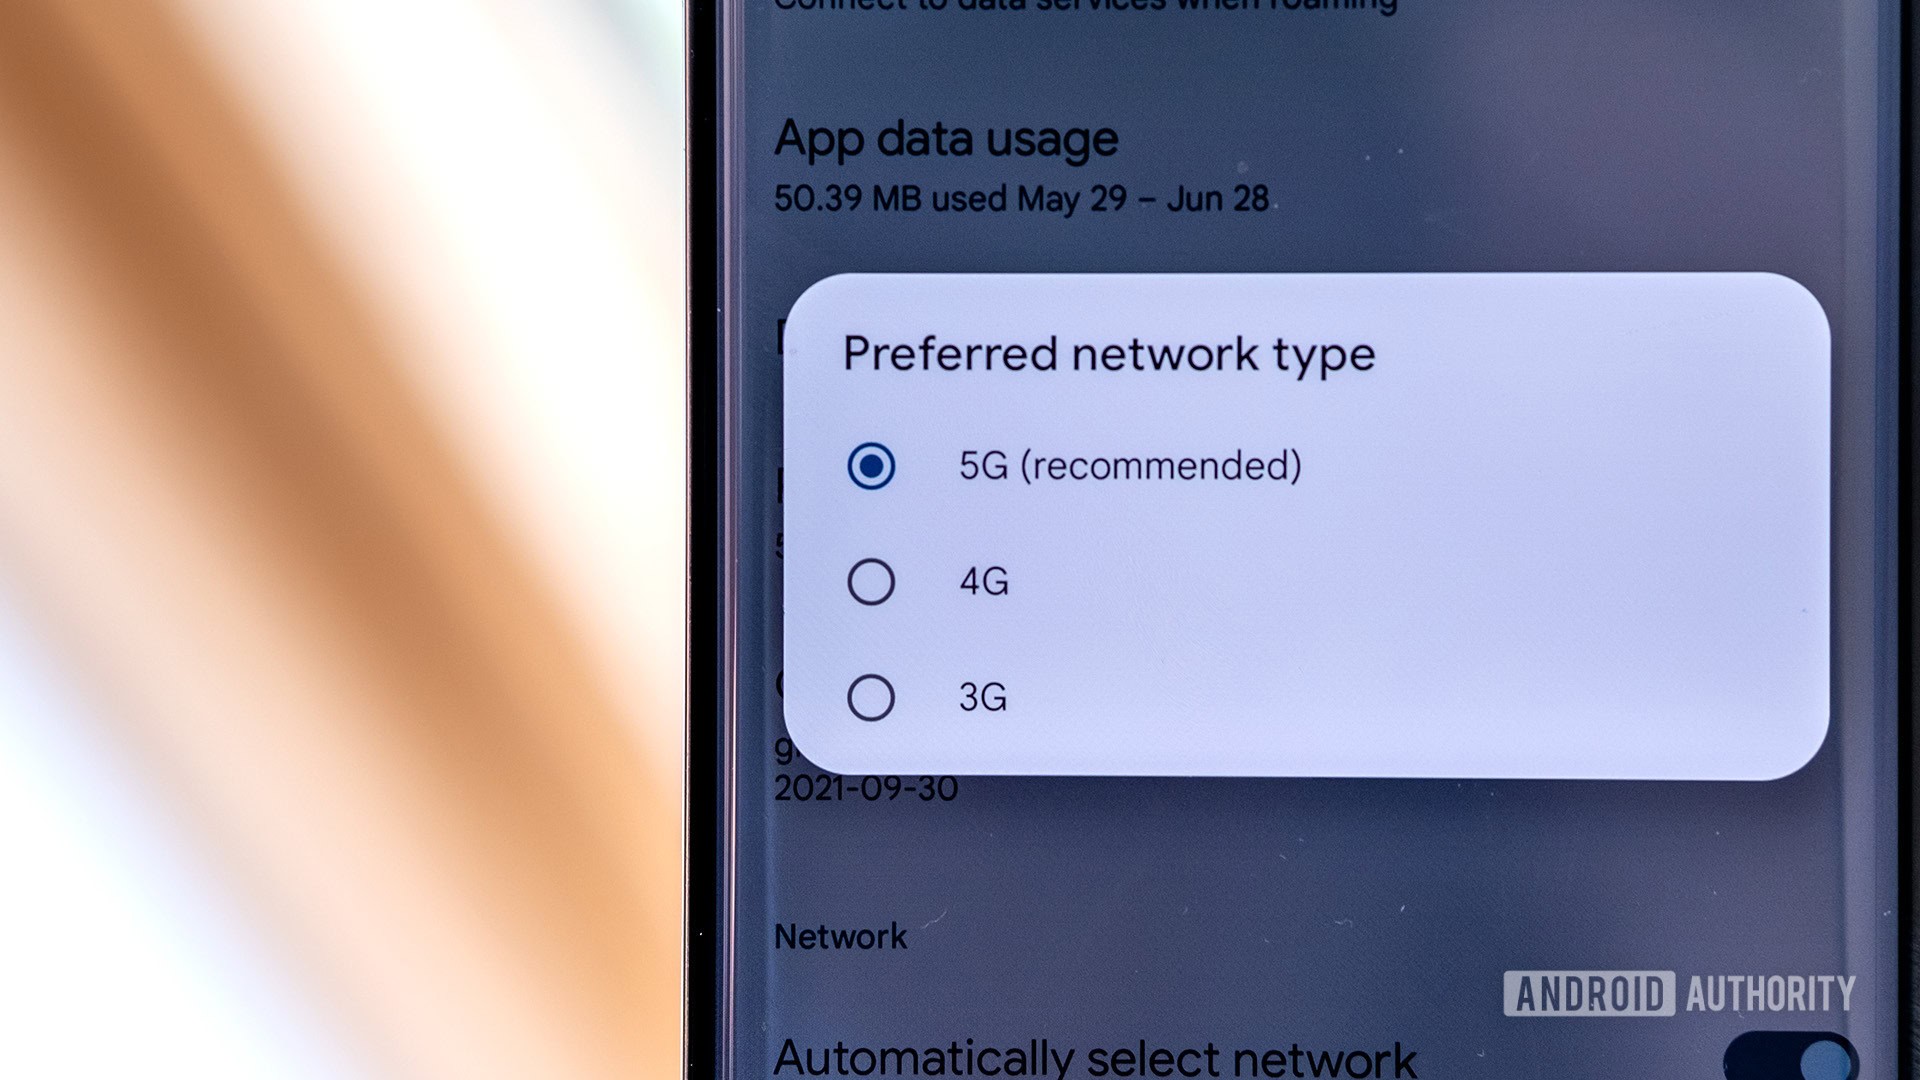
Google is adding a security log, cipher encryption details, and more notification alerts to protect against cellular attacks.

Popular crypto hardware wallet provider SafePal has confirmed a security breach affecting 39,798 customers after an order data flaw was exploited.

Threema secure messaging service faced multiple DDoS attacks earlier this week, causing communication disruptions.

A new information-stealing malware called AmnesiaStealer targets macOS users via ClickFix attacks, featuring remote browser control.

Social engineering attacks are becoming more sophisticated. Companies must combine staff training with technical controls.

The “never trust, always verify” principle is becoming the new standard for enterprise networks.

Preventing every attack is difficult, but good backups and a response plan can dramatically reduce damage.