Crypto's longtime foe: North Korea's Lazarus Group likely behind Binance hack, blockchain sleuths say
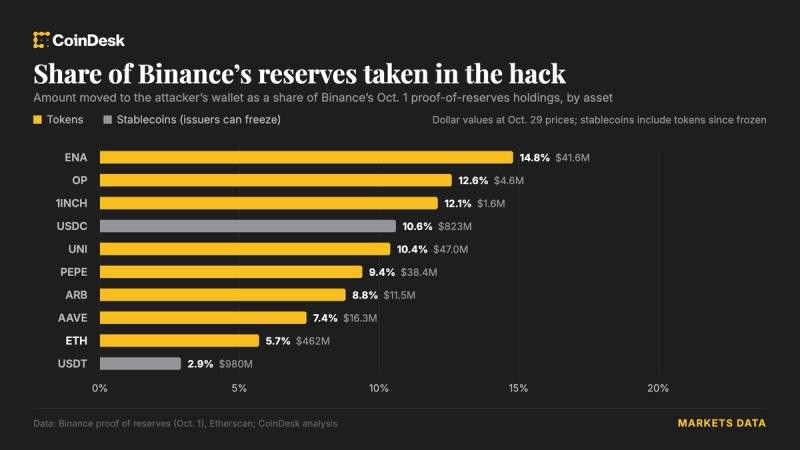
Blockchain investigators suggest that North Korea-linked Lazarus Group is likely behind the recent security breach and hack targeting Binance.
One of the most notorious and persistent threats in the cryptocurrency ecosystem, North Korea's Lazarus Group, has once again emerged as the prime suspect in a major cyber incident. Blockchain researchers and security sleuths have pointed to the group's involvement in recent malicious activities targeting the Binance platform.
Initial tracking of on-chain transactions and movement of funds reveals operational patterns and laundering techniques closely matching previous campaigns attributed to Lazarus. The hacker collective has a long history of systematically targeting major digital asset exchanges worldwide.
Security teams at Binance, alongside independent cybersecurity analysts, are actively investigating the breach to determine the full scope of the incident. While technical details and exact figures are being assessed, experts emphasize the growing need for enhanced defensive measures across all centralized platforms.
This developing situation serves as a stark reminder to the global crypto community about the persistent nature of state-sponsored cyber threats. Ensuring robust security protocols remains a top priority for protecting user funds and maintaining trust in the digital asset industry.