Certighost and the Privilege Hiding in Your Certificate Authority
CVE-2026-54121 allows a standard domain user to escalate an Enterprise CA into a Domain Controller.
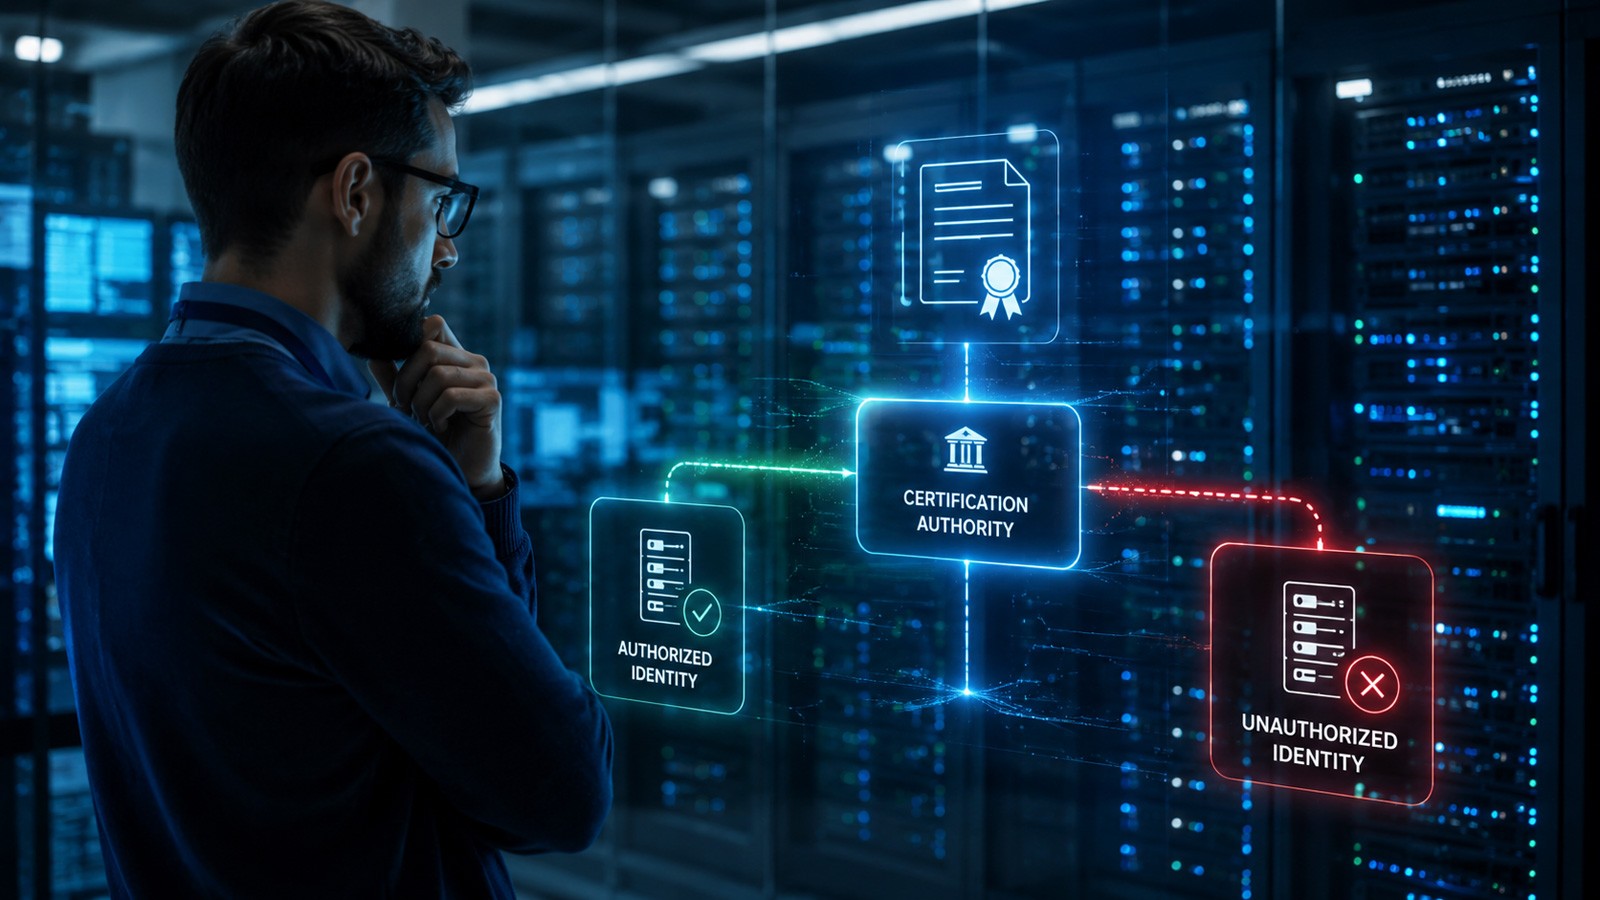
According to BleepingComputer, a newly highlighted security concern exposes deep architectural risks within enterprise environments. Tracked as CVE-2026-54121 and dubbed Certighost, the vulnerability demonstrates how a standard, low-privileged domain user can leverage an Enterprise Certificate Authority to effectively become a Domain Controller.
The core issue revolves around implicit trust and standing privileges embedded within Public Key Infrastructure (PKI) deployments. Attackers can exploit these hidden vectors to bypass standard controls, turning auxiliary certificate services into powerful levers for full network compromise.
Security experts emphasize that while applying the vendor patch is necessary, it is merely the easiest part of the remediation process. The real challenge lies in addressing long-standing assumptions about implicit trust and treating PKI with the strict governance reserved for Tier 0 identity infrastructure.
Historically, certificate authorities have often been overlooked or treated as secondary administrative components rather than core security bastions. However, vulnerabilities like Certighost prove that PKI components hold the keys to the entire directory services kingdom and must be defended accordingly.
For organizations managing complex IT landscapes, this incident serves as a vital reminder to continuously audit standing privileges and re-evaluate their identity infrastructure security postures to prevent advanced escalation paths.