Russian Police Arrest 3 VasyGrek Hackers and Dismantle Infrastructure
Russian authorities have arrested three suspected members of the VasyGrek threat group and dismantled their criminal cyber infrastructure.
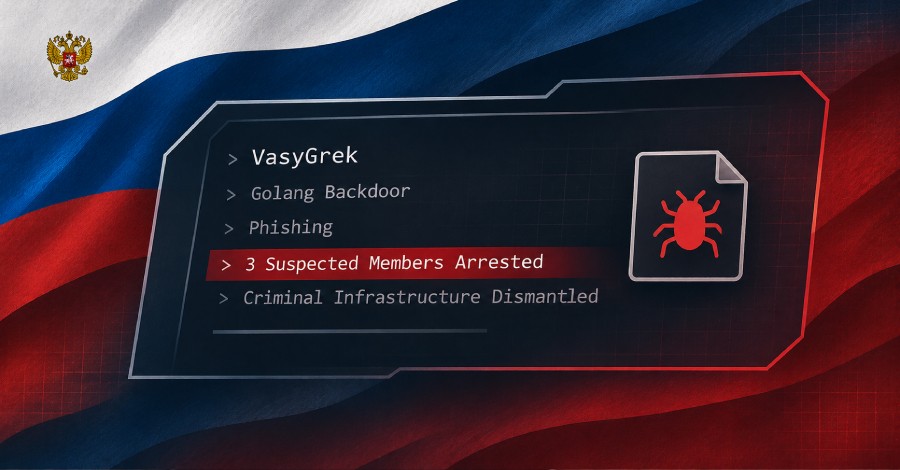
Russian law enforcement authorities have successfully detained three suspected members of the VasyGrek threat group, dismantling their criminal infrastructure in the process. The operation marks a significant step in countering corporate cybercrime in the region.
- Three suspected members of the VasyGrek threat group were arrested
- The group, also known as Fluffy Wolf, has targeted companies since 2016
- Targets included both Russian and international corporate entities
- The Russian Ministry of Internal Affairs reported funds embezzlement from organizations
Background of the VasyGrek Threat Group
Also operating under the alias Fluffy Wolf, the threat actor has a long history of targeting various organizations. Security records show that the group has been active since 2016, consistently focusing on Russian and international companies.
Over the years, the group developed sophisticated methods and infrastructure to compromise corporate networks and execute unauthorized financial transactions, causing substantial issues for targeted businesses.
Read alsoCertified Android TV manufacturer Videostrong embedded backdoor in 1.3 million devicesLaw Enforcement Action and Details
According to the Ministry of Internal Affairs of the Russian Federation (MVD), the arrested individuals are suspected of embezzling funds from corporate accounts. Police action successfully disrupted the operational capabilities of the gang.
The takedown of this criminal infrastructure highlights ongoing international and domestic efforts to curb sophisticated cyber threat actors targeting financial assets.
Impact on Cybersecurity Landscape
The dismantling of the VasyGrek infrastructure provides temporary relief for businesses facing targeted financial attacks. Experts emphasize that companies must remain vigilant and continuously update their security protocols against similar threat actors.
Source: The Hacker News