Yoba Campaign Spreads Crypto Miners via Fake ChatGPT and Claude Apps
Threat actors are distributing malware and crypto miners disguised as desktop apps for Anthropic Claude and OpenAI ChatGPT on GitHub.
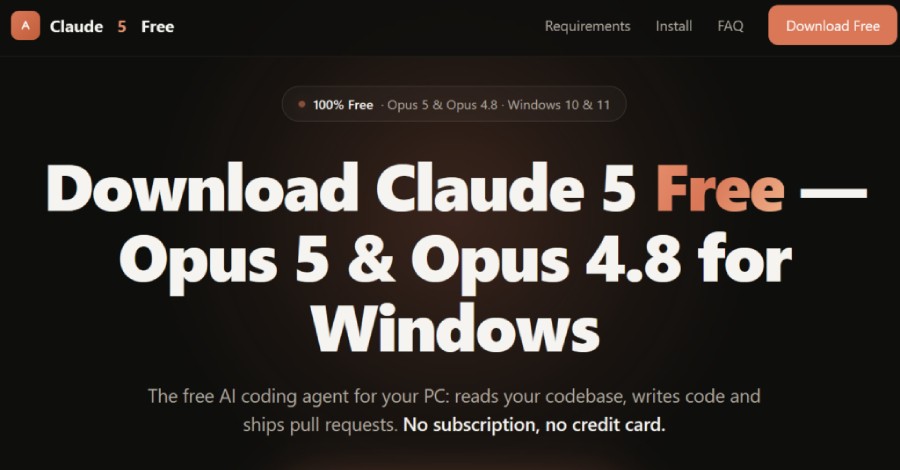
Cybercriminals are targeting users with a new campaign dubbed Yoba, which delivers malicious loaders and cryptocurrency miners disguised as popular artificial intelligence applications. The threat involves fake desktop tools for OpenAI ChatGPT and Anthropic Claude.
Key facts about the Yoba campaign: - Fake GitHub projects mimic desktop applications such as GPT-5.6 Sol, GPT-6 Astra, and Claude Opus. - Attackers leverage signed executable files to bypass standard security controls. - The ultimate goal is to deploy the Manba malware family for cryptocurrency mining.
Details of the Yoba Threat Campaign The malicious activity relies on deceiving users who are searching for desktop clients of leading AI services. By creating convincing yet fraudulent repositories on GitHub, threat actors trick individuals into downloading what they believe are official or advanced versions like GPT-5.6 Sol, GPT-6 Astra, and Claude Opus.
The use of signed executables is a critical technique in this campaign, as it helps the malicious loaders evade detection by security software and operating system warnings. This increases the success rate of infecting target machines with unwanted payloads.
Impact and Security Recommendations The primary consequence for victims is the silent deployment of the Manba malware, which utilizes device resources to mine cryptocurrency without the user's consent. This leads to performance degradation and hardware strain. To stay safe, users must download AI applications exclusively from official vendor websites and exercise extreme caution when dealing with third-party GitHub repositories promising unreleased or unofficial desktop clients.
Source: The Hacker News