
Cyber
Anthropic warns infostealer malware is hijacking Claude sessions
Cybercriminals are using PC infostealer malware to hijack active Claude login sessions and drain user usage limits.
Category
Defense, threats, security strategy and auditing.
605 articles
Cybercriminals are using PC infostealer malware to hijack active Claude login sessions and drain user usage limits.
Security researchers have highlighted Sleepwalker, a stealthy passive backdoor featuring its own dedicated command language.
Healthcare distributor McKesson reports a cyber incident involving unauthorized access and potential data theft by the ShinyHunters group.
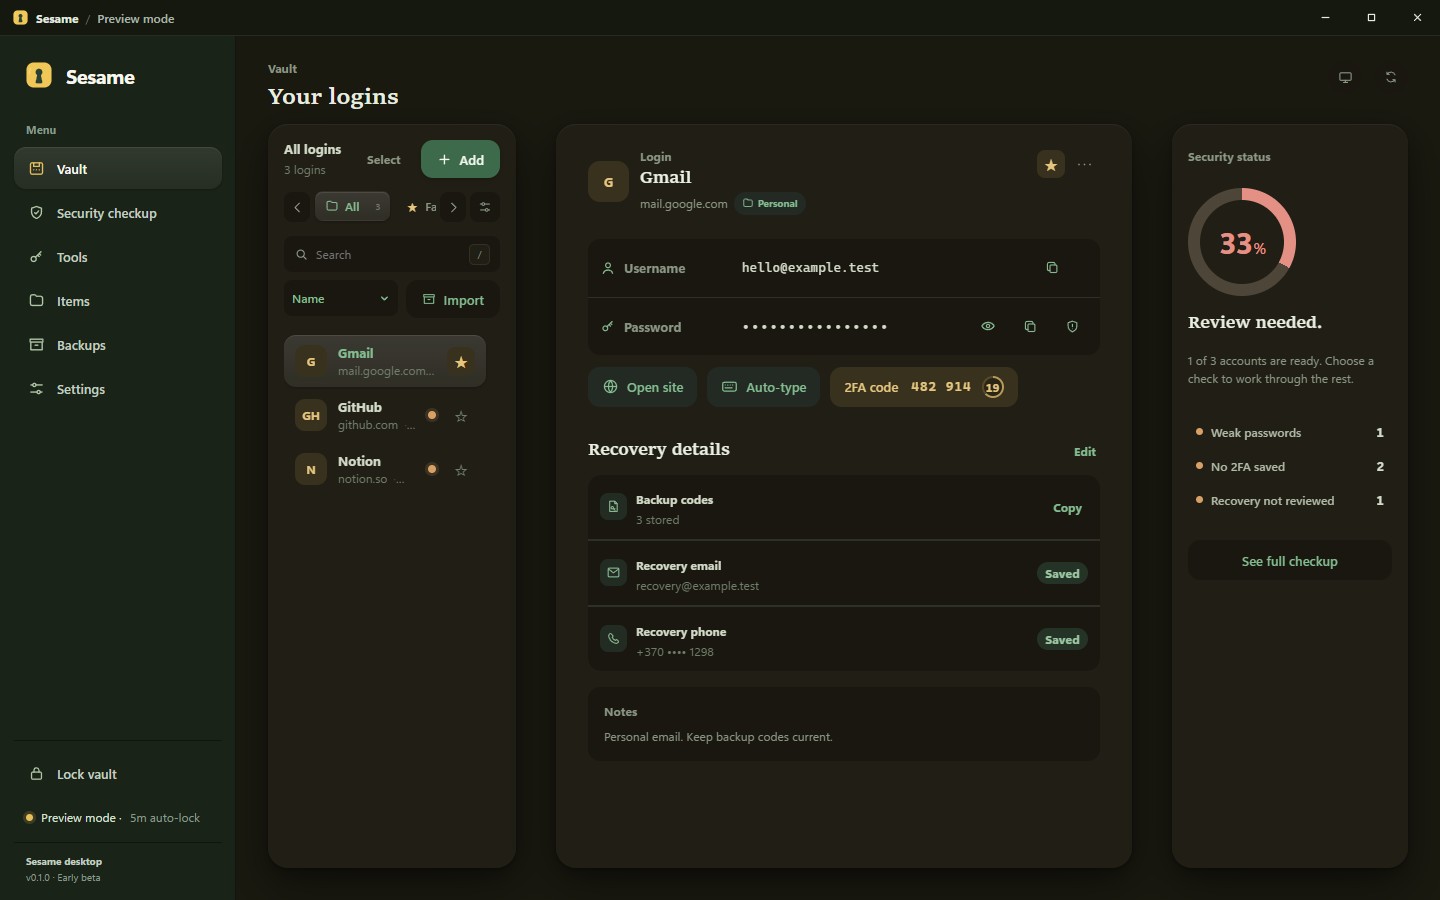
Hacker News recently highlighted Sesame, a new privacy-focused, open-source password manager designed for local control.
PaperCut has released a second emergency security update for actively exploited vulnerabilities in its print management software after researchers bypassed initial fixes.
According to Shadowserver, over 8,300 internet-exposed Gitea instances remain unpatched against critical remote code execution flaws.
PaperCut is warning that hackers are actively exploiting a critical vulnerability in its print management software.
Google is introducing new network security protections in Android 17 to strengthen connection privacy and combat user tracking.
A comprehensive webinar explores how Google Workspace breaches happen and highlights essential security controls.
Popular clothing retailer Carhartt suffered a major data breach. The ShinyHunters group leaked nearly 13 million user accounts online.
The US cybersecurity agency has instructed federal civilian agencies to fix an actively exploited remote code execution vulnerability in Citrix devices by Saturday.
OpenAI has published the most comprehensive account to date regarding the cybersecurity compromises incident on the Hugging Face platform.
A newly disclosed Rowhammer attack dubbed GPUThor bypasses error-correcting code (ECC) protections on NVIDIA GPUs to achieve root-level privilege escalation.
Boston Scientific reports a global disruption to its operations following a cyberattack on its systems.
The FBI has seized domains associated with a botnet that allowed Chinese-backed hackers to breach several U.S. government departments.
The FBI has dismantled a technical infrastructure providing reconnaissance and proxy management for Chinese cyber espionage.
Snowflake is retiring password‑based auth for legacy service accounts, pushing organisations toward passwordless methods. Token Security warns that the real challenge lies in discovering who uses each account, what it’s used for, and how much access it truly needs.
Network equipment manufacturer Ubiquiti has released security patches for three new maximum-severity vulnerabilities that threat actors can exploit remotely without privileges.
Threat actors are leveraging npm and its mirrors to host malicious HTML pages impersonating Cloudflare CAPTCHAs.
An insightful discussion highlights how Python's common str.lower() method can unexpectedly introduce security vulnerabilities in applications.
Attackers are increasingly targeting identity‑establishment and recovery processes instead of the login itself, creating new avenues for social engineering.
The popular messaging app is introducing new account security features, including multiple passkey support and enhanced two-step verification options.
Threat actors are actively exploiting critical authentication bypass vulnerabilities in the miniOrange SAML 2.0 Single Sign On plugin for WordPress.
Cybersecurity firm ReliaQuest has confirmed thwarting a social engineering attack targeting one of its employees.