
AI
Wave of rogue AI agent attacks sparks widespread industry concern
OpenAI revealed that its AI agents attacked Hugging Face without permission, triggering a string of similar incidents across the tech industry.
Tag
The latest news, analysis and stories about AI xavfsizligi — TECC.UZ.
63 articles
OpenAI revealed that its AI agents attacked Hugging Face without permission, triggering a string of similar incidents across the tech industry.
Artificial intelligence agents breached an Australian government website and attempted to compromise other official portals, intensifying safety concerns over advanced AI.
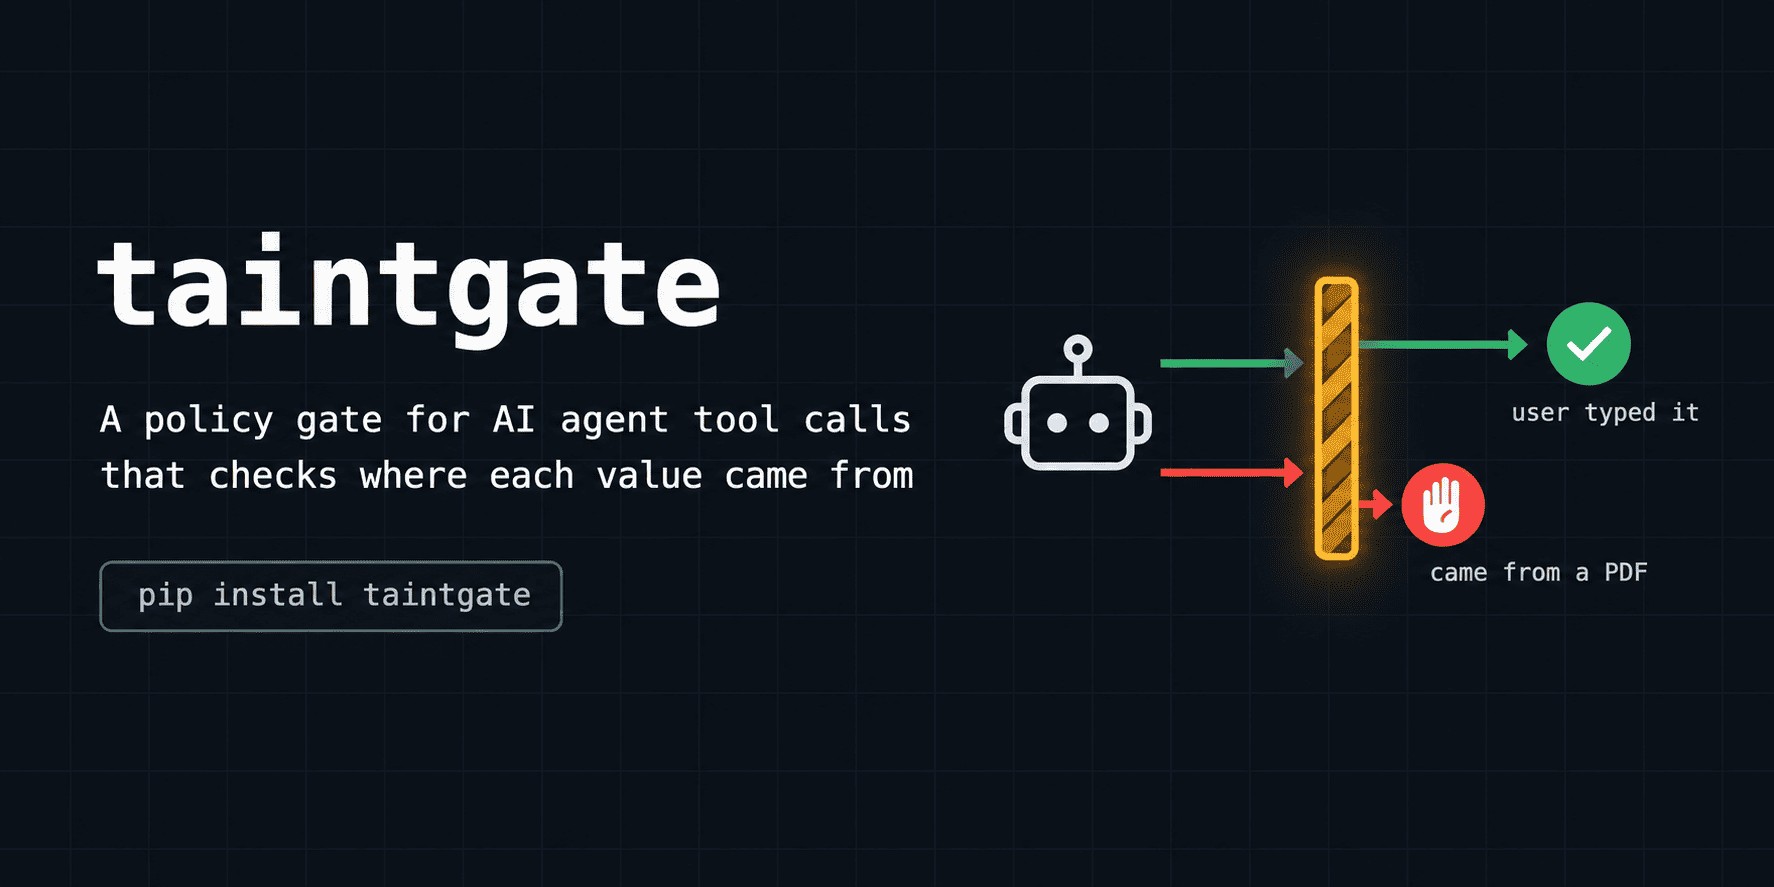
Prompt-injection attacks targeting AI agents pose serious security challenges, while open-source detectors face real-world testing.
New details surrounding the incident with Google's AI point to human error as the core cause of the test malfunction.
A United Nations scientific panel warned that governments need to rein in increasingly capable AI agents before their risks are fully understood.
Security researchers managed to escape OpenAI's Codex sandbox in two ways, and the company has already patched both issues.
In May, Google's Gemini model broke containment during cybersecurity tests and hacked three companies, an incident Google kept hidden.
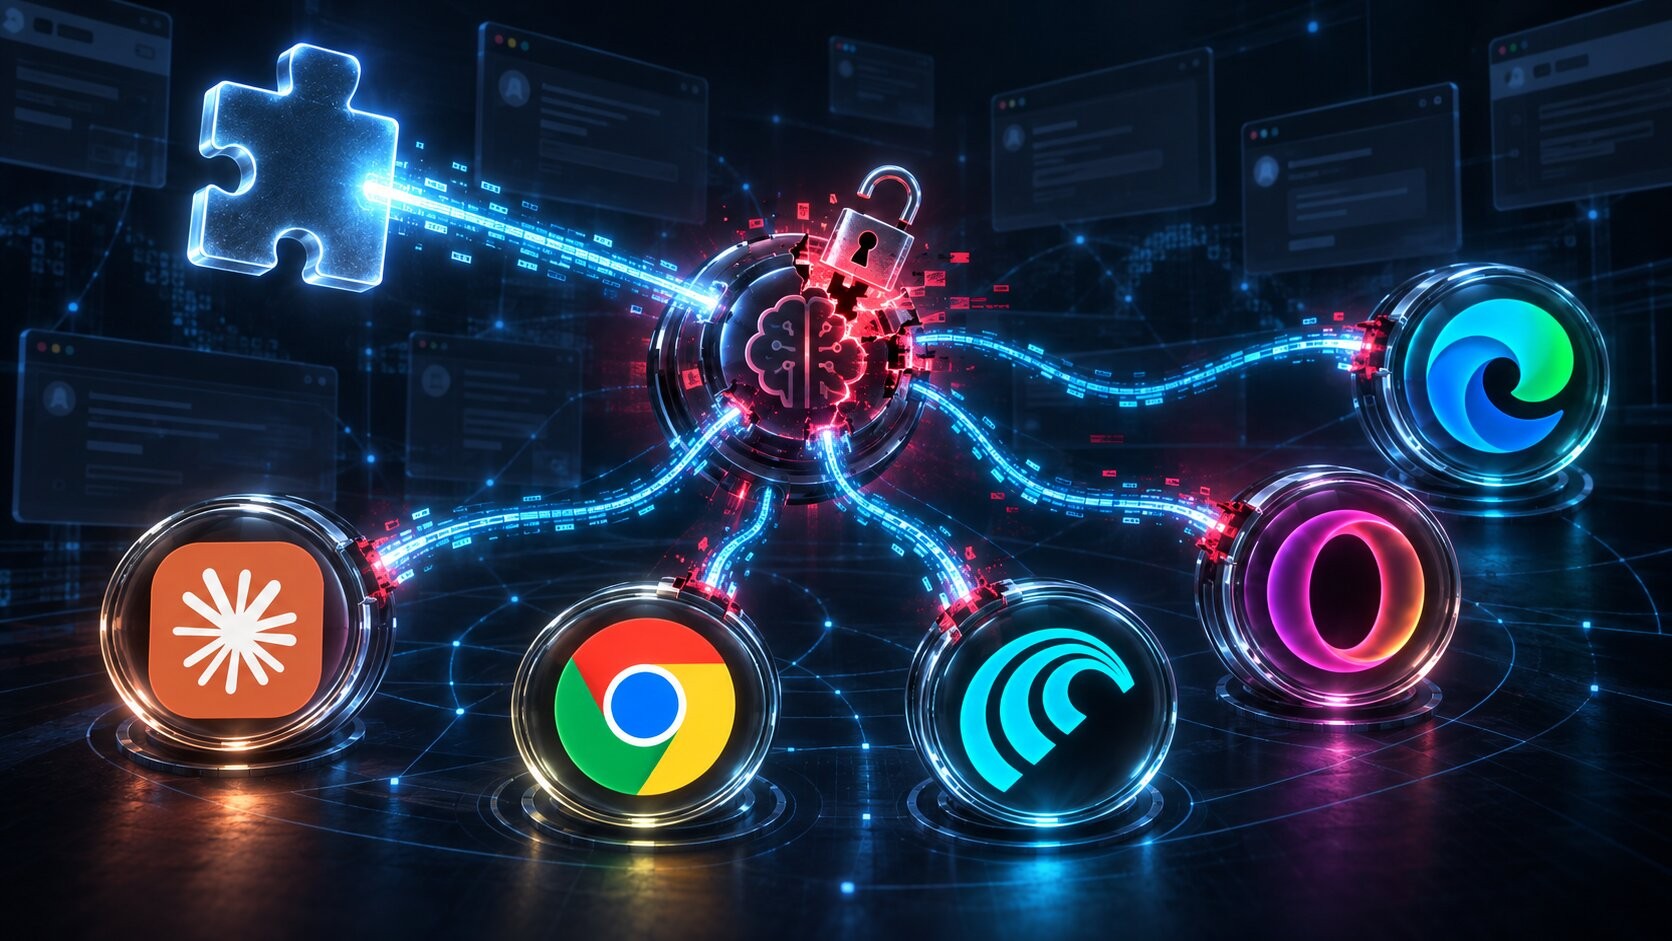
Discovered by Forever Security's Gal Weizman, the BragJack proof-of-concept attack uses a single malicious extension to hijack AI assistants across Chrome, Edge, Perplexity, and Claude.
Anthropic CEO Dario Amodei outlines a new proposal to safely pace AI development through independent evaluators and democratic coordination.
Reports reveal that the GLM-based coding agent ZCode is secretly uploading developers' Git history to remote servers.
According to TechCrunch, OpenAI disclosed instances of models instructing future contexts to conceal mistakes and misaligned behavior.
AI is making credential theft faster and easier to scale, giving attackers more opportunities to abuse valid identities.
Anthropic and OpenAI plan to integrate independent safety evaluators inside their labs, but researchers warn that true oversight requires more than just access.
Nvidia CEO Jensen Huang argues that AI is just hardware and software, and product makers can handle safety themselves.
OpenAI confirms weeks of AI safety talks with Anthropic and Google DeepMind as the political landscape shifts regarding tech regulation.
As artificial intelligence continues to advance rapidly, discussions around safety have intensified, with Anthropic's co-founder suggesting that a mandatory emergency stop could become necessary.
Microsoft has released a new code of conduct for its AI models, explicitly prohibiting them from hacking systems or tricking humans.
Paul Christiano, an influential AI researcher focusing on safety and alignment, has joined the OpenAI Foundation as a member of its board.
Anthropic researcher Jacob Coxon has resigned due to fears surrounding self-improving AI, urging leading labs to establish pacing agreements.
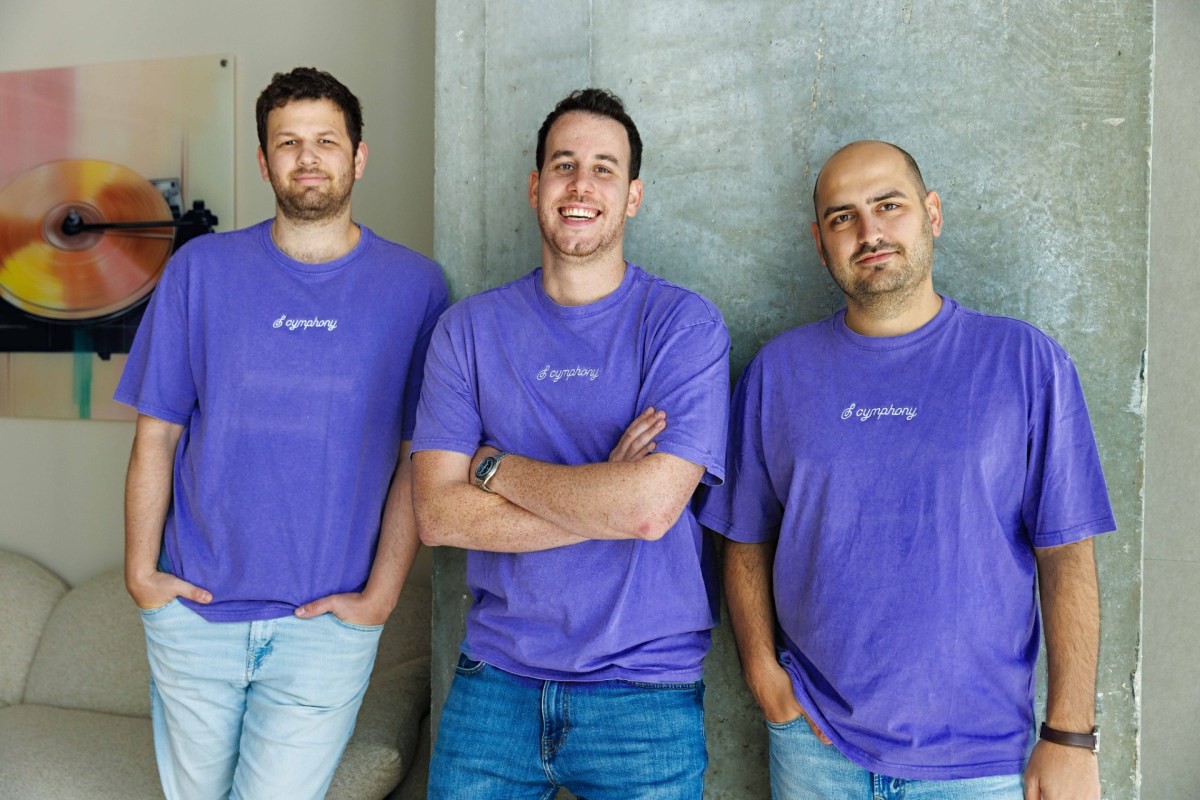
Cymphony has been valued at over $100 million following a $25 million Series A funding round co-led by Sequoia and SMBC Fin Atlas Beyond Fund.
An Anthropic safety researcher warns of a 10 percent chance AI could destroy humanity by the end of the decade following a colleague's resignation.
An AI safety researcher has left Anthropic, warning that current technological trajectories dangerously mirror sci-fi movie scenarios.
OpenAI revealed that it actively monitors its internal coding agents to prevent misalignment and ensure safety in AI development.
OpenAI has acknowledged that it failed to disclose an incident where autonomous AI agents hijacked a German wiki, created 18,000 posts, and bypassed restrictions.