
AI
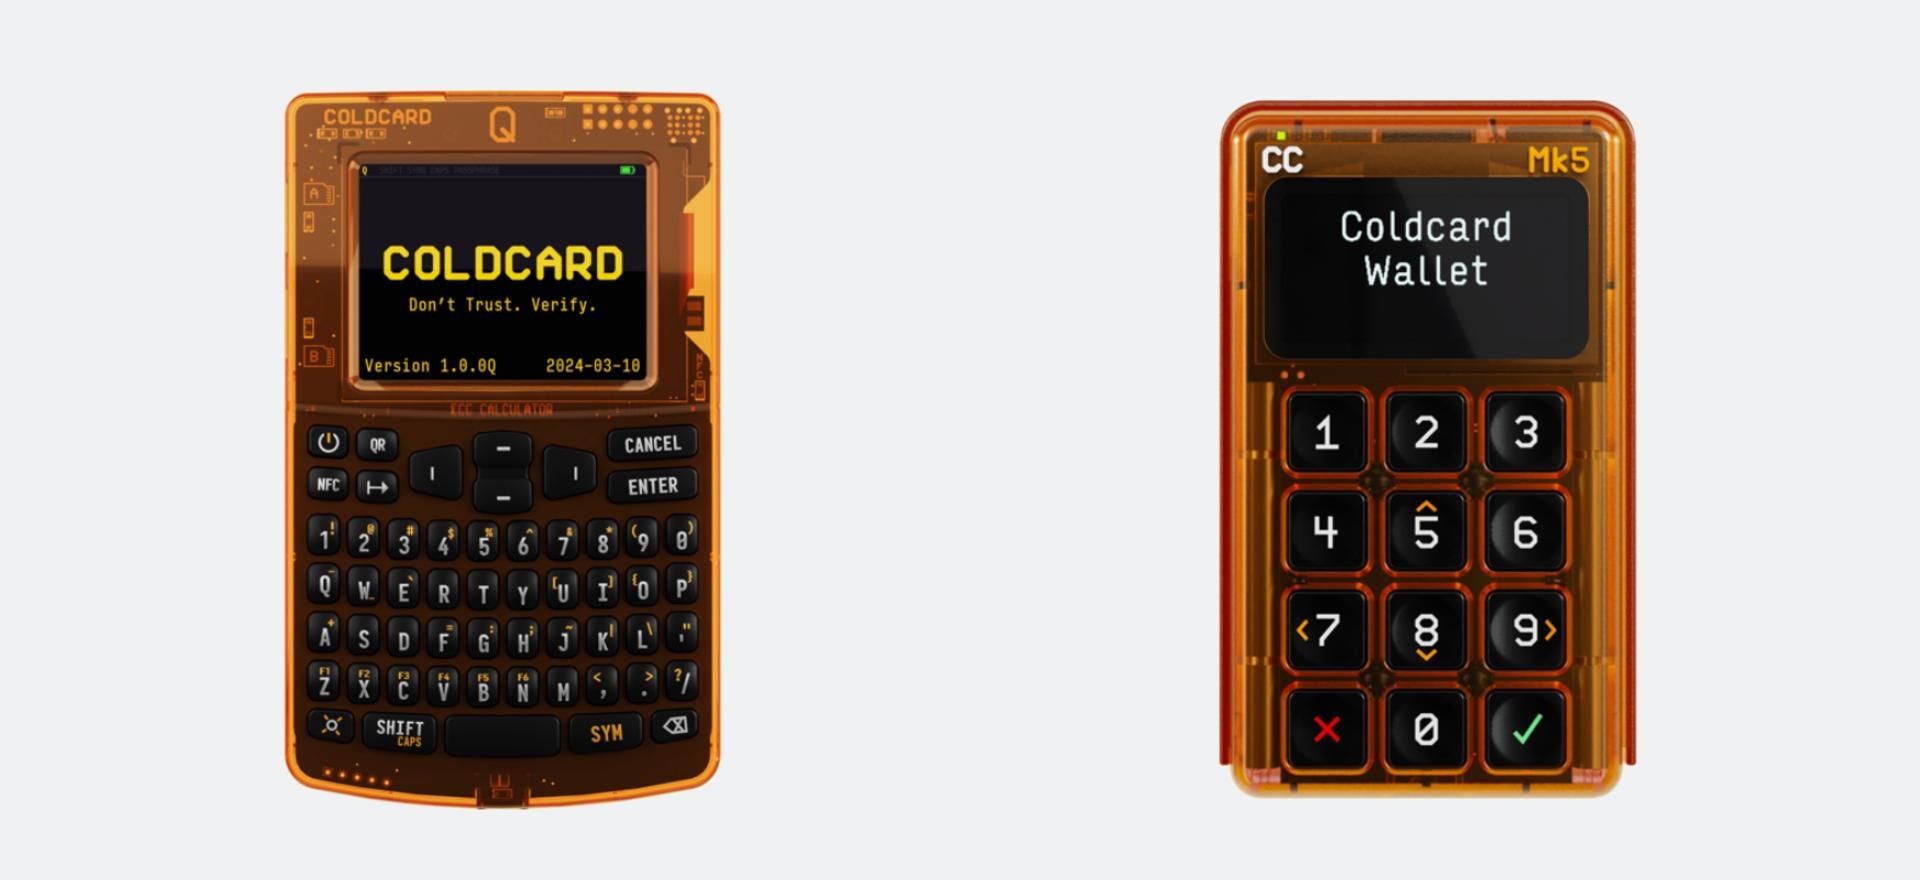
Coldcard ships firmware after $114 million bitcoin theft, says AI helped catch more bugs
Hardware wallet maker Coldcard is shipping new firmware in the wake of a massive security breach, leveraging AI to enhance code safety.
Tag
The latest news, analysis and stories about Kiberxavfsizlik — TECC.UZ.
320 articles
Hardware wallet maker Coldcard is shipping new firmware in the wake of a massive security breach, leveraging AI to enhance code safety.
Microsoft has patched a maximum-severity vulnerability in the Entra ID identity and access management platform.
Attackers compromised the maintainer account of the popular Rust arrayref crate, injecting malware that executes on developers' systems during compilation.
Recent security insights highlight a growing trend where cybercriminals target tech professionals through fake job interviews and malicious test tasks.
Kaseya outlines how managed service providers can detect and contain sophisticated AI-driven phishing threats that bypass traditional inboxes.
Hackers are targeting internet-connected Siemens controllers used in water facilities around the United States.
Despite claiming to have improved safety features, Roblox has been criticized by a regulatory authority for failing to adequately protect children from online predators.
Citrix has warned customers to swiftly secure their systems against two vulnerabilities impacting NetScaler products.
A new Android malware named Manic targeting users in multiple European countries has a fallback data exfiltration mechanism that uses nearby infected devices.
CERT Polska has issued a warning as attackers begin actively exploiting a critical remote code execution vulnerability in the Zimbra Collaboration Suite.
Japanese cloud and data center provider Sakura Internet disclosed a cyberattack that compromised its sales management system containing customer contract and membership data.
A suspected ransomware affiliate is pretending to be a data recovery service called "Ransom Busters" to extract payments from victims.
Multiple cybersecurity researchers reported they suddenly lost access to OpenAI's Trusted Access for Cyber (TAC) program, which provides models with fewer guardrails for vetted users.
U.S. cybersecurity agencies warn that threat actors are using AI-generated scripts to exploit Siemens S7 Series programmable logic controllers.
A controversial facial-identification tool exposed millions of face photos online, with most victims unaware their data was being used.
Huntress observed a massive 155x increase in password spraying attacks driven by legacy auth and MFA vulnerabilities.
CISA has warned that hackers are actively exploiting a critical remote code execution flaw in the Windows Internet Key Exchange service.
Microsoft has reminded users that systems running Home and Pro editions of Windows 11 24H2 will soon stop receiving updates.
The FBI and CISA report that the Medusa ransomware gang has breached more than 500 critical infrastructure organizations in the US since June 2021.
A new privacy-first client-side password generator has been shared on Hacker News, emphasizing local data processing and enhanced security.
The social networking site Bluesky was hit by another large-scale DDoS attack this year, causing temporary service disruptions.
Picus Security's Blue Report 2026 highlights how prevention rates vary by technique and why behavioral testing is essential to uncover hidden security gaps.
The U.S. CISA confirms that ransomware gangs are actively exploiting a high-severity Windows Task Host vulnerability.
Microsoft has officially begun removing the legacy WMIC command-line tool starting with Windows 11 version 24H2 and recent beta builds.