CISA Confirms Hackers Exploiting WordPress Core Flaw During Updates
CISA has added the WordPress Core vulnerability CVE-2026-119977 to the KEV catalog following active exploitation during software upgrades.
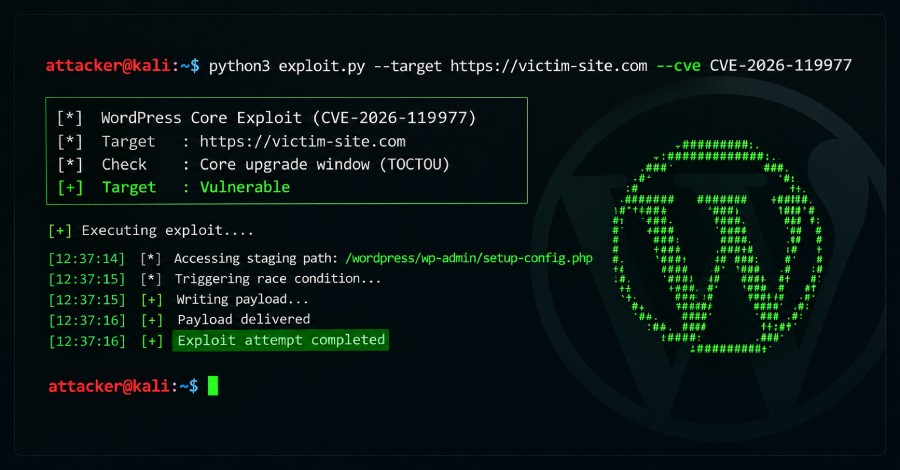
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has officially added a high-severity security flaw in WordPress Core to its Known Exploited Vulnerabilities (KEV) catalog. The move comes in response to concrete evidence that malicious actors are actively leveraging this flaw in real-world attacks.
- The vulnerability is tracked as CVE-2026-119977 with a CVSS severity score of 8.1.
- The security issue is classified as a Time-of-check Time-of-use (TOCTOU) race condition.
- Active exploitation has been specifically observed during software upgrade procedures.
Details of CVE-2026-119977 Vulnerability The discovered security flaw involves a TOCTOU race condition, a type of software bug that occurs when there is a timing discrepancy between checking a system resource's state and using that resource. Attackers can manipulate this gap to bypass security checks.
Successfully exploiting this high-severity flaw can allow unauthorized actors to execute arbitrary code on the affected server. This level of compromise grants malicious entities extensive control over vulnerable websites, risking data integrity and site availability.
Mitigation and Security Recommendations The inclusion of this flaw in the KEV catalog emphasizes the urgent need for remediation. While federal agencies must comply with strict patching deadlines, all administrators managing WordPress instances should take immediate defensive action.
Site owners and developers are strongly advised to apply official core updates as soon as they become available and monitor their web server environments closely to prevent potential exploitation during maintenance windows.
Source: The Hacker News