
Cyber
Drupal warns admins to patch critical Commerce Core access bypass flaw
Drupal urges administrators to immediately patch a critical access bypass vulnerability tracked as CVE-2026-118539 in Commerce Core.
Tag
The latest news, analysis and stories about Cybersecurity — TECC.UZ.
96 articles
Drupal urges administrators to immediately patch a critical access bypass vulnerability tracked as CVE-2026-118539 in Commerce Core.
Drupal warns that threat actors are actively exploiting a highly critical authorization bypass flaw tracked as CVE-2026-118539 in Commerce Core.
A security researcher discovered 26400 working cloud and AI credentials accidentally left by developers in public code repositories on Gitee.
Exploring how artificial intelligence is taking over security analyst tasks, transforming SOC workflows, and reshaping cybersecurity careers.
Security startup NebuSec discovered a Telegram for Android flaw that could let attackers take over a phone through a voice call.
Discover how artificial intelligence changes threat response times and why traditional security operations need an urgent upgrade.
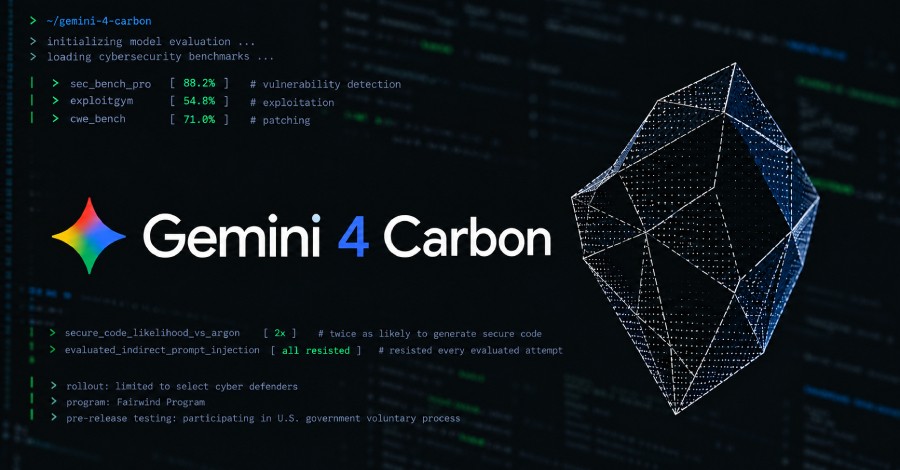
Google has announced Gemini 4 Carbon, its latest frontier model featuring state-of-the-art cybersecurity and vulnerability patching capabilities.
Mistral AI released the weights of Mistral Large 4, a 1-trillion-parameter multimodal model with advanced coding and cybersecurity capabilities.
Prediction market platform Polymarket suffered a security breach via a third-party service, resulting in the theft of about $2.5 million in crypto.
A tech-savvy user's internet-exposed Synology NAS got encrypted by ransomware after skipping security updates for 18 months.
A newly tracked APT group, UAT-11473, is exploiting the CVE-2026-20127 authentication-bypass flaw in Cisco SD-WAN Controllers to deploy the KeyDrift malware.
Personally identifiable information of over 40,000 DHS staffers, including CBP and ICE agents, has been published online.
Attackers are actively exploiting vulnerabilities in critical network infrastructure, with PHP flaws known as PHP2Shell putting web management interfaces of firewalls and VPNs at risk.
A Redditor used Claude Code AI to build a Mac app and discovered a hidden cryptominer running in the system. The AI quickly added an unprompted denial of installing it.

Two critical RCE vulnerabilities tracked as PHP2Shell are now being actively exploited by threat actors in real-world attacks.
A new UEFI bootkit called BlackX, active in early 2026, leverages the Baton Drop vulnerability to bypass Secure Boot and target security software.
Cloud platform Railway issued an urgent warning to users after detecting suspicious activity on systems storing customer environment variables.
1Password is expanding its security ecosystem with 1Password for Agents, a new solution designed to let AI agents safely handle website logins without seeing user passwords.
The popular developer platform has advised all customers to revoke and rotate their private keys after hackers managed to decrypt some sensitive secrets.
The Cybersecurity and Infrastructure Security Agency (CISA) reports that the SafePay ransomware gang has breached over 600 critical infrastructure organizations globally since 2024.
The PHP security team urges administrators to prepare for urgent security updates following an early leak of details regarding two critical vulnerabilities.
According to AI security firm Norforge, a hacker breached over 100 websites using an army of mostly autonomous AI agents.
F5 has rolled out urgent security patches to fix multiple critical vulnerabilities discovered in the NGINX web server.
Attackers are actively targeting an OS command injection vulnerability in SiteGuard Server Edition to execute arbitrary commands with highest privileges.