Google Warns LLMjacking Attacks Costing Enterprises Up to $1M
Google warns that LLMjacking attacks are hijacking enterprise AI access, running up to $1 million in unauthorized cloud and computing charges.
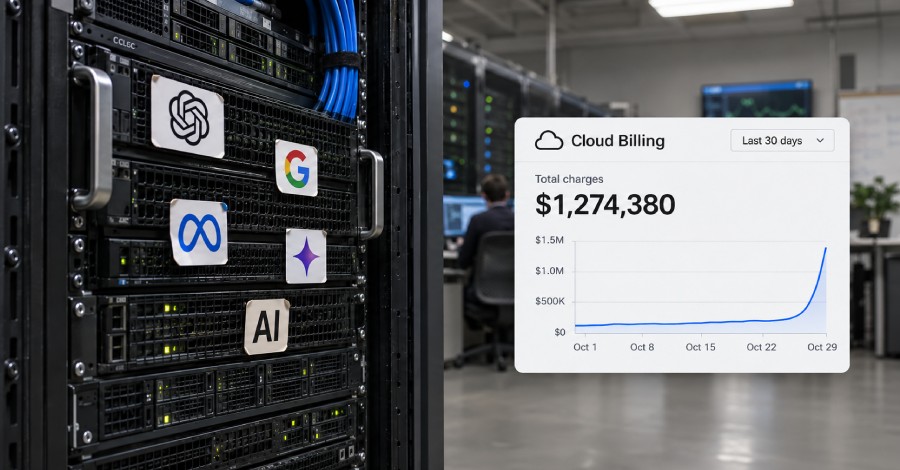
Google has issued a serious warning regarding a rising cyber threat trend where malicious actors hijack enterprise access to Large Language Models (LLMs) to exploit expensive computing infrastructure.
This emerging tactic, dubbed LLMjacking, represents a resource-hijacking method specifically adapted for the generative AI era.
- Threat actors hijack enterprise LLM access to leverage expensive computing resources fraudulently.
- Losses for certain targeted enterprises have reached up to $1 million in cloud bills.
- Attack vectors include phishing, source code leaks, and misconfigured cloud environments.
Understanding LLMjacking Mechanics
The core of the attack relies on obtaining valid API keys that enterprises use to integrate powerful language models into their applications. Once cybercriminals acquire these credentials, they execute resource-intensive AI queries at the victim's expense.
Read alsoGoogle Gemini in Gmail: How AI Reads Your Emails and How to Turn It OffAttackers leverage these stolen resources for heavy data processing, content generation, or resale on underground markets, leaving victim organizations with massive unexpected cloud service invoices at the end of the billing cycle.
Common Vectors of Compromise
According to threat intelligence reports, attackers typically gain unauthorized entry through human error and security oversights. API keys are frequently discovered in public source code repositories where developers accidentally expose secrets.
Additionally, threat agents employ targeted phishing campaigns against administrative accounts and exploit vulnerabilities within client-side application code or poorly configured cloud environments lacking proper access controls.
Business and Security Implications
For enterprises worldwide, this growing menace highlights the critical need to enforce strict security protocols surrounding AI infrastructure. Traditional network perimeters are no longer sufficient to prevent financial drain in cloud environments.
Organizations must implement robust secrets management, continuous code auditing, and anomaly detection systems to monitor token consumption and protect expensive AI deployments from fraudulent abuse.
Source: The Hacker News