
CISA warns of critical pre-auth RCE flaw in MikroTik RouterOS
The U.S. Cybersecurity and Infrastructure Security Agency has issued a warning regarding a critical remote code execution vulnerability in MikroTik RouterOS.
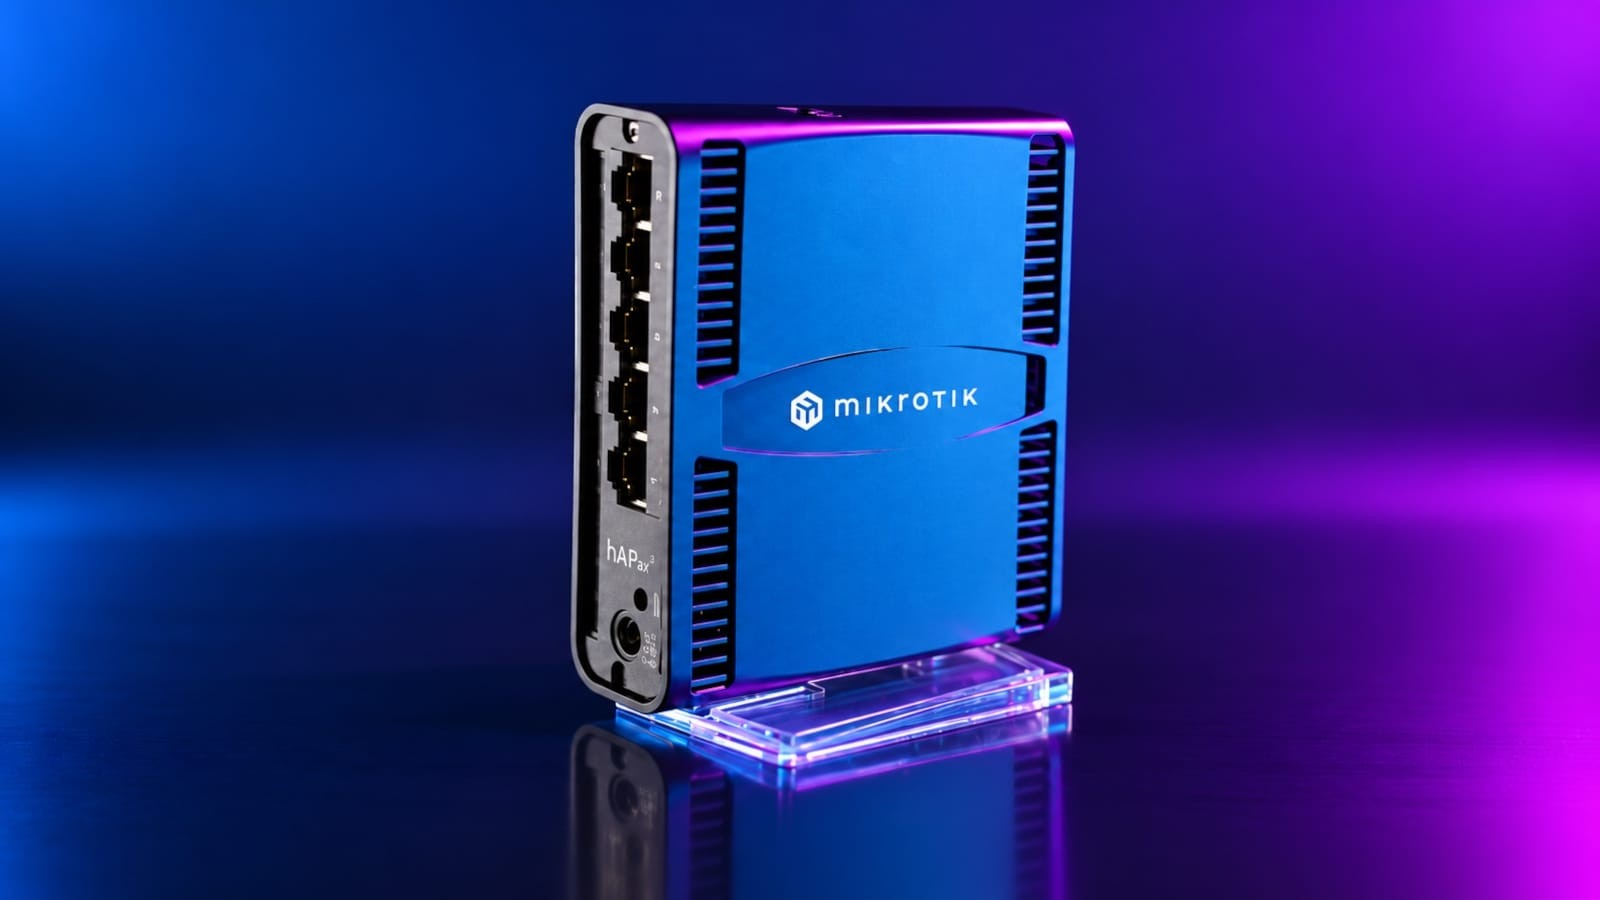
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has raised alarms over a newly identified critical security flaw affecting MikroTik RouterOS. This vulnerability could potentially allow malicious actors to achieve remote code execution and compromise targeted network devices.
According to BleepingComputer, the security gap poses significant risks, potentially leading to unauthorized system access or causing denial-of-service conditions if exploited. Network devices operating on vulnerable versions of the software remain primary targets for threat actors.
Cybersecurity experts and CISA strongly advise network administrators to apply available security updates and patch their MikroTik devices immediately. Failing to update firmware in a timely manner leaves critical infrastructure exposed to potential automated attacks.
This advisory highlights the ongoing necessity for strict vulnerability management across enterprise and provider networks globally. Maintaining up-to-date firmware and monitoring device logs remain essential practices for mitigating advanced cybersecurity threats.


