Linux Kernel TCP Flaw CVE-2026-98432 With 9.8 CVSS Score Affects Ubuntu and RHEL
A critical TCP flaw in the Linux kernel gets a 9.8 CVSS score, affecting Ubuntu and RHEL. Anthropic's AI model successfully wrote an exploit for it.
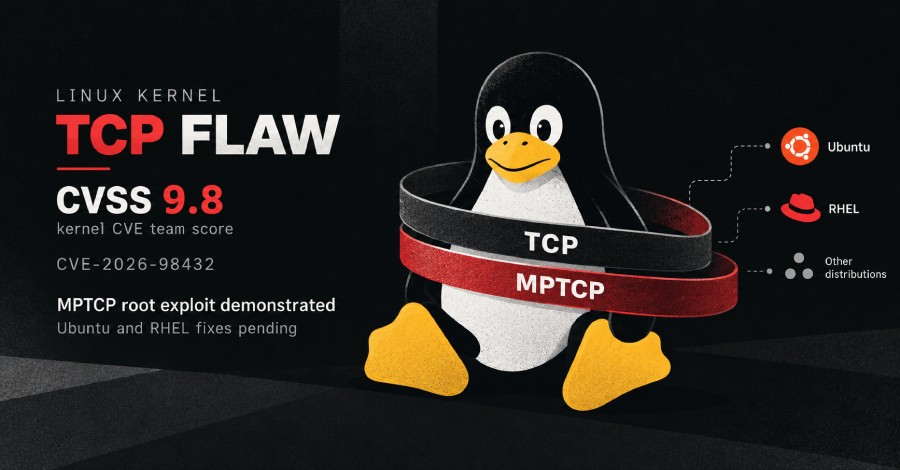
A severe flaw in the Linux kernel's TCP code, tracked as CVE-2026-98432, has been discovered and is affecting major distributions. The kernel's security team has rated this vulnerability at 9.8 out of 10 on the CVSS scale, highlighting its critical nature.
- The vulnerability impacts popular Linux distributions including Ubuntu and Red Hat Enterprise Linux.
- The severity score on the CVSS scale is rated at 9.8 out of 10.
- Anthropic announced that its AI model wrote an exploit utilizing this specific flaw.
Vulnerability Details and Server Risks
The issue resides within the network stack and TCP implementation of the Linux kernel. Due to the nature of the flaw, an unauthenticated remote attacker could potentially execute arbitrary commands with root privileges on targeted Linux servers.
This poses a significant threat to countless enterprise servers running these widespread distributions. System administrators must closely monitor security advisories and prepare to apply patches as soon as they become available.
Read alsoOfficial Claude Code VS Code Extension Compromised for SSH BackdoorThe Role of Artificial Intelligence in Exploitation
Anthropic revealed that on October 27, its AI model successfully generated an exploit that leverages this flaw to achieve remote execution. This demonstrates the accelerating capabilities of modern language models in synthesizing functional attack vectors from vulnerability disclosures.
Such developments illustrate how automated tooling can drastically shrink the window of exposure between vulnerability publication and the emergence of working exploits, reshaping modern threat modeling.
What This Means for IT Professionals and Business
For businesses and system administrators, this discovery requires immediate attention to kernel patch management and infrastructure auditing. Because foundational enterprise distributions like Ubuntu and RHEL are affected, applying security updates promptly is critical to preventing potential remote breaches.
Source: The Hacker News