
Cyber
Hackers Hijack Convertr Analytics Script to Steal Payment Card Data
A credit card skimming group compromised Convertr's analytics script to steal payment card details from online shoppers during checkout.
Category
Defense, threats, security strategy and auditing.
605 articles
A credit card skimming group compromised Convertr's analytics script to steal payment card details from online shoppers during checkout.
Microsoft has released emergency Windows updates to revoke trust in compromised eMudhra certificates, protecting systems without automatic updates.
The popular Warp agentic development environment suffered a security breach involving a third-party vendor, exposing user telemetry and AI agent decision logs.
The U.S. cyber agency has issued a warning that hackers are actively exploiting critical bugs in PHP software, which powers a vast majority of the web.
Huntress Labs has released a new threat ranking detailing how attackers abuse legitimate IT tools and Microsoft 365 to bypass traditional defenses.
The Tailscale security team is working to patch almost a dozen security vulnerabilities that could lead to credential theft and root privilege escalation.
Two experienced senators claim the US government is violating the law through electronic surveillance of its own citizens.
Apple has extended crucial security patches to older iPhones and iPads to fix a zero-day bug used in sophisticated attacks.
Apple has rolled out comprehensive security updates across iOS, macOS, watchOS, and other platforms, fixing hundreds of unique bugs.
DreamHost has forced password resets for email and FTP/SFTP accounts after an incident disrupted its File Manager interface.
A critical flaw dubbed 'HTTP2Shell' in Brotli, the C decoder library built into Node.js, could allow attackers to corrupt memory and access sensitive data.
Two critical RCE vulnerabilities tracked as PHP2Shell are now being actively exploited by threat actors in real-world attacks.
A new UEFI bootkit called BlackX, active in early 2026, leverages the Baton Drop vulnerability to bypass Secure Boot and target security software.
Security researchers remotely disabled a vulnerable updater in the abandoned Time4Popcorn app, closing a major security flaw.
Microsoft has announced plans to integrate AI-powered phishing detection into Teams messages, set to roll out in early November 2026.
HPE has rolled out security updates addressing 72 vulnerabilities in ArubaOS, including eight maximum-severity remote code execution and auth bypass flaws.
Cloud platform Railway issued an urgent warning to users after detecting suspicious activity on systems storing customer environment variables.
Japanese gaming giant Capcom has confirmed a security breach on its CAPCOM ID membership service, exposing millions of user records.
Hackers compromised the LiteLLM project's PyPI package and published malicious Docker images designed to steal credentials and environment variables.
Arista Networks has released security updates to patch an actively exploited zero-day vulnerability affecting VeloCloud Orchestrator On-Prem deployments.
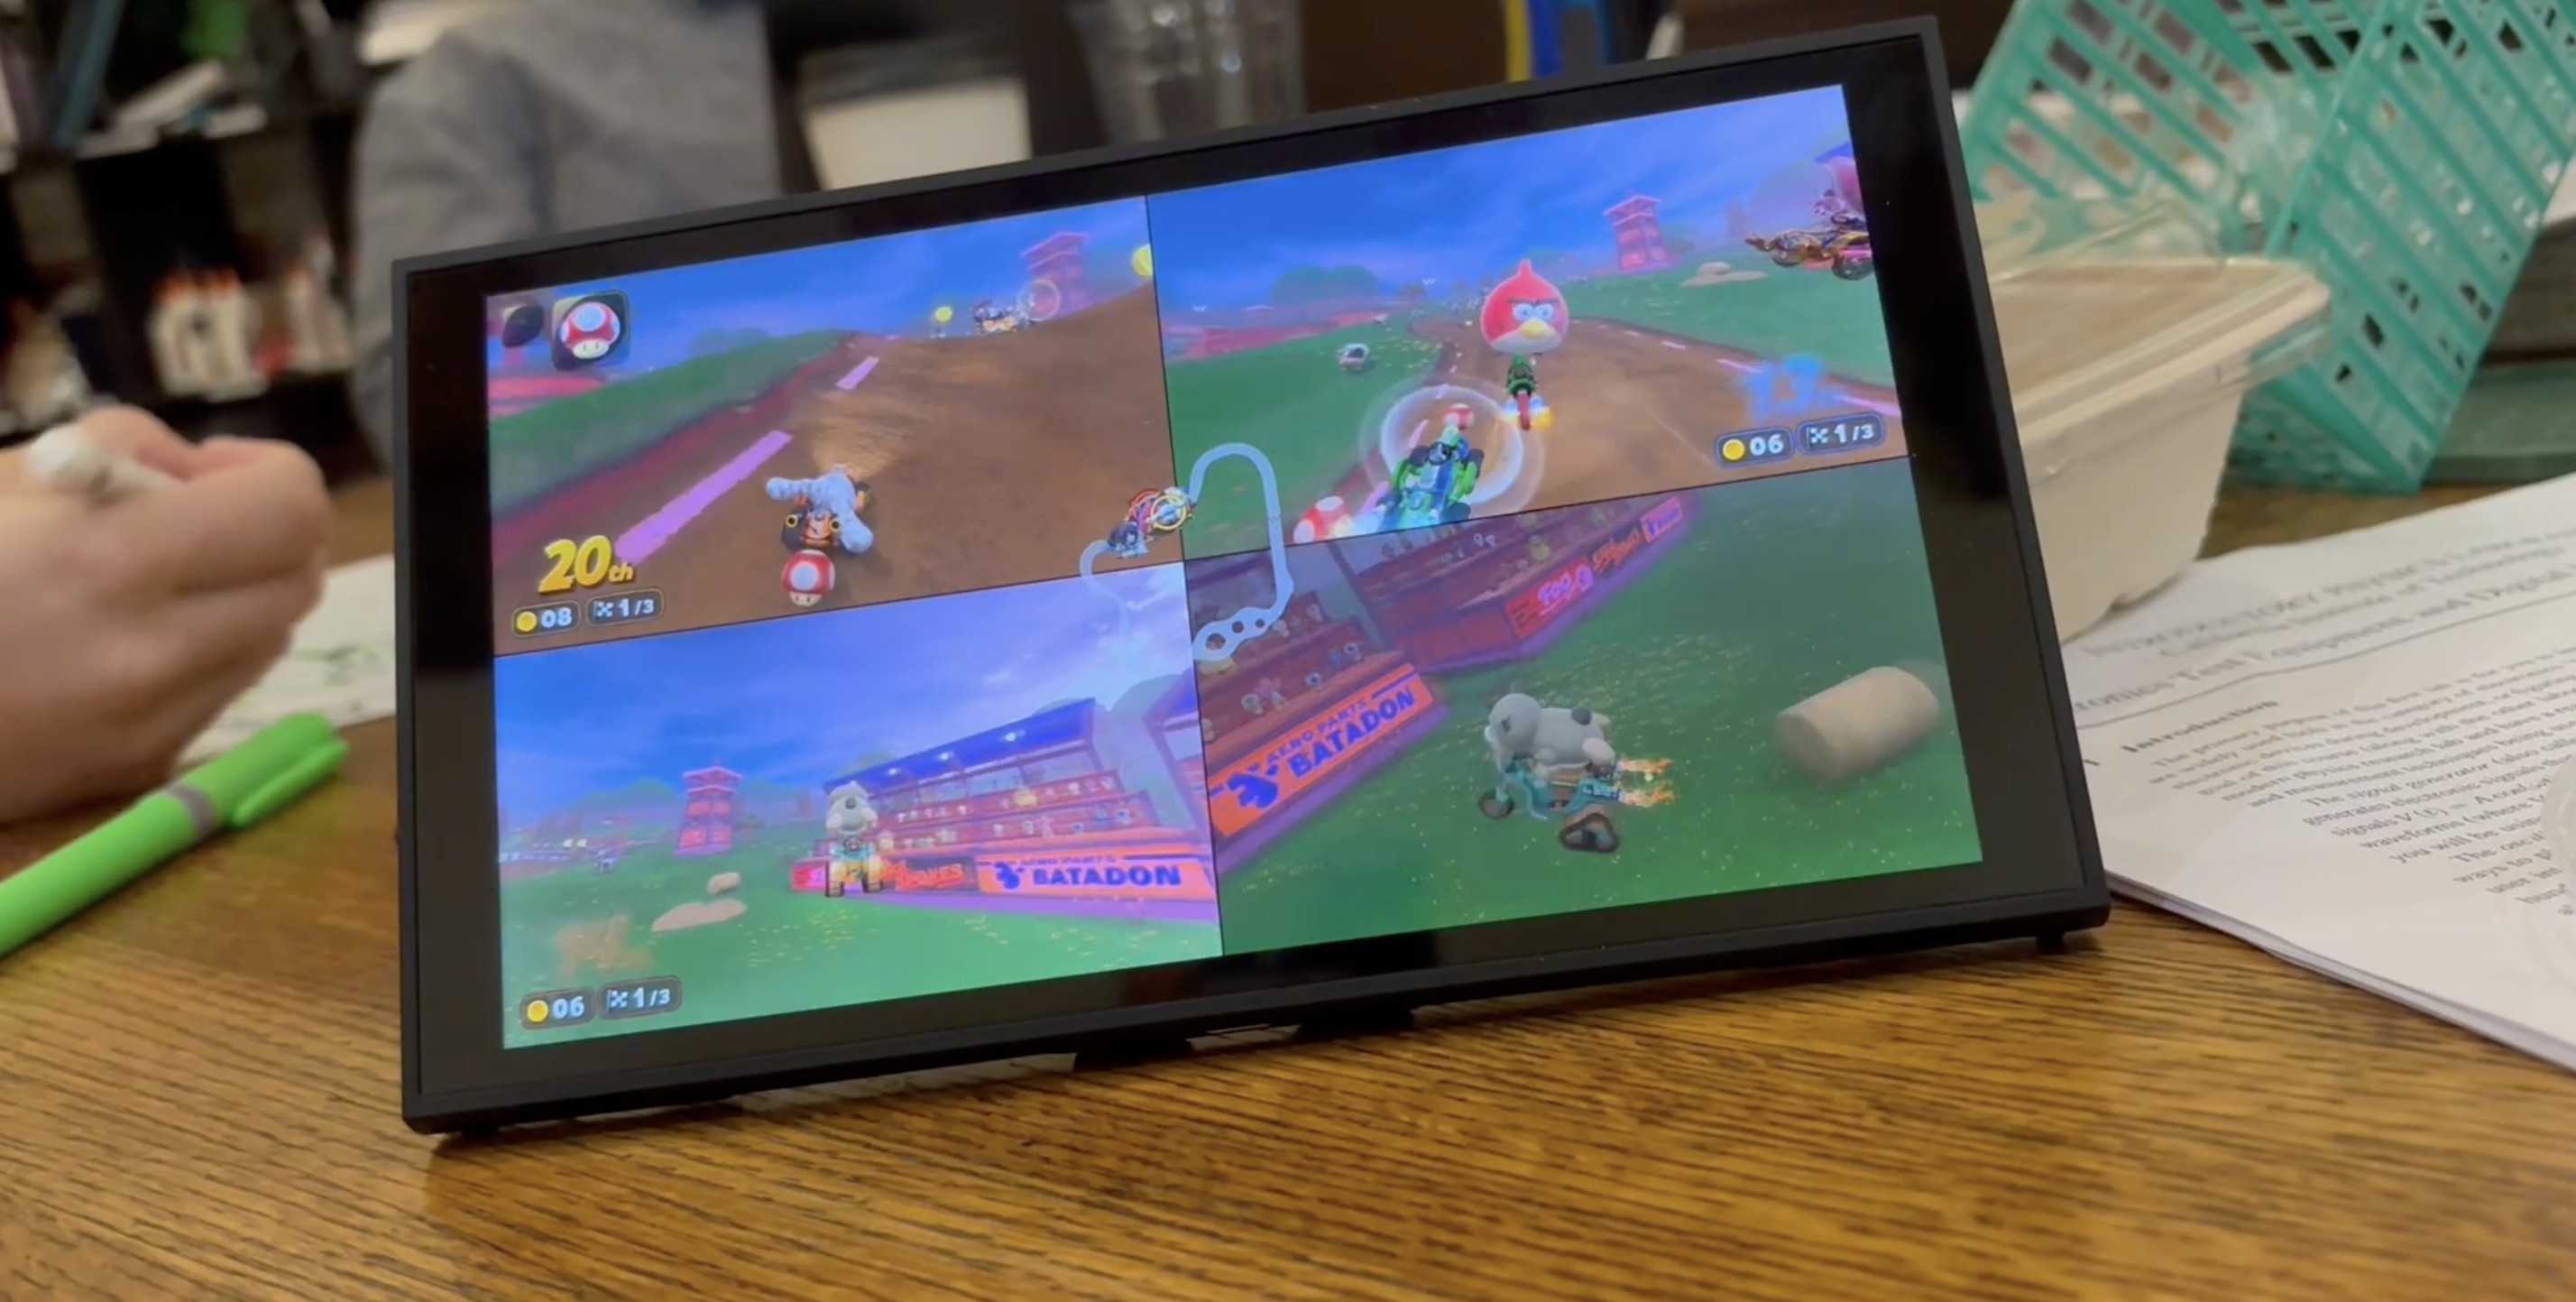
The Nintendo Switch 2 has reportedly been jailbroken, featuring custom Mario Kart World characters built with the help of OpenAI's Codex.
Security researchers at Amazon reveal that critical PHP flaws affecting websites worldwide were targeted by hackers days before official patches became available.
Microsoft blames a China-aligned hacker group for the ConnectWise breach, noting they used AI agents to rapidly compromise thousands of customers.
Newly discovered flaws in the widely used programming language threaten millions of websites and platforms across the global internet.