
Cyber
Binance Hack Impacts India's Largest Crypto Exchange Amid Futures Restrictions
Following recent security issues related to Binance, India's largest crypto exchange has been forced to curb its futures trading operations.
Category
Defense, threats, security strategy and auditing.
605 articles
Following recent security issues related to Binance, India's largest crypto exchange has been forced to curb its futures trading operations.
Major security challenges persist in the crypto space as stolen funds are moved into unfreezable wallets, sparking industry-wide concerns.
Following a recent security incident on Binance, major investors are quickly moving their assets away from centralized platforms.
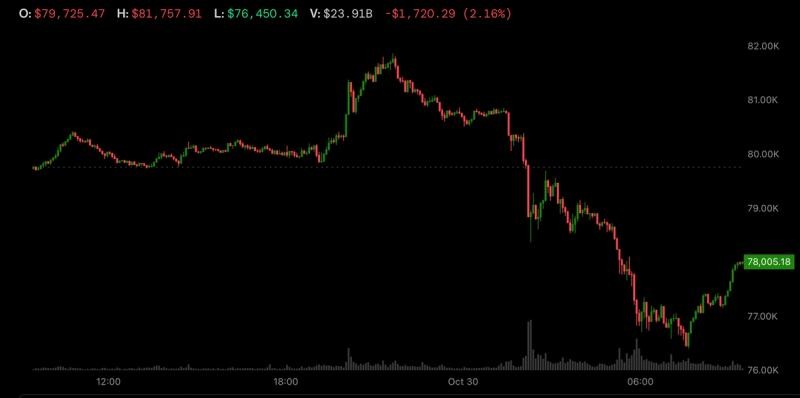
A massive cyberattack on Binance has sent Bitcoin and Ethereum tumbling, with Standard Chartered warning of further struggles ahead for the crypto market.
Blockchain investigators suggest that North Korea-linked Lazarus Group is likely behind the recent security breach and hack targeting Binance.
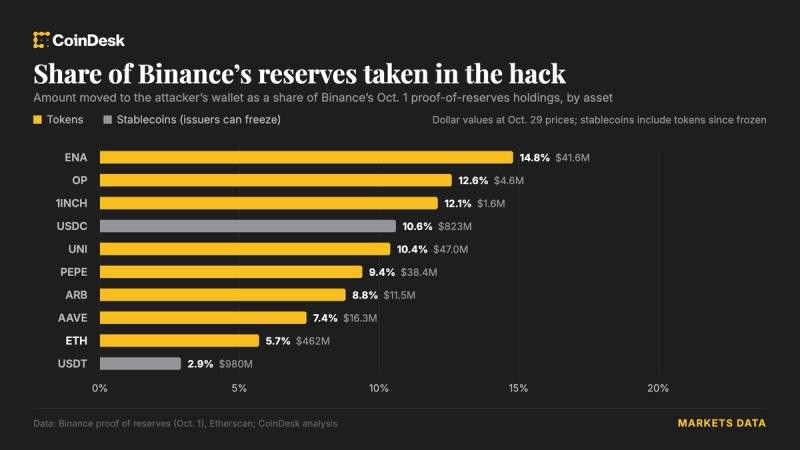
Recent reserve data indicates that a hack on Binance has directly drained the wallets that back customer assets.
Cryptocurrency exchange Binance is investigating a potential security breach involving up to $5.8 billion in digital assets.
Binance, the world's largest crypto exchange, has suffered a major cyberattack, with estimates suggesting billions in crypto may have been stolen.
A crypto-mining campaign abusing Hugging Face models has returned just days after being taken down, targeting GPU servers.
Prediction market platform Polymarket paused trading on Thursday following a third-party service breach that drained approximately $2.5 million in assets.
Binance, one of the world's largest cryptocurrency exchanges, has suffered a multi-billion-dollar hack, significantly impacting the broader digital asset market.
A newly tracked APT group, UAT-11473, is exploiting the CVE-2026-20127 authentication-bypass flaw in Cisco SD-WAN Controllers to deploy the KeyDrift malware.
A total of 319 Chrome extensions with 13.4 million installations were caught hijacking user searches to generate ad revenue for Bing and Yahoo.
Cisco has released urgent security updates to address a zero-day denial-of-service vulnerability in ASA and FTD software actively exploited in attacks.
The US Department of Homeland Security suffered a major data breach, exposing personal information of tens of thousands of employees.
American authorities have seized the main domain of Virtualine, a bulletproof hosting service heavily used by ransomware operators and cybercriminals.
Personally identifiable information of over 40,000 DHS staffers, including CBP and ICE agents, has been published online.
Recent critical bugs in PHP have sent organizations scrambling to patch their systems. Experts warn that the cleanup process is far from over.
Chinese state-sponsored threat group Volt Typhoon is utilizing the 'Silent Train' framework to conceal attacks targeting high-value systems.
Attackers are actively exploiting vulnerabilities in critical network infrastructure, with PHP flaws known as PHP2Shell putting web management interfaces of firewalls and VPNs at risk.
The US Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that hackers have started exploiting a critical Brotli vulnerability known as Node2Shell.
A Ukrainian national was sentenced to 70 months in prison for his role in ransomware attacks targeting hospitals and government entities.
Major South Korean cryptocurrency exchange Bithumb has suffered a cyberattack executed through its internal employee systems.
The GMO Group has asked customers to disconnect from the internet and shut down computers following a security breach affecting Onamae Desktop Cloud.