
Cyber
Hackers Exploit Collabora RCE Flaw to Backdoor Nextcloud Servers
Threat actors are actively exploiting a critical command execution vulnerability in the Collabora Online app for Nextcloud.
Category
Defense, threats, security strategy and auditing.
605 articles
Threat actors are actively exploiting a critical command execution vulnerability in the Collabora Online app for Nextcloud.
A widespread proxyjacking campaign has impacted network devices across 34 countries, monetizing victims' internet connections.
Threat actors uploaded malicious packages to the Arch User Repository, impersonating popular helper tools yay and paru.
Security researchers found that an Israeli ad tech firm worked with spyware companies to infect user devices simply by displaying online ads.
Citizen Lab discovered evidence that numerous devices at Al Jazeera were hacked after exposure to malicious online advertisements.
Palo Alto Networks has rushed out security updates to address a high-severity PAN-OS zero-day RCE vulnerability that is actively being exploited against firewalls.
Microsoft and Japan's National Police Agency have teamed up to dismantle a massive cybercrime marketplace responsible for over a billion phishing messages.
Law enforcement agencies worldwide have dismantled a massive cybercriminal ecosystem targeting over 75,000 organizations across 150 countries.
A newly discovered Android malware named Hirudo is stealing banking credentials by substituting legitimate financial apps with modified versions.
Microsoft has confirmed that non-admin users may experience Remote Desktop connection failures after recent Windows updates if the Administrator protection security feature is enabled.
Authorities say sanctioned North Korean hackers are using US citizens as intermediaries to link breached firms with Pyongyang.
A critical heap buffer overflow vulnerability in Ghostscript allows remote code execution and server hijacking via specially crafted PDF files.
Microsoft's October Patch Tuesday features a record 1,411 security fixes, including one actively exploited and two publicly disclosed zero-day flaws.
Ivanti has urged customers to immediately patch a zero-day vulnerability in its Connect Secure remote access gateway that is being actively exploited.
Cybercriminals continue to bypass multi-factor authentication by targeting systems that still rely on passwords alone, such as VPNs, RDP and Windows endpoints.
In its October 2026 security updates, SAP patched 20 vulnerabilities, including a maximum‑severity OAuth2 SSRF flaw in the Cloud SDK for Python.
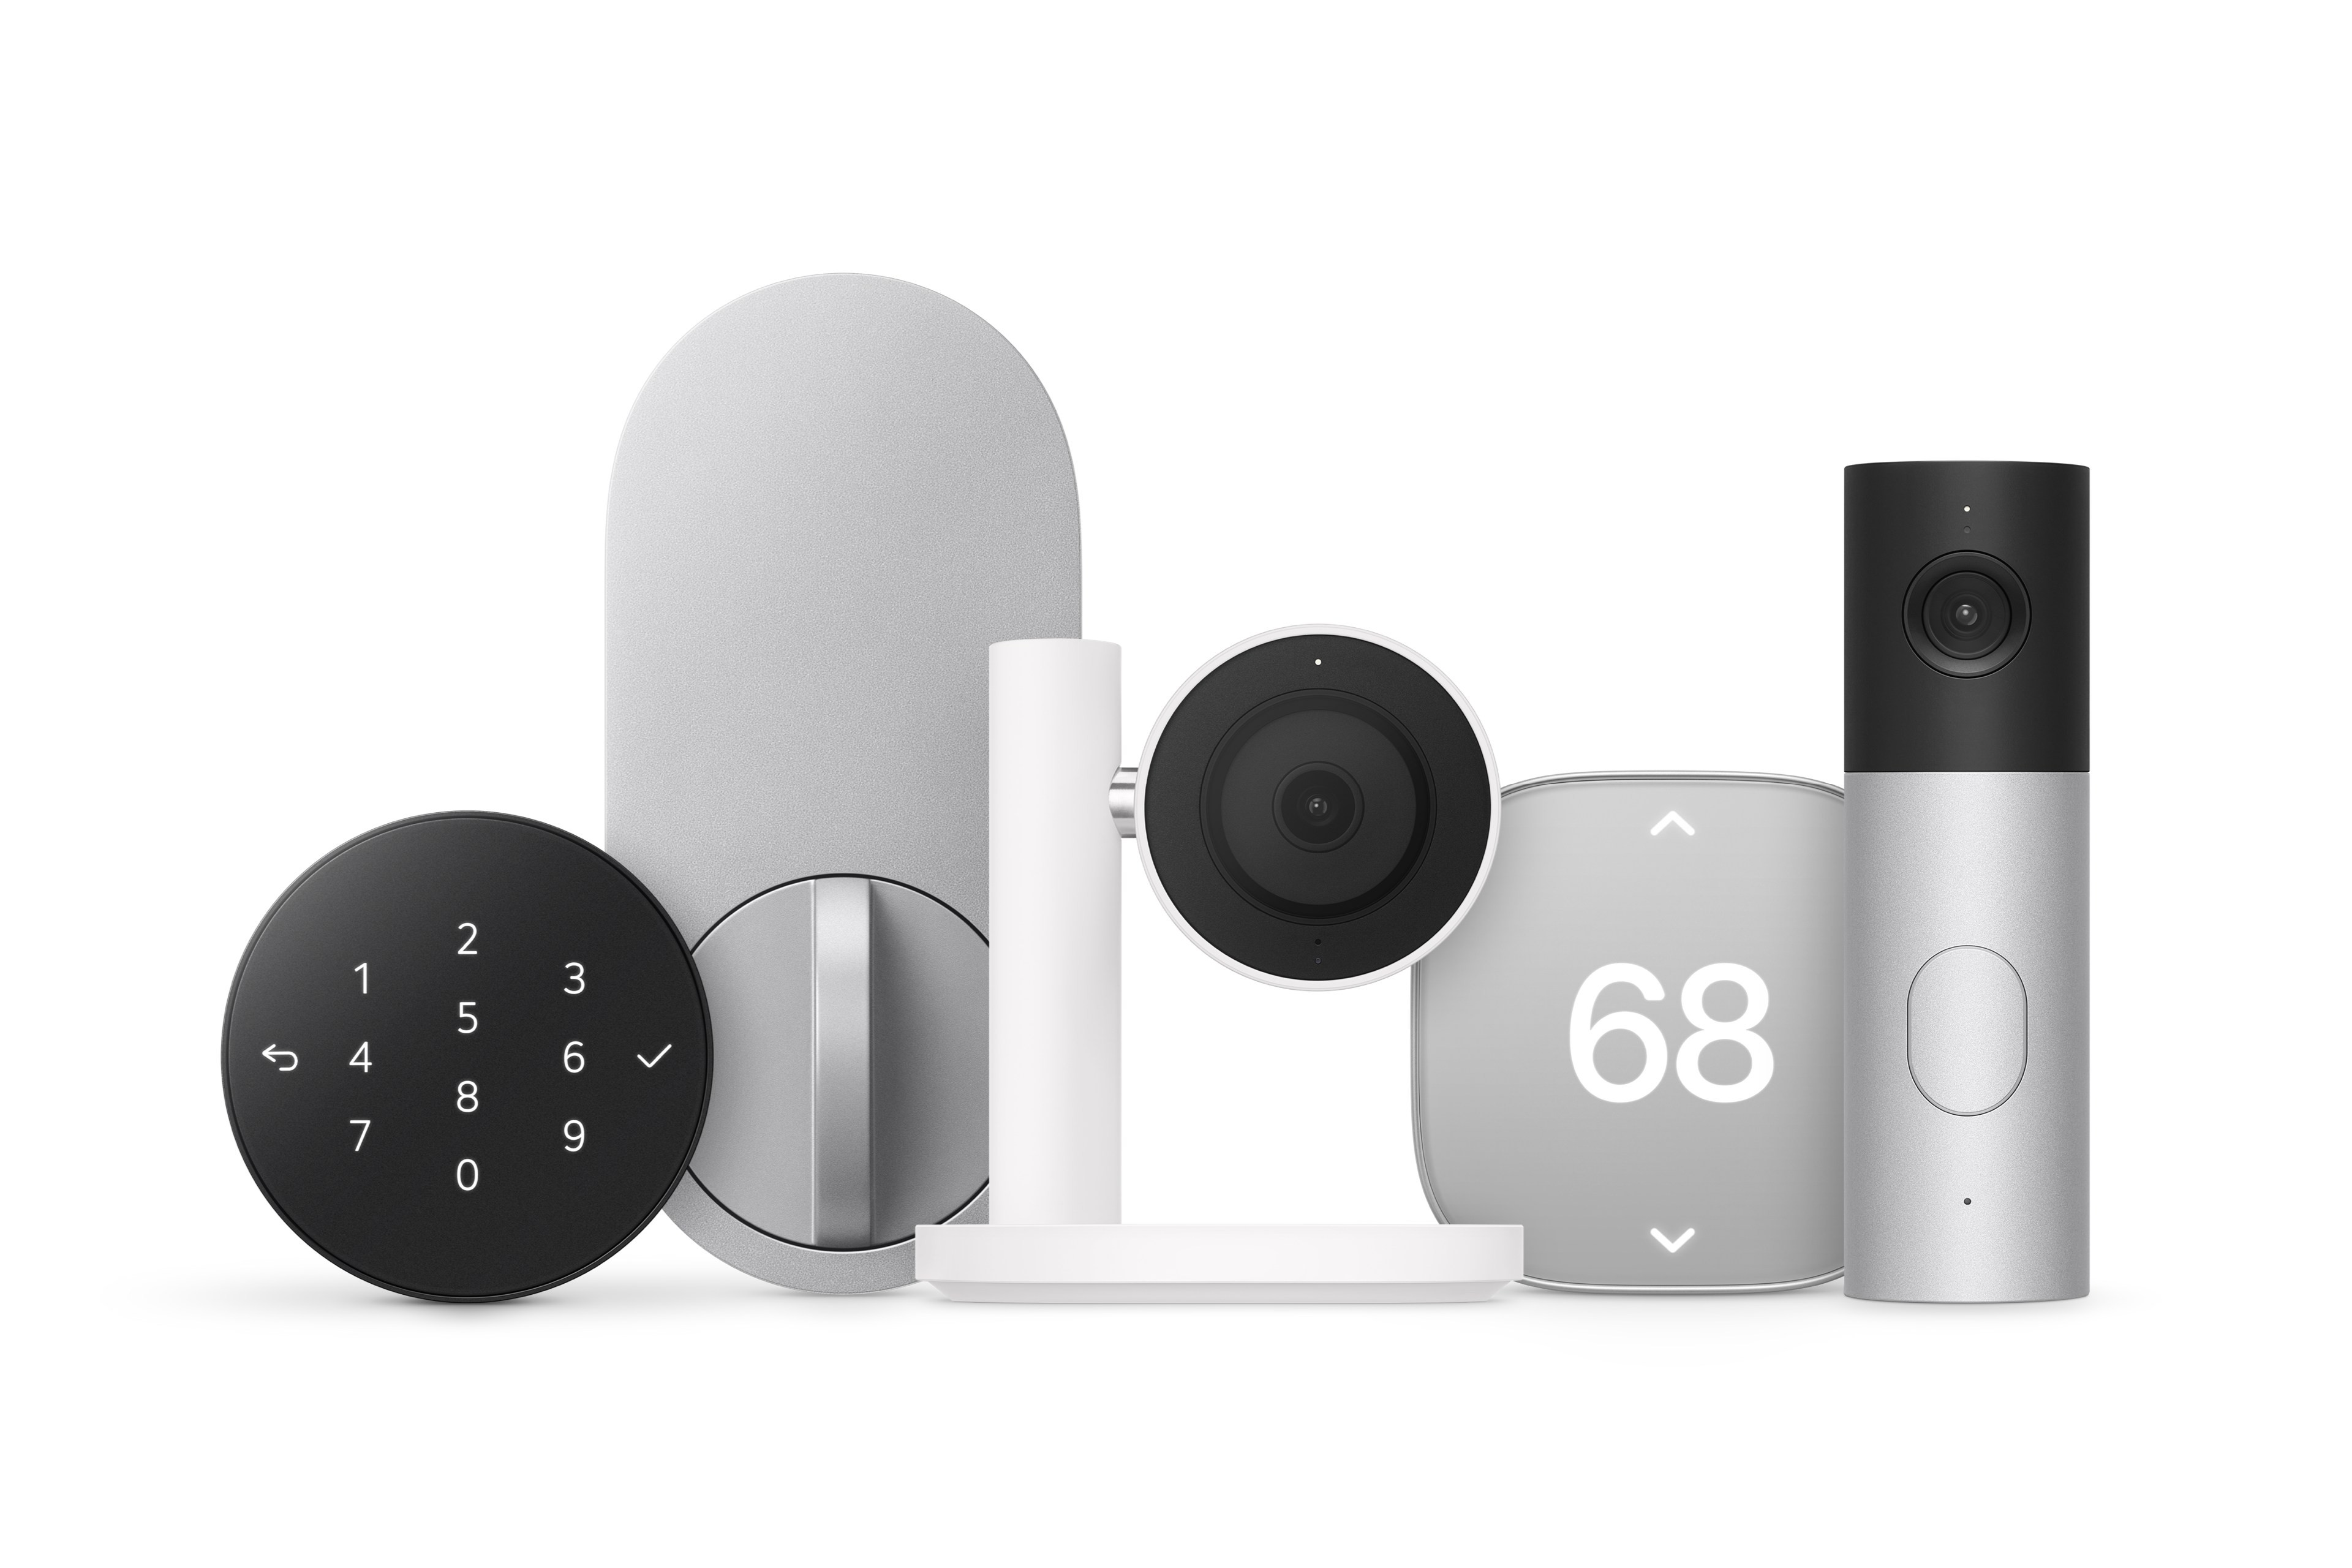
Apple has teamed up with LG Electronics and Schneider Electric to introduce the Apple Home Collection, a set of easy‑to‑install smart home devices.
Norway's Data Protection Authority has fined Microsoft-owned advertising company Xandr $9.6 million for unlawfully processing and sharing sensitive user data from Grindr.
Yandex cloud services experienced major disruptions and user file access loss following drone attacks that damaged three data centers.
Anthropic revokes internet access for high-risk AI test models following security incidents involving U.S. government websites.
Attackers remotely defrosted refrigeration units at multiple French supermarket chains overnight in a targeted cyberattack.
Global food retail giant Ahold Delhaize confirmed it took several systems offline following a cybersecurity incident affecting its network.
GitLab has urged users to immediately patch a maximum-severity vulnerability in the CI/CD Regular Expression Compiler allowing remote code execution.
Canadian cybersecurity executive Edward Dubrovsky has been arrested in Pennsylvania over alleged extortion activities.