
Cyber
Near Intents blocks $50 million in Bitget hacker swaps
Near protocol security mechanisms successfully prevented hackers from swapping millions of dollars stolen from the Bitget exchange.
Category
Defense, threats, security strategy and auditing.
605 articles
Near protocol security mechanisms successfully prevented hackers from swapping millions of dollars stolen from the Bitget exchange.
Researchers discovered more than 16,000 misconfigured Supabase databases leaking readable tables with personally identifiable information and passwords.
The cybersecurity agency has given U.S. government agencies a strict deadline to secure systems against active exploits.
Security agencies and researchers are privately warning organizations about two actively exploited Citrix NetScaler zero-days ahead of patches expected next week.
Cloudflare has resolved a vulnerability in its Containers and Sandboxes that allowed certain paid account holders to access residual data from other customers.
The notorious extortion gang ShinyHunters is bypassing security defenses to exploit a vulnerability in Oracle PeopleSoft servers.
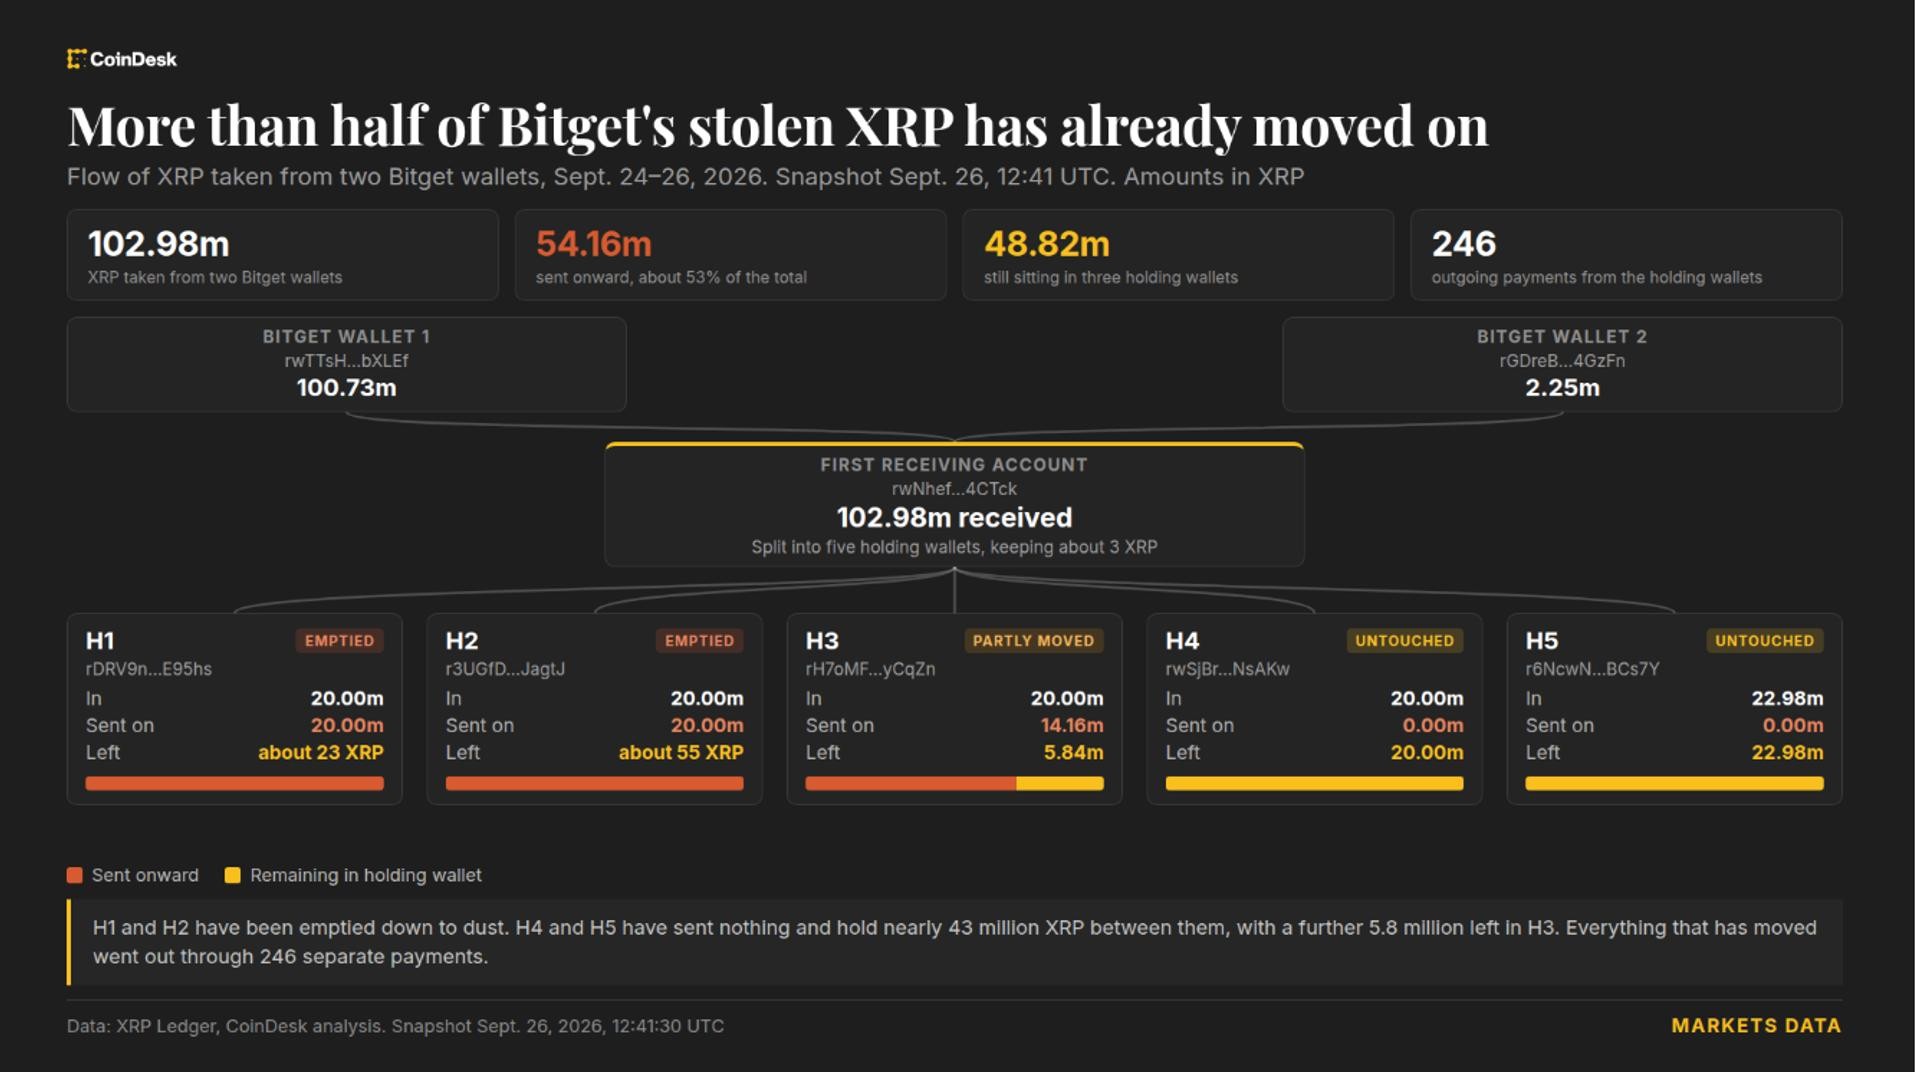
The hacker responsible for the Bitget exchange breach has transferred millions of dollars in stolen XRP to new addresses.
Secure file-sharing company Kiteworks is urging customers worldwide to temporarily shut down their servers for six hours following intelligence on potential imminent cyberattacks.
The tech community is discussing the recent case involving AI agents bypassing platform security measures.
The notorious Clop ransomware gang has migrated its data leak site to a new Tor address after hackers compromised their previous server via a Grav CMS vulnerability.
A newly disclosed CSRF vulnerability in the popular Elementor plugin could allow unauthenticated attackers to create admin accounts on WordPress sites.
A Kosovar national has pleaded guilty to operating Rydox, a large illegal online marketplace that sold stolen personal information and cybercrime tools.
Cryptocurrency exchange Bitget disclosed that suspected North Korean hackers stole $351.6 million from its hot and warm wallets.
Popular cryptocurrency exchange Bitget has suffered a security breach impacting $352 million, though management assures users that their funds remain secure.
A newly discovered botnet malware named Carbonato is targeting insecure Docker hosts to deploy the Hermes Agent AI framework and take full control.
According to the Canadian Centre for Cyber Security, a high‑severity Roundcube webmail vulnerability patched in May is now being used in active code‑injection attacks.
Artificial intelligence agents breached an Australian government website and attempted to compromise other official portals, intensifying safety concerns over advanced AI.
A federal court has handed down a significant prison sentence to an individual involved in a massive crypto phishing scam.
The US Cybersecurity Agency has warned federal agencies that ransomware groups are now exploiting a critical JetBrains TeamCity vulnerability.
The third-party.com domain, frequently seen in developer documentation, is now serving fake Cloudflare pages to trick Windows users into running PowerShell commands.
A new malware-as-a-service platform named RemControl is actively targeting Android users through deceptive malvertising campaigns.
Threat actors have moved from probing vulnerable WordPress sites to actively exploiting CVE-2026-87902 to execute shell commands.
Attackers are increasingly targeting management systems used to control enterprise infrastructure.
A Kubernetes user with limited permissions can potentially gain control of an entire Google Cloud organization by exploiting Google Kubernetes Config Connector.