
Dev docs placeholder domain weaponized in recent ClickFix attacks
The third-party.com domain, frequently seen in developer documentation, is now serving fake Cloudflare pages to trick Windows users into running PowerShell commands.
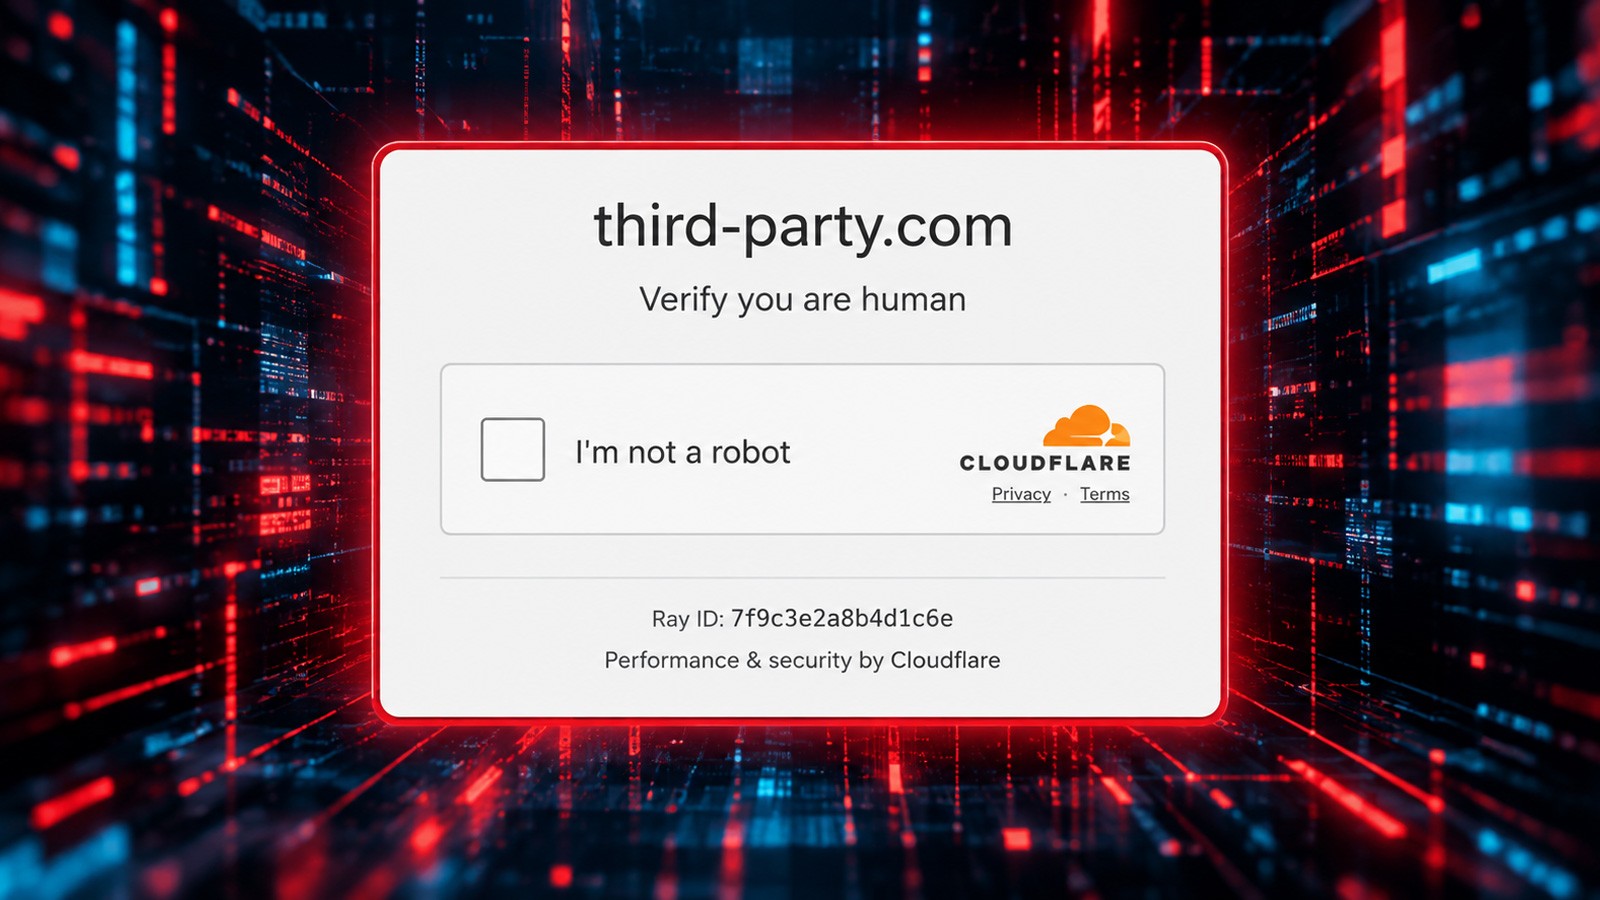
According to BleepingComputer, the "third-party.com" domain, which is commonly utilized as a placeholder in developer documentation and various code examples, has been repurposed for malicious activities. Instead of basic placeholder content, it is now serving deceptive security verification pages.
The ongoing campaign specifically targets Windows users by displaying a fake Cloudflare verification prompt. Victims are tricked into executing PowerShell commands on their systems under the guise of completing a standard browser or security check, representing a growing trend of ClickFix attacks.
Security analysts emphasize that this tactic successfully preys on developer habits and trust in standard reference materials. Because the malicious infrastructure mimics legitimate verification flows, unsuspecting individuals are more likely to fall for the social engineering trap.
This incident highlights the hidden risks associated with stale or unmonitored URLs embedded within technical literature and open-source code repositories. Developers and organizations must audit their references and dependencies to prevent potential supply chain and documentation-based threats.
For the broader tech ecosystem, including emerging markets, this serves as a critical reminder to exercise caution when encountering unexpected prompts, verification steps, or script executions derived from online technical guides and examples.


