
Cyber
ReliaQuest Confirms Failed Data-Theft Attack
Cybersecurity firm ReliaQuest has confirmed thwarting a social engineering attack targeting one of its employees.
Tag
The latest news, analysis and stories about BleepingComputer — TECC.UZ.
357 articles
Cybersecurity firm ReliaQuest has confirmed thwarting a social engineering attack targeting one of its employees.
Microsoft has confirmed that .NET Framework updates released as part of the August Patch Tuesday are breaking printing and PDF export in WPF applications.
The Cybersecurity and Infrastructure Security Agency (CISA) has ordered U.S. government agencies to patch an actively exploited vulnerability in Zimbra Collaboration Suite within three days.
The ToxicPanda Android malware has evolved with new malicious functionality, expanding its targeting to 349 applications and adding support for 167 remote commands.
A supply-chain attack targeting Android-based car head units is using a legitimate device-update app to spread proxy botnet malware and ad fraud tools.
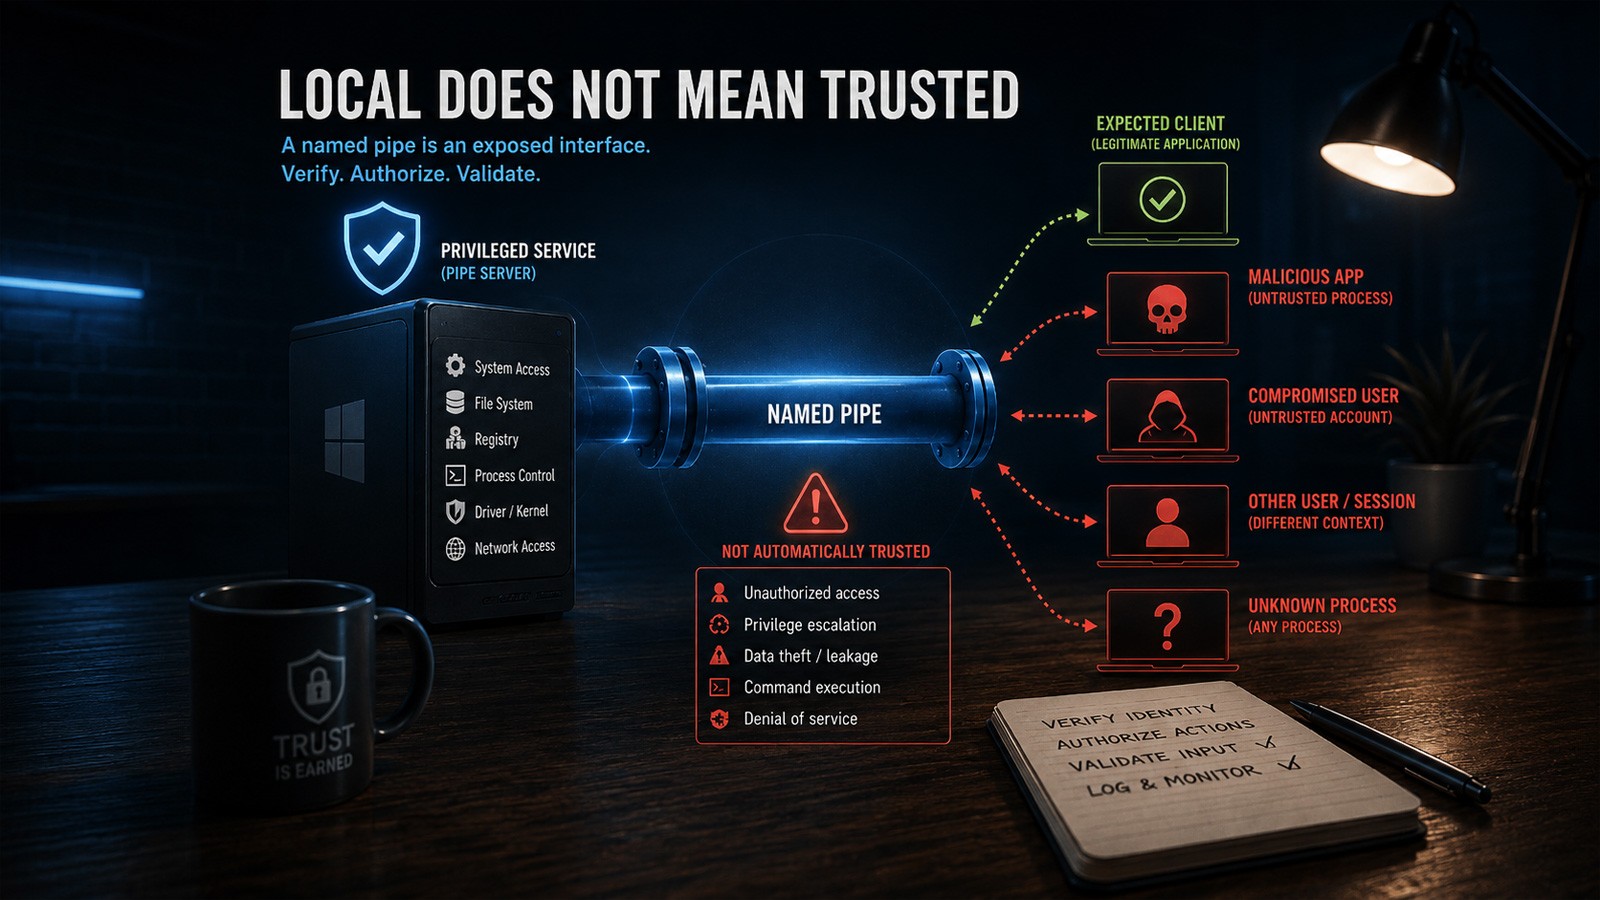
Windows named pipes provide fast interprocess communication, but weak access controls can expose privileged services to untrusted processes.
A previously unknown malware family named SynkLoader is being distributed through Microsoft Teams phishing attacks to steal credentials using a fake lock screen.
New findings reveal that thousands of Amazon Web Services access keys left publicly exposed remain active and valid.
Threat actors are abusing FTP banners to hide commands that deliver two previously undocumented remote access trojans named E4del and PINHOLE.
Microsoft has patched a maximum-severity vulnerability in the Entra ID identity and access management platform.
Attackers compromised the maintainer account of the popular Rust arrayref crate, injecting malware that executes on developers' systems during compilation.
A critical vulnerability in the Elementor Pro WordPress plugin could allow attackers to upload executable files for remote code execution on the server.
Kaseya outlines how managed service providers can detect and contain sophisticated AI-driven phishing threats that bypass traditional inboxes.
Citrix has warned customers to swiftly secure their systems against two vulnerabilities impacting NetScaler products.
The Cybersecurity and Infrastructure Security Agency (CISA) has warned that threat actors are actively exploiting a critical vulnerability in the MLflow platform.
A new Android malware named Manic targeting users in multiple European countries has a fallback data exfiltration mechanism that uses nearby infected devices.
CERT Polska has issued a warning as attackers begin actively exploiting a critical remote code execution vulnerability in the Zimbra Collaboration Suite.
Microsoft is investigating a potential issue with the August updates that may prevent some games from launching or cause them to crash on affected Windows 11 systems.
Users worldwide are experiencing issues signing in, creating new accounts, and loading previous conversations on ChatGPT.
Japanese cloud and data center provider Sakura Internet disclosed a cyberattack that compromised its sales management system containing customer contract and membership data.
A suspected ransomware affiliate is pretending to be a data recovery service called "Ransom Busters" to extract payments from victims.
A large-scale cyberattack campaign called CameraSwarm has compromised more than 14,500 Dahua IP cameras, mainly in Ukraine and Russia.
U.S. cybersecurity agencies warn that threat actors are using AI-generated scripts to exploit Siemens S7 Series programmable logic controllers.
American authorities have charged 17 Iranian nationals linked to the Mabna Institute hacking-for-hire group over massive data theft operations.