Gitee: 26400 Exposed Cloud and AI Credentials Found in Public Repos
A security researcher discovered 26400 working cloud and AI credentials accidentally left by developers in public code repositories on Gitee.
·1 min read
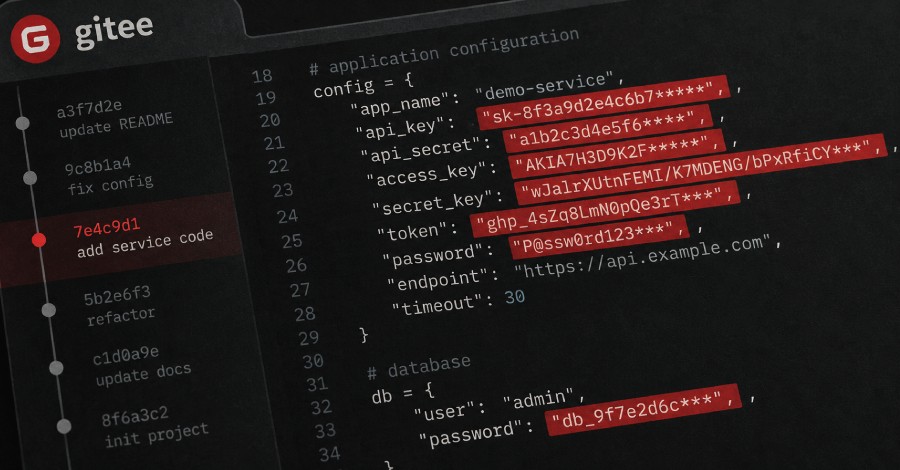
Independent researcher Ben Zimmermann has discovered 26,400 credentials left by developers in public code on Gitee, a major Chinese code-hosting service. Tests confirmed that a significant portion of these exposed keys were still active and fully operational.
- 26,400 working credentials were found.
- The exposure occurred on public Gitee repositories.
- Most of the keys belong to cloud and AI services.
- The findings were reported publicly on October 28.
Scope of the Gitee Discovery Ben Zimmermann uncovered the credentials after scanning an impressive 7.25 million public repositories hosted on Gitee. The scale of the exposure highlights ongoing challenges with secure secret management among developers who inadvertently push sensitive API keys and tokens into public view.
Impact on Cloud and AI Services The majority of the compromised credentials provided direct access to various cloud computing platforms and artificial intelligence services. Anyone who happened to copy these keys from the public source code could have potentially hijacked resources or accessed sensitive data.
Security Implications for Developers Leaving credentials exposed in public repositories remains a persistent risk in software development. This incident serves as an urgent reminder for teams to implement robust secrets scanning tools and adhere to best practices when managing deployment keys and tokens.
Source: The Hacker News