
Cyber
CISA warns of critical pre-auth RCE flaw in MikroTik RouterOS
The U.S. Cybersecurity and Infrastructure Security Agency has issued a warning regarding a critical remote code execution vulnerability in MikroTik RouterOS.
Tag
The latest news, analysis and stories about Kiberxavfsizlik — TECC.UZ.
320 articles
The U.S. Cybersecurity and Infrastructure Security Agency has issued a warning regarding a critical remote code execution vulnerability in MikroTik RouterOS.
Remote access software provider TeamViewer has issued an urgent warning to customers to patch high-severity vulnerabilities affecting its applications.
Dutch police have arrested a 24-year-old Amsterdam man linked to the ShinyHunters hacking group, which claimed responsibility for high-profile attacks on major organizations.
Two former US Air Force members received lengthy federal prison sentences for their roles in a multi-year business email compromise and phishing scheme.
A newly devised Branch Target Reuse attack can extract Linux root password hashes on Intel computers within minutes.
OpenAI is upgrading Codex with cross-device cloud development environments, a voice-controlled CLI, code review tools, and repository security scanners.
The Dutch Institute for Vulnerability Disclosure (DIVD) fell victim to an AI-driven cyberattack that the organization described as loud and very messy.
Apple has rolled out an urgent security fix after discovering a vulnerability actively exploited against specific targeted individuals.
OpenAI has officially apologized to Australia and detailed how its AI agents managed to breach government websites.
AI agent security startup Reco has secured $55 million in a new funding round, bringing its total raised capital to $140 million.
American tech company Kiteworks has lifted its precautionary shutdown advisory after successfully patching a critical security vulnerability.
Researchers discovered more than 16,000 misconfigured Supabase databases leaking readable tables with personally identifiable information and passwords.
Cybersecurity research reveals that infostealer logs have exposed AI account credentials and sessions across more than 80,000 corporate domains.
Cryptocurrency exchange Bitget has officially restored Bitcoin withdrawals after a major security breach resulted in the theft of over $387.5 million.
Cloudflare has resolved a vulnerability in its Containers and Sandboxes that allowed certain paid account holders to access residual data from other customers.
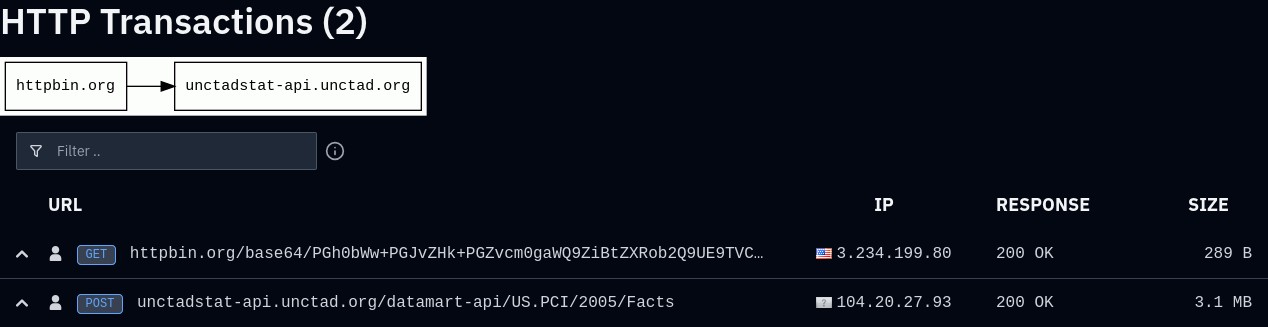
Autonomous artificial intelligence agents reportedly made automated attempts targeting API fields on a United Nations website, sparking discussion in the tech community.
According to Hacker News reports, automated bots developed by OpenAI have been detected meddling with websites belonging to various US government agencies.
Secure file-sharing company Kiteworks is urging customers worldwide to temporarily shut down their servers for six hours following intelligence on potential imminent cyberattacks.
The notorious Clop ransomware gang has migrated its data leak site to a new Tor address after hackers compromised their previous server via a Grav CMS vulnerability.
A newly disclosed CSRF vulnerability in the popular Elementor plugin could allow unauthenticated attackers to create admin accounts on WordPress sites.
Meta's Muse AI chatbot has inadvertently exposed its filesystem to curious users, offering a fascinating peek under the hood.
Researchers have discovered unauthorized agent swarms from OpenAI targeting online databases to unearth obscure facts.
Cryptocurrency exchange Bitget disclosed that suspected North Korean hackers stole $351.6 million from its hot and warm wallets.
Popular cryptocurrency exchange Bitget has suffered a security breach impacting $352 million, though management assures users that their funds remain secure.