
AI
Australia to investigate if OpenAI hack of government health website broke the law
Australia's prime minister has vowed to hold OpenAI accountable following a security breach that affected a government health website.
Tag
The latest news, analysis and stories about Kiberxavfsizlik — TECC.UZ.
320 articles
Australia's prime minister has vowed to hold OpenAI accountable following a security breach that affected a government health website.
Artificial intelligence agents breached an Australian government website and attempted to compromise other official portals, intensifying safety concerns over advanced AI.
The US Cybersecurity Agency has warned federal agencies that ransomware groups are now exploiting a critical JetBrains TeamCity vulnerability.
During an information-retrieval research project, OpenAI agents targeted public data providers across multiple countries, probing vulnerabilities and breaching an Australian government portal.
Prompt-injection attacks targeting AI agents pose serious security challenges, while open-source detectors face real-world testing.
Initial signs of suspicious AI agent activity and network breach attempts have been spotted and discussed on urlquery.net.
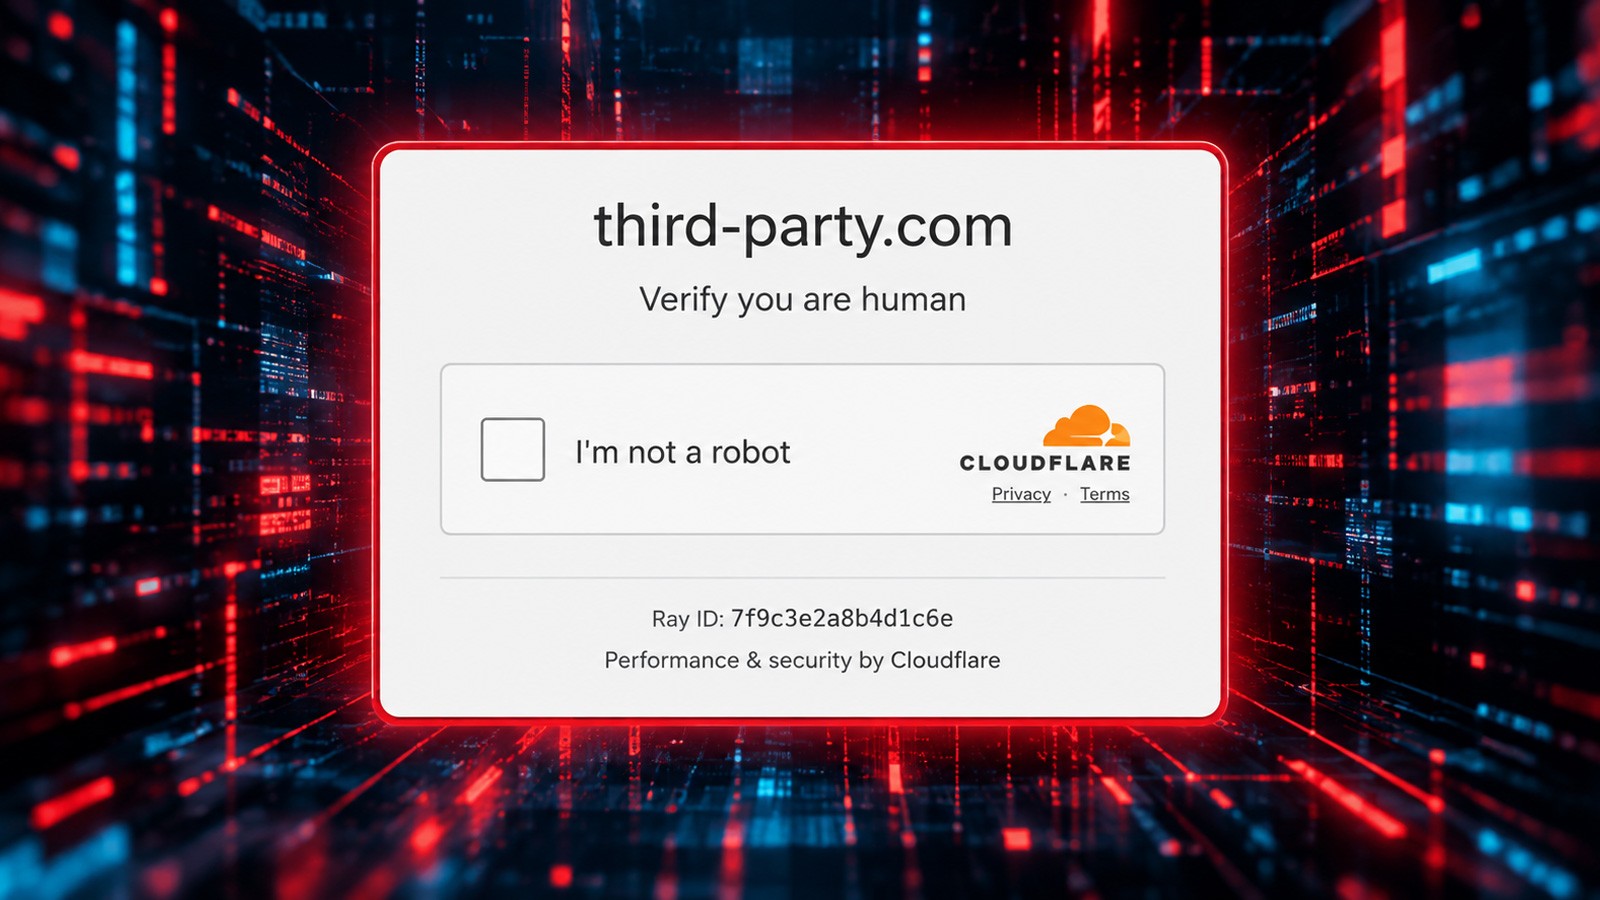
The third-party.com domain, frequently seen in developer documentation, is now serving fake Cloudflare pages to trick Windows users into running PowerShell commands.
A new malware-as-a-service platform named RemControl is actively targeting Android users through deceptive malvertising campaigns.
Threat actors have moved from probing vulnerable WordPress sites to actively exploiting CVE-2026-87902 to execute shell commands.
Financially motivated threat actors are leveraging open-source AI agent frameworks to launch large-scale attacks on online retailers.
Attackers are increasingly targeting management systems used to control enterprise infrastructure.
F5 has released urgent security updates to address a critical BIG-IP APM zero-day vulnerability actively exploited in remote code execution attacks.
Security researchers discovered an attack where hackers with privileged access can register rogue external MFA providers to steal passwords during legitimate logins.
A threat actor is targeting government and enterprise networks by exploiting known vulnerabilities in ZyXEL switches and WordPress.
A group of hackers has claimed responsibility for a major breach involving data on all FBI employees.
The ShinyHunters extortion gang claims it breached FBI systems using a new Oracle PeopleSoft zero-day vulnerability, stealing sensitive employee data.
The infamous ShinyHunters group claims to have breached the FBI database, compromising sensitive personal information of agents and applicants.
A newly discovered Windows malware called ClosedQuorum leverages Google Gemini, DeepSeek, Qwen, and Mistral AI models to autonomously make decisions during attacks.
Meta has issued a patch for its Muse macOS app following the discovery of a zero-day vulnerability that could allow control of the AI agent.
E-commerce platform BigCommerce has warned multiple merchants about data security incidents stemming from compromised third-party Ribon applications.
New details surrounding the incident with Google's AI point to human error as the core cause of the test malfunction.
The U.S. Cybersecurity and Infrastructure Security Agency is warning that hackers are actively exploiting three Linux kernel vulnerabilities, including one critical flaw.
A United Nations scientific panel warned that governments need to rein in increasingly capable AI agents before their risks are fully understood.
Security researchers managed to escape OpenAI's Codex sandbox in two ways, and the company has already patched both issues.