ClickFix attacks are tricking Mac and Windows users into hacking themselves
A rising security threat known as ClickFix is deceiving computer users into executing harmful code via fake online advertisements.
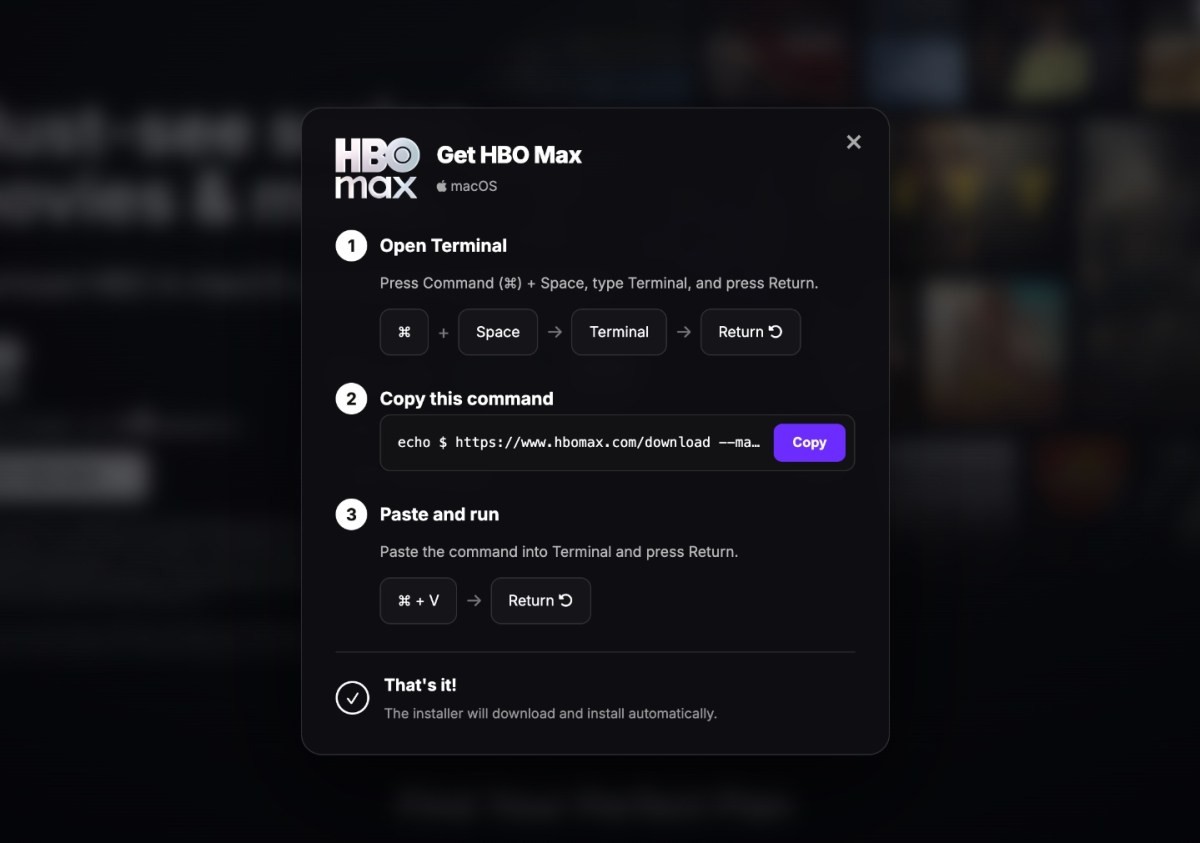
If you clicked on a fake HBO Max ad on Reddit in the past week, you might have fallen victim to a rising ClickFix security threat. This emerging cyber tactic highlights how modern social engineering manipulates everyday internet users.
Unlike traditional malware that exploits system vulnerabilities silently, ClickFix attacks rely on tricking the victim into performing the malicious actions themselves. Attackers often disguise their payload behind fake error messages or browser troubleshooting prompts.
Users are typically instructed to copy and paste a specific command line script into their terminal or PowerShell to fix a non-existent issue. By doing so, the user unwittingly authorizes the execution of malicious software on their own machine.
This clever psychological trick bypasses many automated security defenses because the system believes the action was deliberately initiated by the owner. It represents a worrying trend in how cybercriminals adapt to better security measures.
For technology users in Uzbekistan and beyond, this serves as a critical warning about online vigilance. Avoiding suspicious ads and never pasting unknown code into system terminals remain essential practices for maintaining personal and corporate digital safety.