APT29 Hackers Exploit iOS and Android via Analytics Script
Russia-linked APT29 hackers compromise Ukrainian web analytics service Plerdy SEO Tracker in a massive watering hole campaign targeting mobile users.
·1 min read
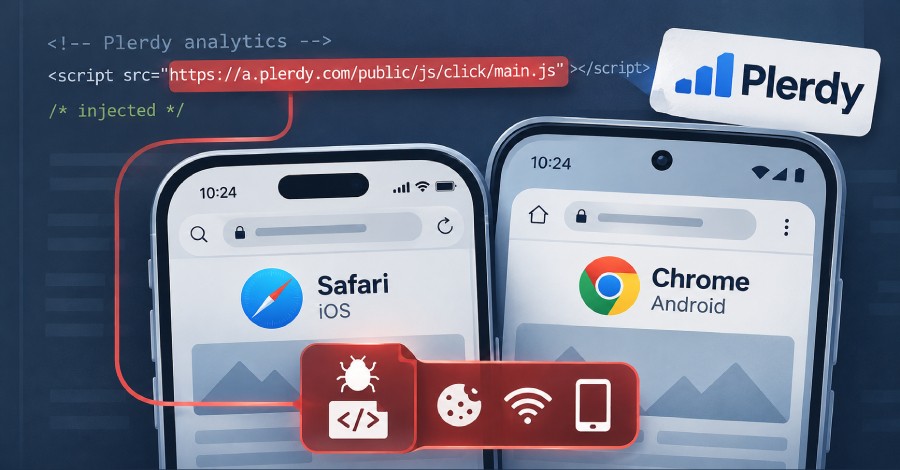
The Russia-linked threat actor group known as APT29 has launched a large-scale cyberattack targeting mobile device users through compromised websites and supply chain tactics.
Key highlights of the attack: - Targets: iOS and Android smartphone users - Method: Supply chain attack and watering hole campaign - Tool: Compromised Plerdy SEO Tracker web analytics script - Threat actor: APT29 (linked to Russia)
Analysis of the Supply Chain Attack Security researchers discovered that the attackers compromised the Ukrainian web analytics service Plerdy SEO Tracker to inject malicious code into legitimate websites visited by targets. The injected JavaScript collects specific browser and device attributes from visitors, allowing threat actors to profile victims before delivering tailored mobile exploits.
Broader Implications for Mobile Security Leveraging legitimate third-party web analytics tools highlights the sophisticated nature of modern supply chain threats. Such vectors make detection extremely difficult for traditional website administrators. Cybersecurity experts continue to monitor the campaign, which utilizes fake domains and compromised infrastructure to target iOS and Android ecosystems globally.
Source: The Hacker News