French blood service fridges hit by cyberattacks
Following a series of attacks on supermarket freezers, French EFS blood storage units were targeted by hackers. No materials were lost thanks to early alerts.
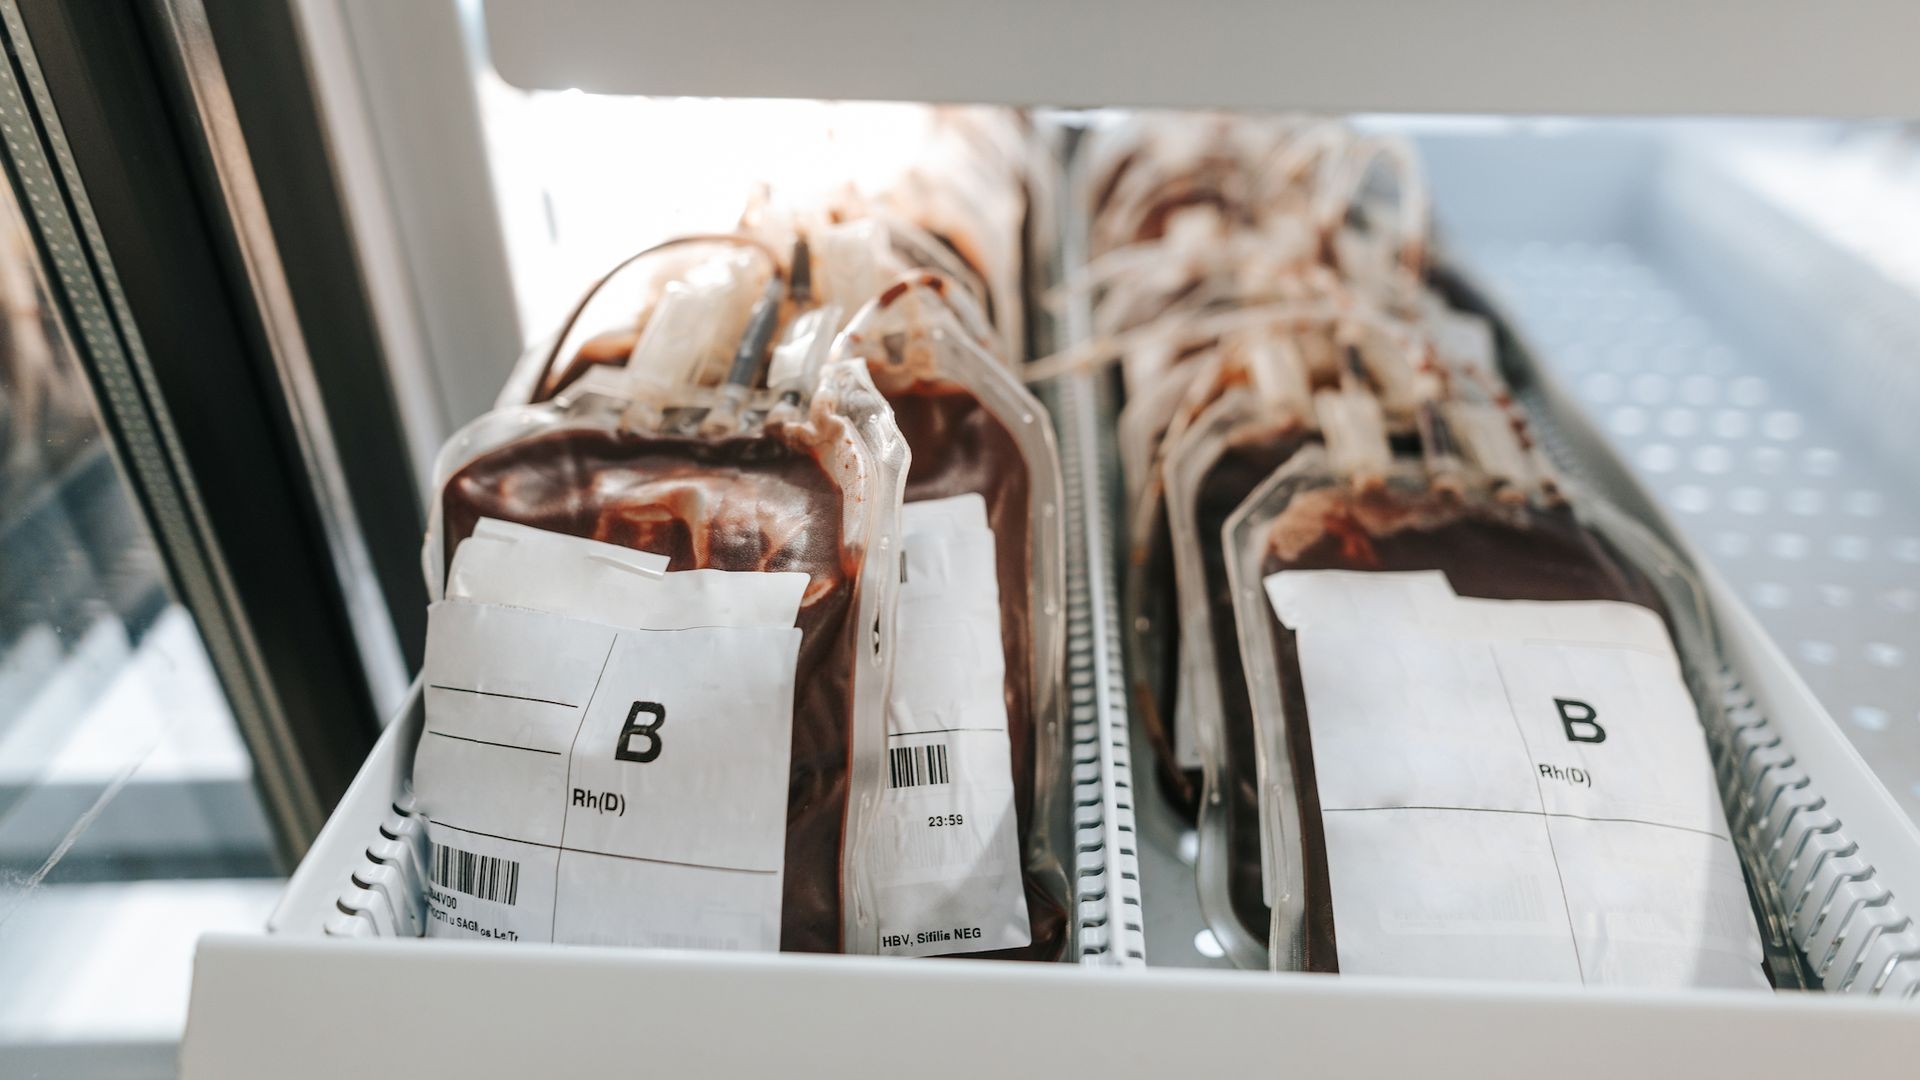
France's blood service, EFS, has become the latest target of cyberattacks aimed at refrigeration units. This incident follows a wave of similar attacks on supermarket freezers across Europe. Fortunately, the EFS' internal monitoring system triggered early warnings, allowing staff to secure biomaterials and prevent any loss of assets.
- The attack originated through a third-party service provider, identified as Coolworld.
- Three EFS sites were affected, including in the Burgundy-Franche-Comté region.
- Russia-aligned hacking groups Noname057(16) and Z-Pentest have claimed responsibility.
- Improperly configured industrial controllers exposed to the internet are the primary vulnerability.
Understanding the Security Gap
The investigation suggests the breach was facilitated by remote monitoring software provided by a third party. While details are scarce, the attack pattern matches previous incidents where industrial controllers, such as those from Danfoss or Copeland/Dixell, were reachable directly from the internet. In many cases, these devices were installed with default settings that left ports (like 80 or 22) exposed to the public web.
Vendor Response and Best Practices
Read alsoFrench Blood Service hacked as refrigeration units are heated to 110 degreesFollowing the initial waves of attacks, manufacturers have issued security advisories urging users to place their controllers behind secure VPNs. This shift in policy marks a necessary move away from legacy installation guides that previously suggested mapping ports for easier external access. However, it highlights the danger of relying on outdated security configurations in modern industrial environments.
Implications for Global Cybersecurity
This breach serves as a stark reminder that legacy industrial control systems are becoming low-hanging fruit for hackers. Businesses must prioritize the isolation of OT/IoT networks from the public internet. Organizations should audit their third-party vendor access and ensure that all remote management interfaces require robust authentication and encrypted tunneling to mitigate the risk of exploitation.
Source: Latest from Tom's Hardware