CERT-In Warns of AI-Driven Cyberattacks by Crafty Falcon Group
CERT-In has issued an alert regarding the Crafty Falcon group, which is using AI-powered tools to target the financial sector and breach critical consoles.
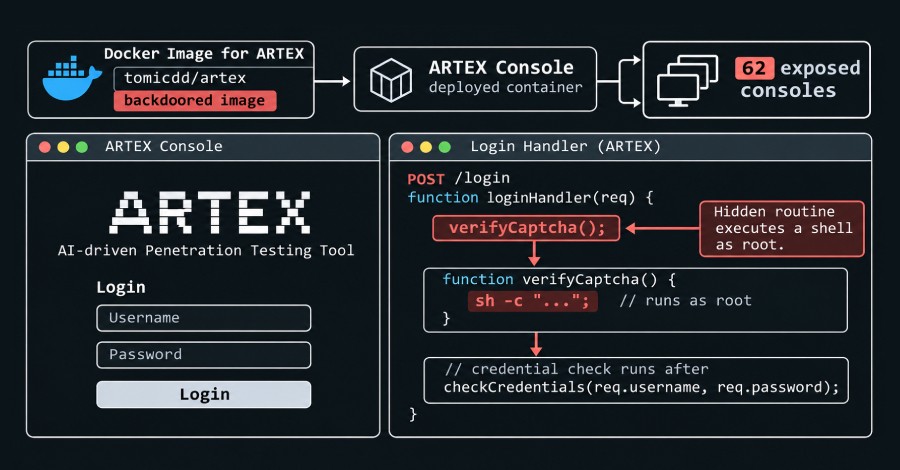
The Indian Computer Emergency Response Team (CERT-In) has disclosed an ongoing threat from a threat actor identified as Crafty Falcon. The group is systematically targeting the Banking, Financial Services, and Insurance (BFSI) sectors by leveraging AI-driven offensive security tools.
- Crafty Falcon is actively targeting the financial infrastructure sectors.
- The attacks leverage publicly available AI-based offensive security tools.
- An ARTEX vulnerability allowed attackers to gain root access to 62 consoles.
Nature of the AI-Enhanced Attacks
The threat posed by Crafty Falcon is significant due to the adoption of AI-assisted methods. By utilizing accessible AI tools, the attackers are able to automate sophisticated reconnaissance and exploitation phases, making these campaigns harder to detect and mitigate using traditional signature-based security systems.
The ARTEX Breach and Root Access
Read alsoCrowdStrike acquires two AI security startups in deals nearing $500MThe activity has resulted in a critical security compromise involving the ARTEX platform. The attackers exploited existing vulnerabilities to gain root access to 62 consoles. This level of access grants the threat actors complete control over the compromised systems, posing a severe risk to data integrity and network security.
Implications for the Security Industry
This incident highlights the democratized threat of AI in cyber warfare. As these tools become more readily available, organizations worldwide must prioritize robust security posture, specifically focusing on advanced anomaly detection and incident response protocols to counter AI-empowered adversaries effectively.
Source: The Hacker News