Government Linux Servers Targeted With SysGoRAT and AI Scripts
Cybersecurity researchers reveal a cyber espionage campaign targeting government Linux infrastructure using SysGoRAT and AI-generated scripts.
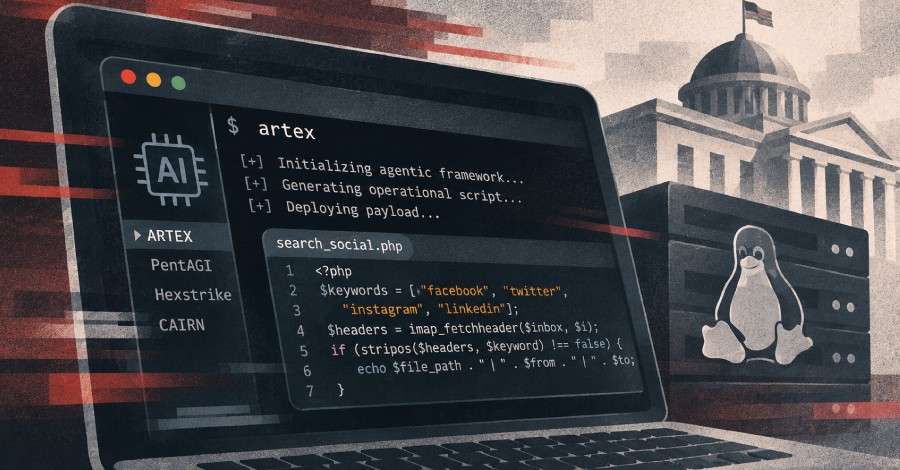
Cybersecurity researchers have disclosed details of a targeted cyber espionage campaign focusing specifically on Linux infrastructure associated with government entities and state-affiliated organizations.
- The activity was observed by Palo Alto Networks Unit 42 between October 2025 and April 2026.
- Researchers are tracking this activity under the moniker CL-UNK-1211, where CL stands for cluster and UNK denotes unknown.
- The attackers utilized SysGoRAT alongside suspected AI-generated scripts to facilitate their operations.
Details of the CL-UNK-1211 Espionage Campaign
The malicious activity was closely monitored by Unit 42 researchers over a six-month period from October 2025 to April 2026. The campaign was explicitly designed for cyber espionage against critical government assets running on Linux environments.
The deployment of SysGoRAT highlights the targeted and sophisticated nature of these intrusions. Furthermore, the suspected use of artificial intelligence to generate operational scripts indicates an evolving trend in how threat actors leverage modern technologies for automated attacks.
Read alsoCVE-2026-98432: Critical TCP Use-After-Free Vulnerability in Linux KernelImplications for Enterprise Security
Incidents like these emphasize that enterprise Linux servers remain prime targets for sophisticated state-sponsored threat actors. The integration of AI-generated components into attack toolchains represents a growing challenge for defensive security operations worldwide.
Source: The Hacker News