Critical Linux kernel vulnerability CVE-2026-98432 allows root access
Anthropic researchers found a critical CVE-2026-98432 Linux kernel flaw. Learn how to secure your servers against remote root execution exploits.
·2 min read
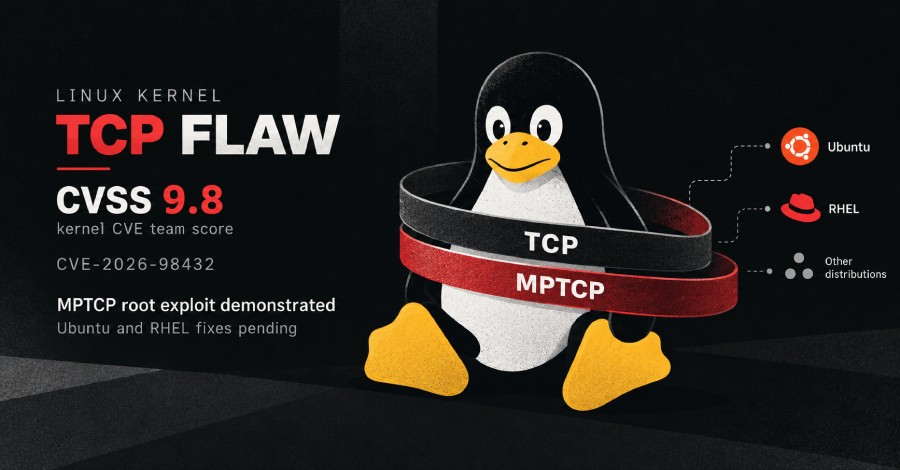
Security researchers at Anthropic have discovered a critical vulnerability in the Linux kernel, tracked as CVE-2026-98432, which allows unauthenticated attackers to execute commands as root remotely. The flaw primarily affects systems utilizing Multipath TCP (MPTCP) listeners.
- Severity score of 9.8 out of 10.
- Affects Linux kernels dating back to version 4.4.
- Exploitation creates a use-after-free condition in IPv4 TCP code.
- AI-driven exploit generation reduced attack development time significantly.
The Technical Vulnerability The issue stems from a race condition in how the kernel handles TCP connection requests. Specifically, the 'tcp_v4_syn_recv_sock' function incorrectly transfers ownership of socket options, leading to a use-after-free state. While Red Hat initially classified this primarily as a potential Denial-of-Service, Anthropic demonstrated that it could be weaponized to bypass KASLR and execute arbitrary code as root in under an hour.
Broader Impact and Go Language A significant concern is the automated enablement of MPTCP in newer software stacks, such as Go 1.24, which enables this feature by default on Linux. This means many developers may be unknowingly exposing their services to this vulnerability, as it can be triggered even without direct authentication through complex packet manipulation.
Mitigation and Remediation Administrators must check their specific distribution advisories, as fixes are being backported to stable kernels. For environments where patching is delayed, network-level restrictions, such as blocking IPv4 TCP packets with suspicious IP options using nftables, are highly recommended. Disabling MPTCP is suggested, though it may not fully mitigate the risk if the underlying TCP stack is reachable.
The New Era of AI-Assisted Exploits This incident highlights a shift in cybersecurity: AI is being used not just for defense, but to drastically shorten the time required for threat actors to develop reliable exploits. For businesses running Linux, the window between vulnerability disclosure and automated exploitation has shrunk, making rapid patching cycles and proactive vulnerability management critical business requirements.
Source: BleepingComputer