Microsoft Teams Attackers Pose as IT Support to Steal Data
Attackers are impersonating IT support on Microsoft Teams to trick employees, abuse AD CS, and steal privileged company data.
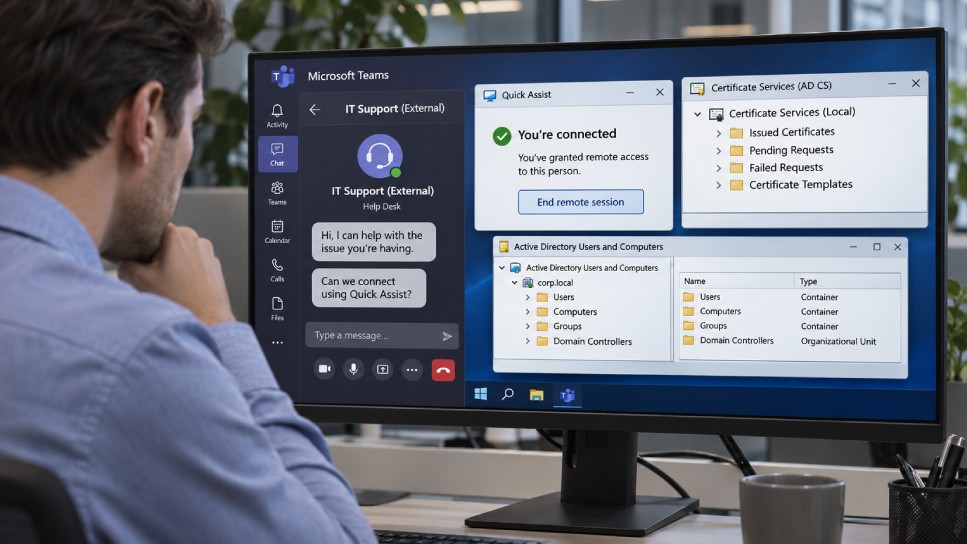
Microsoft has issued a warning regarding a sophisticated campaign where attackers pose as IT support staff on Microsoft Teams. By manipulating employees, the threat actors gain remote control over company PCs to infiltrate corporate networks.
- Threat actors impersonate IT support via Microsoft Teams.
- Employees are tricked into granting remote PC access.
- Insecure AD CS settings are exploited to obtain certificates.
- Privileged accounts, including domain controllers, were compromised.
Social Engineering on Microsoft Teams
According to a Microsoft investigation report detailing two intrusions, attackers leveraged Microsoft Teams to deceive employees. By pretending to be internal IT personnel, they successfully talked workers into handing over remote control of their systems.
Once inside the workstation, the actors could execute further malicious steps, targeting critical infrastructure components instead of immediately deploying ransomware or standard malware.
Read alsoSynology warns of C3RB3R ransomware attacks targeting NAS devicesExploiting Active Directory Certificate Services
After establishing a foothold, the attackers abused insecure Active Directory Certificate Services (AD CS) settings. This allowed them to forge or obtain legitimate login certificates for highly privileged user accounts.
The compromised assets notably included a certificate for a domain controller, granting the attackers deep access to the targeted corporate environment and its sensitive databases.
Implications for Enterprise Security
This campaign highlights the persistent danger of social engineering combined with misconfigured enterprise environments. Organizations must rigorously audit their AD CS configurations and reinforce IT support verification protocols to prevent similar breaches.
Source: The Hacker News