Zyxel fixes zero-day exploited in GS1900 switches
Zyxel has patched a zero-day vulnerability in GS1900 network switches that was actively exploited by hackers to compromise nearly 1,000 devices.
·2 min read
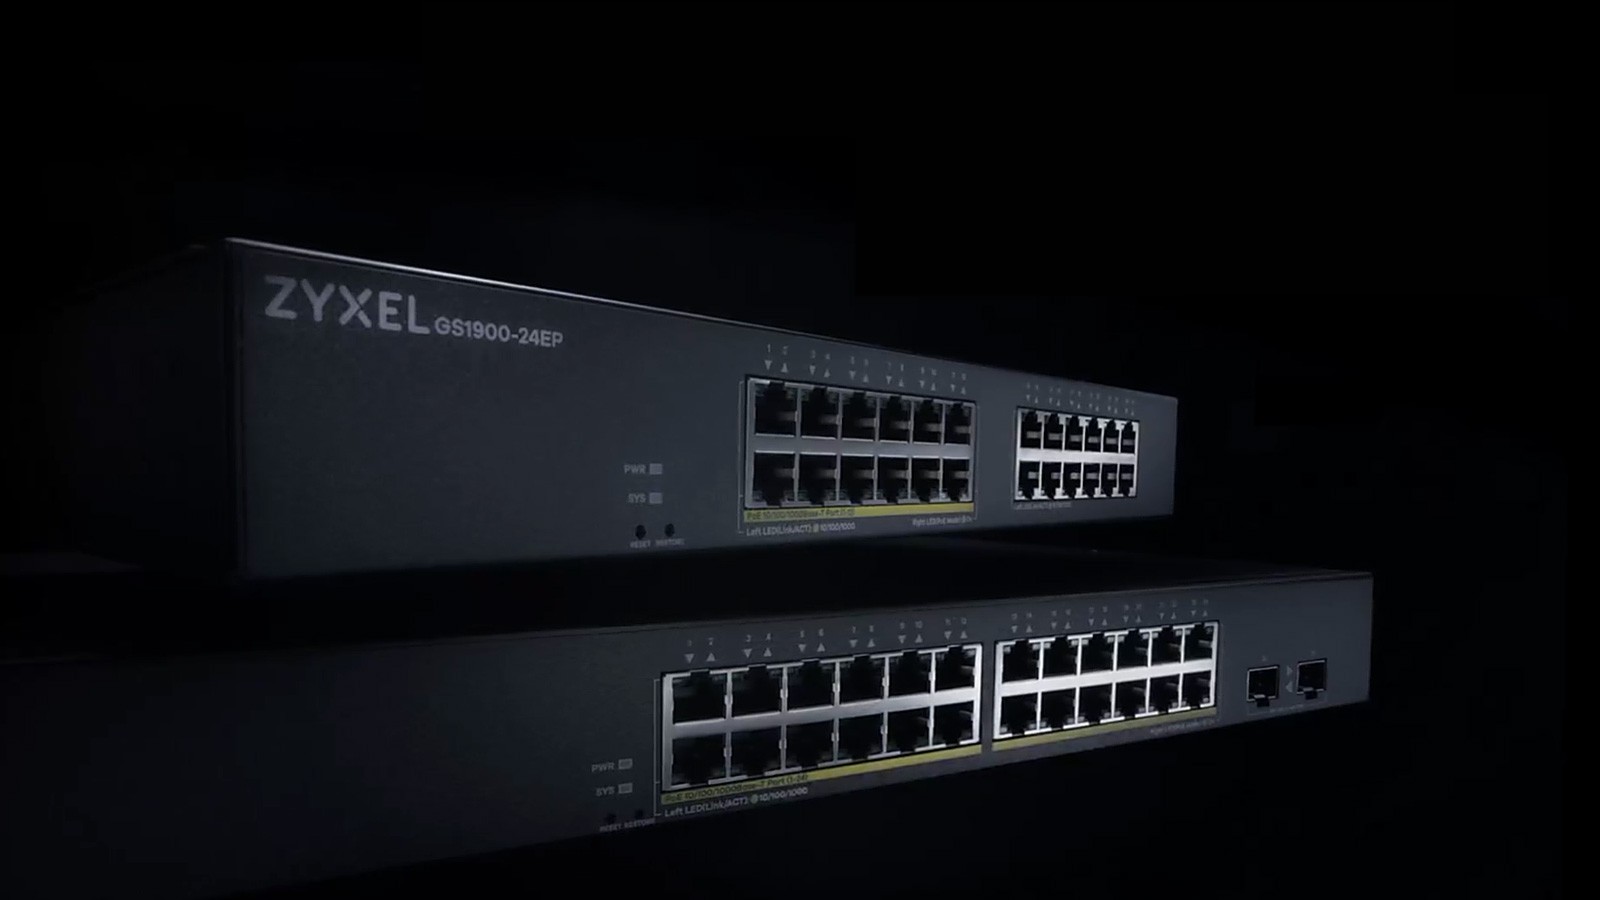
Zyxel has released security updates to patch a zero-day vulnerability affecting its GS1900 series network switches. Attackers actively exploited this flaw to compromise nearly a thousand devices worldwide and steal sensitive configuration files and credentials.
- The vulnerability is tracked as CVE-2026-107441, involving an out-of-bounds write flaw in the web management interface.
- Attackers compromised 996 devices across 48 countries using specially crafted HTTP requests to execute OS commands.
- Initially mistaken for an older flaw, security researchers later uncovered the distinct and unpatched mechanism.
Background and Attack Campaign Details Affecting ten models in the GS1900 switch series, the flaw allows unauthenticated attackers with network access to execute arbitrary operating system commands. According to cybersecurity firm GreyNoise, a suspected Chinese-speaking threat actor named Kapibala began exploiting the switches around August 17. The attackers downloaded scripts to harvest device configurations, hashed root credentials, and network details. Initially, researchers and CISA associated these attacks with CVE-2026-7273, an older pre-authentication buffer overflow flaw patched by Zyxel back in June.
Binarly's Discovery of the Bypass Firmware security researchers at Binarly discovered an exposed archive containing an obfuscated Python exploit targeting Zyxel switches. Analysis revealed that the exploit successfully bypassed firmware updates that were supposed to fix the older vulnerability. By corrupting a parameter counter before validation, the attackers managed to overwrite memory and execute commands without authentication, even on switches running the June security patches.
Vendor Response and Recommendations for Admins Binarly reported the findings to Zyxel in late September, and the vendor officially confirmed the new vulnerability as CVE-2026-107441 on October 11. On October 22, Zyxel released new firmware updates that properly limit parameter sizes and validate parameter counts before memory copying. Administrators managing affected Zyxel GS1900 switches are strongly advised to apply the latest firmware updates immediately to secure their network infrastructure against potential intrusions.
Source: BleepingComputer