
Cyber
Apple details every security fix included in iOS 27 and iPadOS 27
Apple has officially released the complete security breakdown and vulnerability fixes included in the newly launched iOS 27 and iPadOS 27 updates.
Category
Defense, threats, security strategy and auditing.
605 articles
Apple has officially released the complete security breakdown and vulnerability fixes included in the newly launched iOS 27 and iPadOS 27 updates.
Fintech company Revolut has revealed a data breach affecting a number of customers after falling victim to a threat actor impersonating a government agency.
A mass-scanning campaign targeting internet-exposed Vite development servers is attempting to steal cloud credentials from AWS and Azure deployments.
The official HBO Max Reddit account was compromised to push malicious ads executing ClickFix attacks that target Windows and macOS devices.
A browser extension named JeetBot, available in official stores, was found silently exfiltrating Twitch OAuth session tokens to a commercial bot service.
The popular Homebrew package manager has launched version 7.0.0 featuring the native BrewUI graphical interface and a vulnerability scanner.
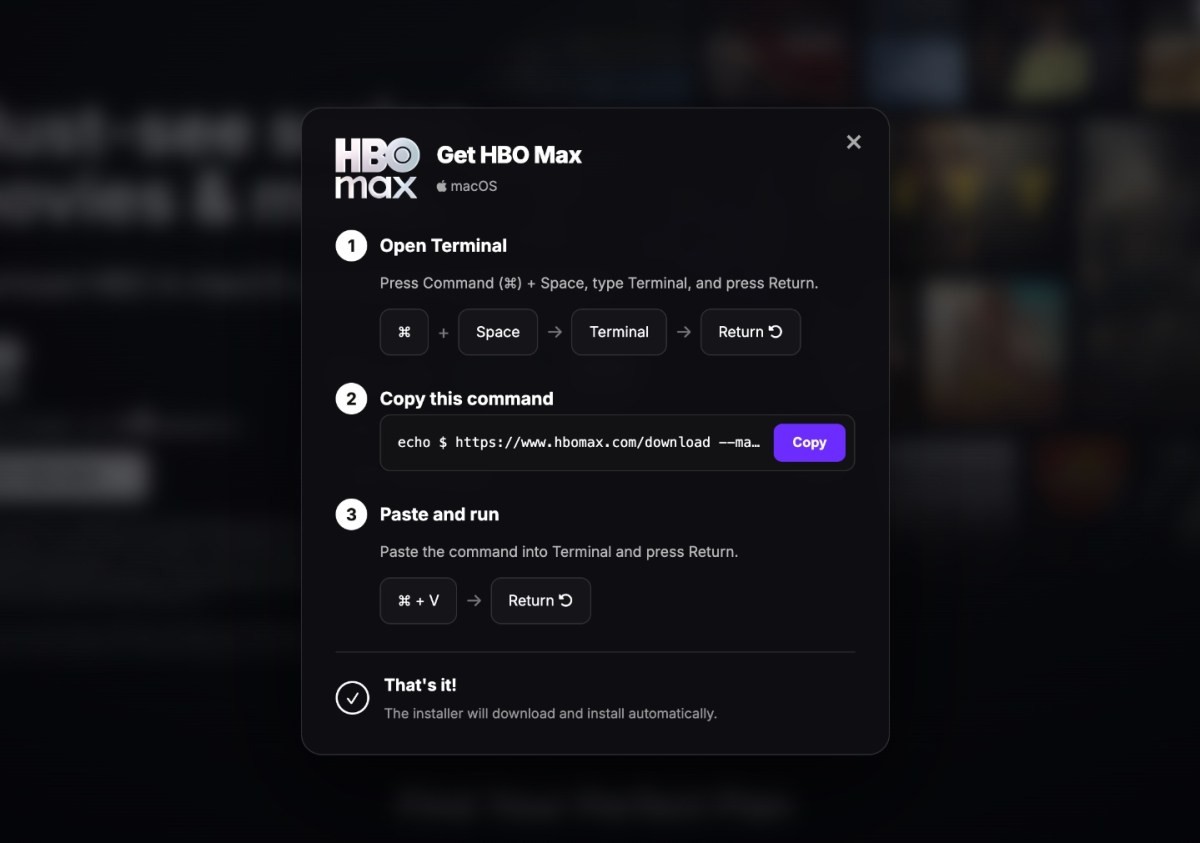
A rising security threat known as ClickFix is deceiving computer users into executing harmful code via fake online advertisements.
A newly discovered Android threat named Mantax Otax combines ransomware and spyware features to compromise mobile devices.
Popular VPN provider Surfshark revealed that hackers accessed one of its internal test servers following a configuration error.
A threat actor leveraged hundreds of AI agents to orchestrate a global exploitation campaign targeting vulnerable PaperCut NG/MF servers.
Cisco Talos reveals that two recently patched Secure Firewall Management Center vulnerabilities have been actively exploited by three threat clusters.
Identity verification company IDScan has confirmed that hackers accessed data stored in its cloud platform following massive leak reports.
Prophet Security breaks down the main attack patterns targeting user identity between May and July 2026.
Multiple cyber-espionage groups deployed an exploit kit dubbed BlueMoon that leveraged zero-day vulnerabilities in Microsoft Windows and Google Chrome.
IDScan has confirmed a major data breach involving the theft of over 150 million driver's licenses and other government-issued identity documents.
Trezor has alerted its customers that threat actors who breached its third-party email provider are targeting them with phishing campaigns.
Healthcare company AdaptHealth has confirmed that the data of 4.1 million people was exposed during a July cyberattack attributed to ShinyHunters.
Cisco has confirmed that a maximum-severity authentication bypass vulnerability in its Secure FMC software is being actively leveraged in attacks.
Healthcare technology company Veradigm disclosed a data breach affecting patient personal information following a cybersecurity incident at a third-party vendor.
While MFA makes account takeover harder, attackers are increasingly targeting password resets and recovery processes.
An anonymous security researcher known as Nightmare Eclipse has released a new Microsoft Defender zero-day exploit named ShieldCrash following the September 2026 Patch Tuesday updates.
Last month, a Claude user noticed his account was consuming tokens even though he wasn't working. Anthropic has since issued a security warning to users.
A sophisticated Linux rootkit targeting F5 BIG-IP APM environments can intercept PHP file loading and inject fileless web shells directly into memory.
The EU Cyber Resilience Act vulnerability reporting requirements take effect, giving software vendors as little as 24 hours to report active flaws.