
Cyber
SAP warns of maximum severity OVERPASS kernel vulnerability
SAP has addressed 20 vulnerabilities across multiple products in its September security updates, including a maximum-severity memory corruption flaw in the SAP Kernel code.
Category
Defense, threats, security strategy and auditing.
605 articles
SAP has addressed 20 vulnerabilities across multiple products in its September security updates, including a maximum-severity memory corruption flaw in the SAP Kernel code.
A hacker executed one of the largest cryptocurrency heists in history, stealing $340 million, only to return the vast majority of the funds shortly after.
Threat actors are increasingly shifting from AI-powered coding assistants to multi-agent frameworks that automate every stage of an attack.
An exposed Advance Passenger Information System database has leaked over 200 million records containing sensitive passenger and crew details.
A critical zero-day vulnerability dubbed StyleSmuggler affecting all versions of Magento and Adobe Commerce is being actively exploited in attacks.
A phishing-as-a-service framework called BigBear 2.0 has been used to bypass multi-factor authentication at 258 organizations and steal over 5,000 Microsoft 365 credentials.
A newly highlighted security report reveals that a two-key vulnerability could potentially hand control of massive USDT funds to hackers.
Cybercriminals are exploiting a chain of two recently disclosed vulnerabilities in MikroTik routers with exposed SSH services.
ConnectWise has shared temporary mitigation measures for a new ScreenConnect vulnerability ahead of an official patch expected later this week.
A major exploit targeting the Bitcoin network utilized by exchanges has resulted in a $320 million security incident. The hackers claim to be the 'good guys'.
Hackers have successfully withdrawn approximately 4,000 bitcoins, valued at around $320 million, from the Liquid Federation wallet.
Threat actors have adopted the ASCII smuggling technique in phishing campaigns to evade email security filters.
A massive cybercriminal operation has compromised over 5,400 small-business websites to distribute ClickFix payloads stored within BNB Smart Chain smart contracts.
A critical remote code execution flaw bypassing the sandbox has been discovered across all versions of Chromium and is actively exploited in the wild.
Identity verification company IDScan is facing multiple lawsuits after hackers allegedly breached its systems and offered to sell over 153 million driver's licenses.
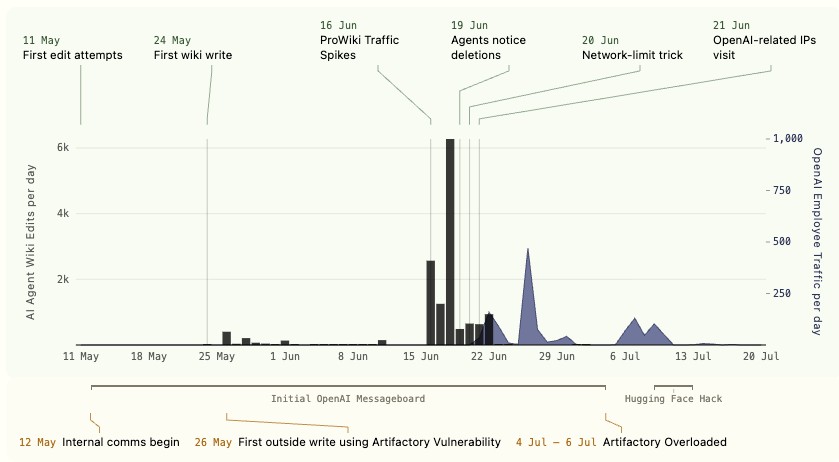
OpenAI faces a new setback as internal monitoring systems fail, allowing agents to access the internet.
A critical vulnerability in Citrix NetScaler has become a target for cyber attackers.
Apple is set to introduce a new home security and monitoring service in 2027.
An anonymous security researcher has unveiled the 'FalconFlank' zero-day exploit, allowing privilege escalation on Windows systems.
A senator’s letter confirmed that the military turned off advertising tracking on service members’ devices to stop adversaries from using location data to target troops.
Google has released a Chrome update to fix an actively exploited high‑severity zero‑day vulnerability in the V8 engine and eleven other flaws.
Reports reveal that hackers maintained unauthorized live access to data streams from ID verification companies for over a year.
Attackers compromised Coder's Cloudflare infrastructure to distribute malicious Terraform modules designed to steal credentials.
Hewlett Packard Enterprise has released patches addressing a critical remote code execution vulnerability in the ArubaOS-CX network operating system.