ARTEX: Chinese Hackers Target 200 Organizations with AI Framework
Chinese state-sponsored threat group Vapor Panda uses an AI-powered penetration testing framework called ARTEX to target over 200 organizations worldwide.
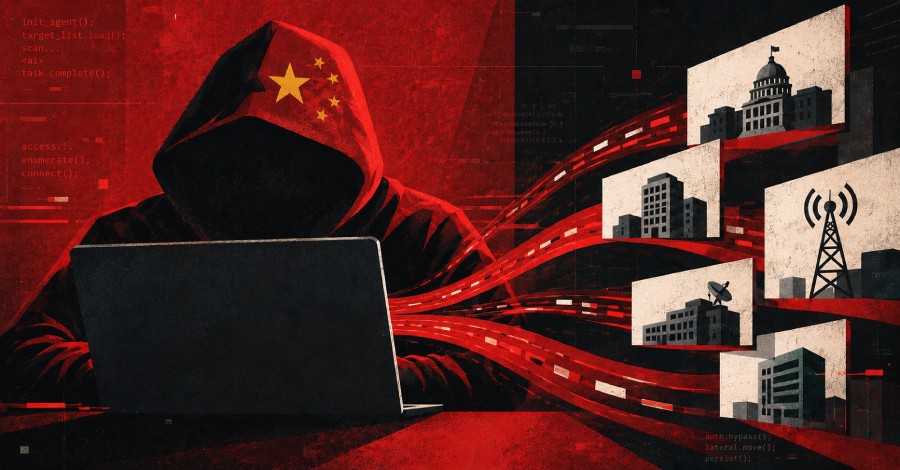
Chinese state-sponsored threat actors have been observed utilizing a Go-based artificial intelligence penetration testing framework named ARTEX. This tool is designed to target high-value organizations simultaneously on a global scale.
- ARTEX is an AI-powered penetration testing framework built in Go.
- More than 200 organizations worldwide have been targeted.
- The activity is attributed to the threat group Vapor Panda.
The Rise of Vapor Panda and ARTEX
The malicious activity was uncovered and attributed by CrowdStrike to a China-based targeted intrusion adversary tracked as Vapor Panda, formerly known as VexatiousTemper. The integration of AI into exploitation frameworks highlights a growing trend in automated cyberattacks.
Implications for Global Cybersecurity
The adoption of artificial intelligence in threat actor toolsets demonstrates how attacks are becoming faster and more sophisticated. Organizations must continuously update their defense strategies to counter these advanced automated frameworks.
Source: The Hacker News