ChatGPT Lockdown Mode vulnerability allows unauthorized chat access
Cybersecurity researchers discovered a flaw in OpenAI's ChatGPT that allowed attackers to bypass Lockdown Mode and exfiltrate chat data without user interaction.
Cybersecurity researchers have identified and disclosed a now-patched vulnerability in OpenAI's ChatGPT that bypassed the platform's Lockdown Mode. Introduced in June 2026, the Lockdown Mode was designed to minimize the risk of data exfiltration caused by prompt injections.
- The flaw enabled silent exfiltration of chat session data.
- Attacks could be executed without requiring user interaction.
- Vulnerability allowed bypassing the intended security restrictions.
- OpenAI has since deployed a patch to mitigate the issue.
Understanding the Vulnerability
The Lockdown Mode was intended to serve as an optional safety barrier against malicious prompt manipulation. However, the discovered exploit revealed that the security implementation had architectural weaknesses, allowing attackers to bypass these protections and access private chat histories silently.
The nature of the attack was particularly concerning because it required no input or permission from the user. By gaining access to previous conversation contexts, attackers could potentially orchestrate more sophisticated phishing attempts or data harvesting campaigns.
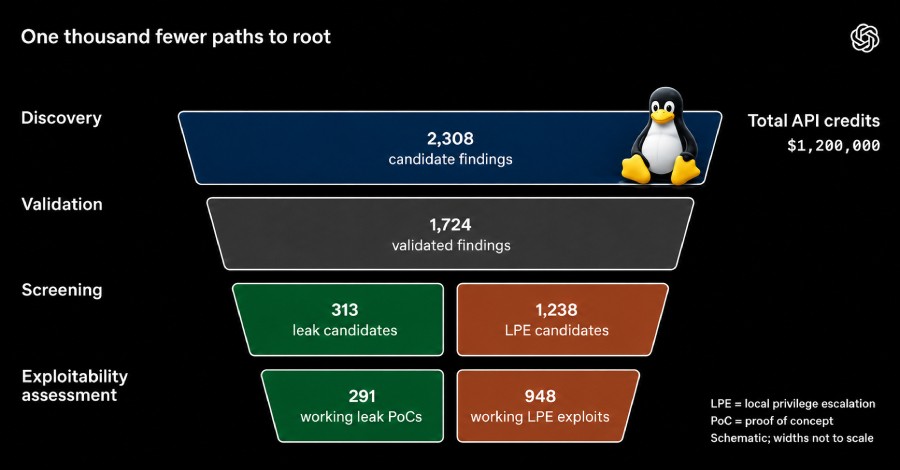
Read alsoOpenAI AI agents discover 948 privilege escalation flaws in LinuxMitigation and Security Response
OpenAI addressed the findings promptly by rolling out a security update that patches the vulnerability. The platform is now considered secure against this specific exploit, and no further action is required from end-users beyond maintaining standard platform usage.
This incident highlights the ongoing challenges of securing large language models. Even with dedicated security modes, the evolving nature of AI exploits necessitates continuous vigilance and rapid response cycles from service providers.
Impact and Takeaways
For developers and enterprise users, this incident emphasizes that no security layer is impenetrable. It serves as a reminder to practice data minimization when interacting with AI systems and to keep all AI-related software and browser integrations updated to the latest secure versions.
Source: The Hacker News