OpenAI AI Pipeline Generates 948 Linux Root Escalation Exploits
OpenAI detailed an AI pipeline that successfully validated and created exploits for 948 Linux privilege escalation vulnerabilities in a 30-hour run.
·1 min read
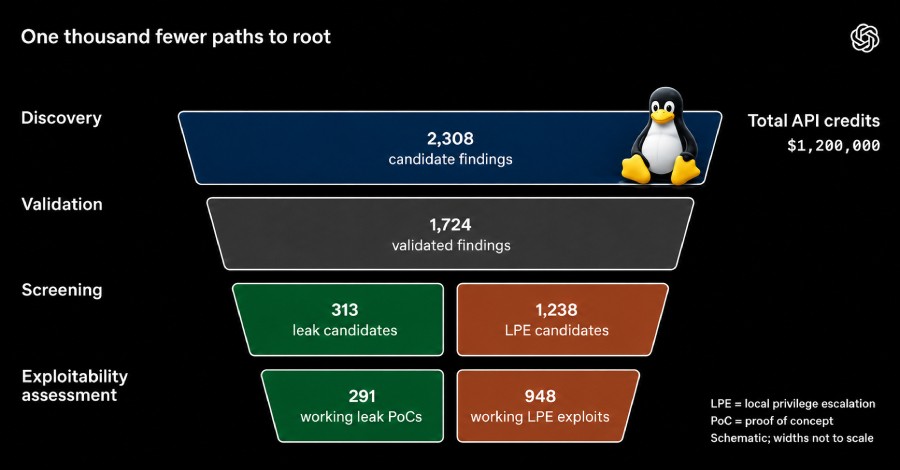
OpenAI has revealed details about a specialized cyber-focused AI model designed to enhance software security. The pipeline successfully analyzed, validated, and generated exploits for nearly a thousand vulnerabilities within the Linux kernel.
- 2,308 candidate Linux kernel findings were analyzed.
- 1,724 vulnerabilities were dynamically reproduced.
- 948 local privilege escalation (LPE) exploits were generated.
- The total API cost reached $1.2 million for the 30-hour process.
Analyzing the Pipeline The prototype focused on automating the identification and validation of LPE vulnerabilities. By dynamically reproducing these threats, the model proves that AI can significantly streamline the patching process, moving far beyond simple static analysis.
Costs and Scale Running the pipeline for 30 hours incurred $1.2 million in API expenses, showcasing the massive computational demands required for such deep security research. This reflects both the power of modern LLMs and the cost associated with large-scale automated vulnerability testing.
Impact on Cybersecurity For the global tech industry, this development suggests that automated security auditing will soon become the standard. By reducing the time-to-patch for critical kernel vulnerabilities, this technology could fundamentally improve the stability and security of global cloud infrastructure.
Source: The Hacker News