Claude Code exposes developer passwords and keys on public GitHub
A security flaw in Anthropic's Claude Code exposed passwords and API keys across 1,122 public GitHub repositories.
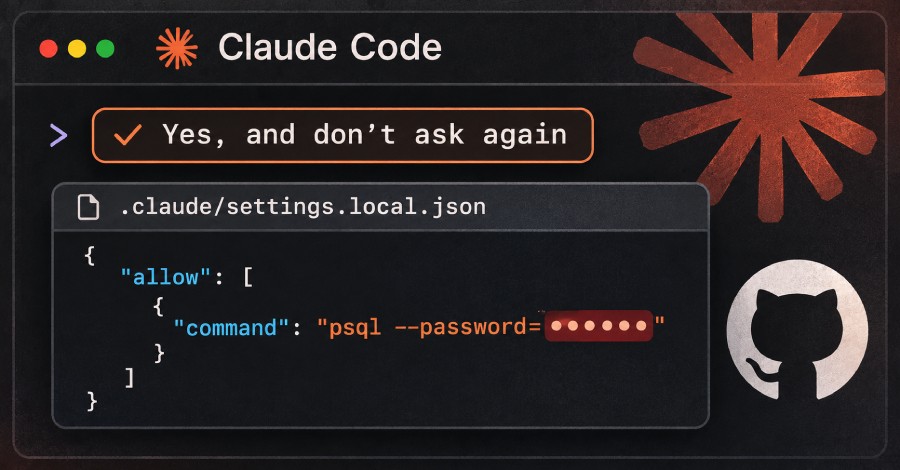
Software security company Apiiro has revealed that passwords and API keys entered by developers into Claude Code are currently exposed in public GitHub repositories.
- Don't Ask Again feature saves commands word-for-word
- 1,122 public copies contain sensitive secrets
- Developers' API keys and passwords are readable by anyone
How the Flaw Occurs
When users select the 'Yes, and don't ask again' option to approve commands in Anthropic's AI coding assistant, the tool saves the command verbatim, including any embedded secrets, directly into a project settings file.
Scale of the Exposure
Read alsoAnthropic updates Claude to stop blocking game development projectsAccording to Apiiro, exactly 1,122 public repository copies on GitHub currently contain these sensitive project settings files. This leaves the exposed credentials open for anyone to read and exploit.
What This Means for Developers
Developers using automated AI tools must carefully audit their repository settings and configuration files. Immediate action such as revoking leaked API keys and updating passwords is vital to secure projects against potential breaches.
Source: The Hacker News