Claude Dispatch vulnerability allows malicious extensions to run local code
Forever Security researchers warn that malicious browser extensions could exploit Claude Dispatch to execute arbitrary code on user machines.
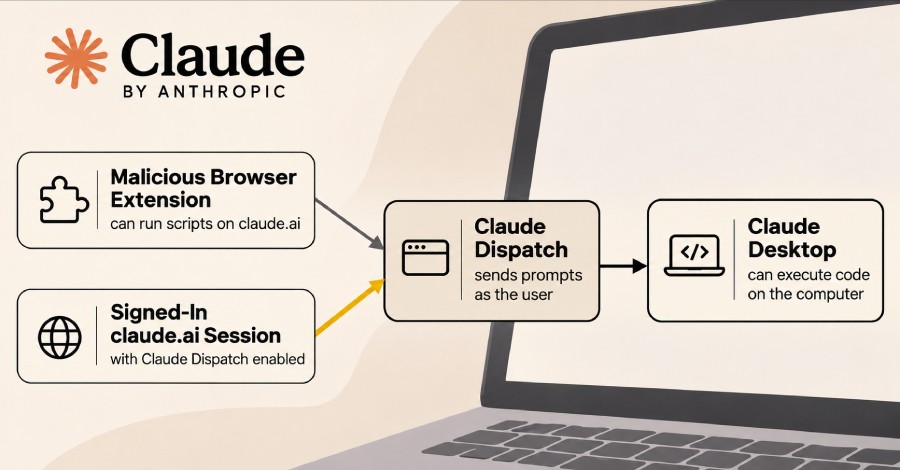
Researchers at the endpoint security company Forever Security have uncovered a concerning security flaw involving the Claude Dispatch feature. A malicious browser extension, capable of executing scripts on claude.ai, could potentially trick the Claude Desktop application into running malicious code directly on the user's computer.
Key takeaways: - The attack leverages the synchronization mechanism of the Claude Dispatch feature. - Malicious browser extensions can manipulate Claude's interaction with the desktop client. - The security researchers confirmed that the flaw can still be exploited by attackers.
Vulnerability Mechanics The Claude Dispatch feature was designed to provide a seamless experience by allowing users to send tasks from their mobile devices to the Claude Desktop application. However, the lack of strict authentication or origin validation for these tasks allows a malicious extension to inject instructions that the desktop client interprets as legitimate commands from the user.
Risks to Endpoint Security This vulnerability poses a significant risk to the integrity of the user's local machine. Since the Claude Desktop application often requires certain permissions to interact with the system, an attacker could abuse these privileges to perform unauthorized actions, ranging from data exfiltration to executing malicious system commands.
Impact and Mitigation For developers and business users, this highlights the risks inherent in browser-based AI integration. Users should be cautious when installing browser extensions, even if they appear benign. Always audit the permissions granted to third-party extensions and consider limiting the scope of access they have to sensitive websites like claude.ai to mitigate the risk of such supply chain-style attacks.
Source: The Hacker News