Langflow 1.13.0 Released to Fix Critical RCE and Auth Bypass Flaws
IBM reports critical flaws in Langflow versions 1.0.0 through 1.12.8 allowing unauthenticated code execution. Update to 1.13.0 immediately.
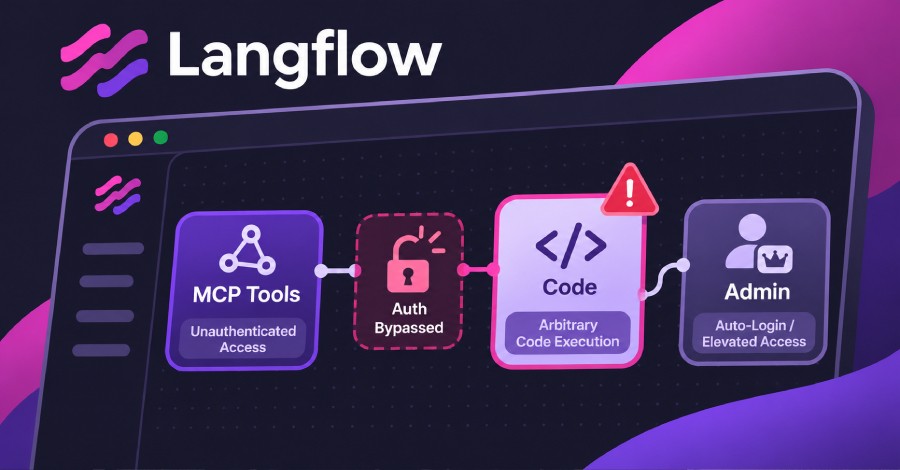
IBM announced last week that two critical vulnerabilities were discovered in Langflow, which could allow a remote attacker without an account to bypass authentication or execute arbitrary code on affected servers.
- Every release from version 1.0.0 through 1.12.8 is affected by these critical flaws
- The vulnerability allows unauthenticated attackers to run arbitrary code remotely
- Version 1.13.0 is currently the only official fix released to address the issue
- Langflow is a widely used open-source tool for building AI agents and workflows
Details of the Langflow Security Flaws
Langflow is an open-source tool designed for building AI agents and workflows, with vulnerability reports managed through IBM. According to recent disclosures, the security defects impact all software releases ranging from version 1.0.0 up to version 1.12.8.
These critical gaps expose servers to remote attacks where malicious actors can bypass security checks without needing user credentials. Although neither flaw is currently listed in CISA's Known Exploited Vulnerabilities catalog, the severity requires immediate attention from system administrators.
Read alsoAlpine Linux rebuilds GitLab infrastructure after RCE attackMitigation and Recommended Action
Developers and organizations utilizing Langflow must upgrade their instances to version 1.13.0 immediately. Updating is currently the only known fix to secure systems against potential remote code execution and unauthorized access attempts.
Source: The Hacker News