NetamLoader Malware Targets Government Windows 10 Systems in Asia
Kaspersky details a sophisticated infection chain using a new .NET framework called NetamLoader to target government Windows 10 builds in Asia.
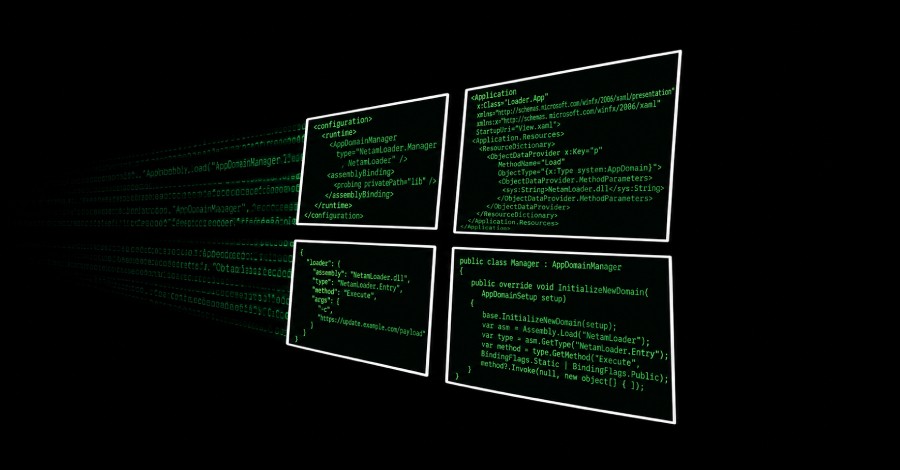
Cybersecurity researchers have uncovered a highly sophisticated infection chain targeting government organizations in Asia. The campaign highlights advanced tactics utilized against specific critical infrastructure targets.
- Targets a custom Windows 10 build used exclusively by government entities
- Deploys a previously undocumented .NET assembly-loading framework
- Employs advanced .NET injection techniques for stealth
Details of the NetamLoader Campaign
According to disclosures from Kaspersky, the malicious activity focuses on specialized government operating system builds in the Asian region. The attackers leverage a novel framework designed to load .NET assemblies covertly.
The newly discovered framework, designated as NetamLoader, had not been documented in previous threat intelligence reports. This indicates the use of bespoke tooling tailored for targeted espionage operations.
Read alsoVOLTA infostealer uses LLMs to rank victims by asset valueImplications for Cybersecurity
Such sophisticated campaigns underscore the persistent threats facing government networks globally. Security teams must remain vigilant and continuously adapt their defenses against undocumented custom loaders and injection methods.
Source: The Hacker News