Debian and Ubuntu APT Flaw Allows MitM Attackers to Run Code as Root
A vulnerability in APT for Debian and Ubuntu lets MitM attackers swap verified packages and execute arbitrary code with root privileges.
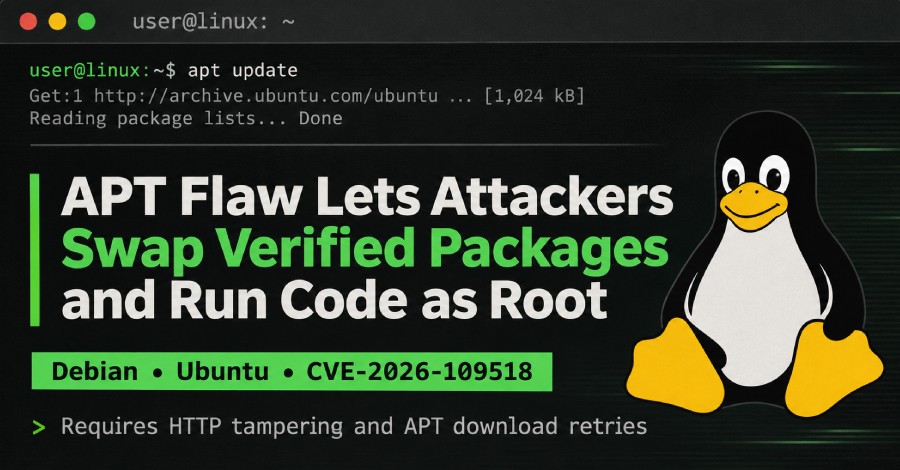
According to advisories published on November 4 by Debian, Ubuntu, and APT developers, a significant vulnerability affects the APT package manager. The flaw allows an attacker capable of modifying package downloads to substitute a checked package with a malicious one.
- The flaw impacts the APT package manager across Debian and Ubuntu
- The exploit requires the ability to intercept and modify downloads (MitM)
- The attack relies on APT retrying failed package downloads
- Arbitrary attacker code executes with full root privileges
Vulnerability Details and Attack Vector
The security advisory details that the attack mechanism depends on APT's default behavior of retrying failed downloads. This behavior has been enabled by default starting from Debian 12, making modern deployments susceptible to the exploit.
An attacker positioned to perform a Man-in-the-Middle (MitM) attack can interfere with the initial download, cause it to fail, and manipulate APT into retrying the download while substituting the official package with a malicious counterpart.
Read alsoRed Hat Patches Critical Linux TCP Vulnerability as Ubuntu Tests FixesImpact on System Security
Because package managers operate with elevated system privileges, successfully replacing a verified package results in the attacker's code executing as root. This grants the adversary complete control over the affected host operating system.
What This Means for Users and Administrators
System administrators and users managing Debian or Ubuntu environments should immediately apply the official APT updates provided by the respective distributions to mitigate potential exploitation risks.
Source: The Hacker News