Red Hat Patches Critical Linux TCP Vulnerability as Ubuntu Tests Fixes
Red Hat has released fixes for a critical Linux kernel TCP flaw, while Ubuntu keeps its updates in the opt-in testing channel.
·1 min read
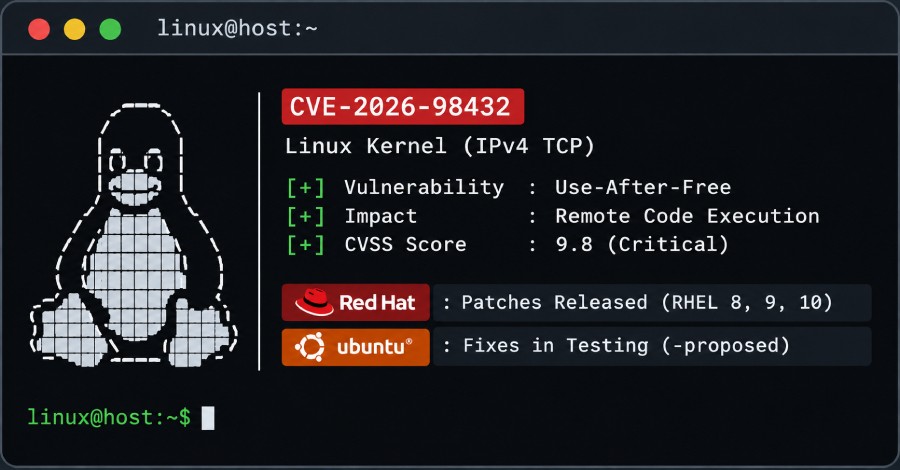
Red Hat has made fixed kernels available for Red Hat Enterprise Linux versions 8, 9, and 10 to address a serious security flaw in the Linux kernel.
The vulnerability involves a use-after-free issue within the kernel's IPv4 TCP code that can be exploited remotely.
- The flaw is tracked as CVE-2026-98432
- It affects the Linux kernel's IPv4 TCP code implementation
- Exploitation can be achieved by a remote, unauthenticated attacker
- Fixes are currently ready for Red Hat Enterprise Linux users
Details of CVE-2026-98432 The vulnerability represents a significant risk to server infrastructure because it allows remote threat actors to interact with the flaw without requiring any prior system authentication. The use-after-free condition in the network stack poses severe stability and security concerns.
Mitigation Status Across Distributions While Red Hat has moved quickly to push stable updates to supported enterprise releases, Canonical's Ubuntu has taken a more cautious approach. Fixes for its three newest long-term support releases remain confined to the opt-in testing channel with no set release date.
Impact on IT Professionals and Infrastructure Administrators managing Red Hat environments should apply the patches immediately to secure their networks against potential remote exploits. Ubuntu administrators must monitor the testing channels and await the official stable rollout.
Source: The Hacker News