Ruby on Rails Flaw Allows Arbitrary File Upload via ImageMagick
A critical vulnerability in Ruby on Rails allows attackers to write arbitrary files on servers using ImageMagick. Patches are available.
·1 min read
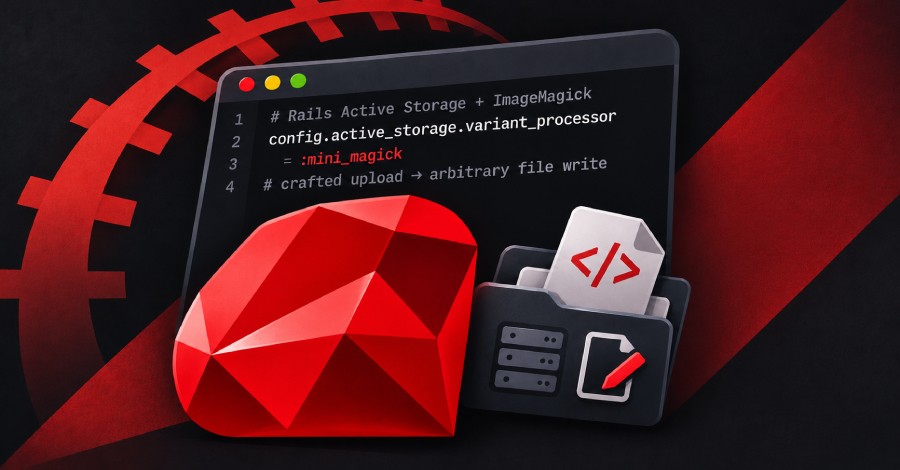
A critical security flaw has been disclosed in the Ruby on Rails web framework that could allow an unauthenticated attacker to write arbitrary files on an application's server. The issue is triggered by uploading a specially crafted file.
Key facts about the vulnerability: - The flaw resides in Active Storage, the file upload component of Rails. - It affects applications that process uploaded files using ImageMagick. - Attackers can exploit this by uploading a crafted file to the server. - The Rails team has patched the issue in versions 8.1.4.1 and 8.0.5.2.
Understanding the Active Storage Flaw The vulnerability impacts Active Storage, which is responsible for handling file attachments and uploads in Ruby on Rails applications. If an app relies on ImageMagick to process these uploads, it becomes susceptible to the flaw. By leveraging a maliciously crafted file, an attacker could potentially bypass security controls and write arbitrary files to the server's filesystem, posing significant security risks.
Mitigation and Developer Recommendations The Ruby on Rails project has officially disclosed the advisory and released immediate patches to address the issue. The security updates are available in versions 8.1.4.1 and 8.0.5.2. Developers are strongly advised to update their Rails applications immediately, especially if they use ImageMagick for file processing, to prevent potential server compromise.
Source: The Hacker News