Control Web Panel: Hackers Hide Linux Backdoor in Web Server
Researchers found a backdoor hidden in the Control Web Panel web server that executes commands without leaving logs.
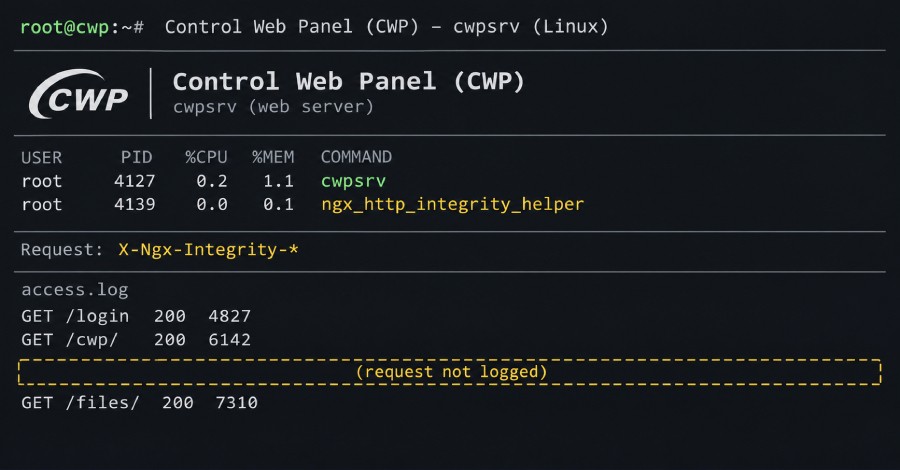
Researchers at QiAnXin's XLab have discovered a covert backdoor hidden within the web server that powers Control Web Panel (CWP), a popular free Linux hosting management tool.
- The backdoor hides inside the web server running Control Web Panel.
- It executes commands sent via web requests without detection.
- Attack traces never appear in the server's access logs.
- Installation requires prior root access to the target server.
How the Backdoor Operates
According to the security researchers, the malicious component intercepts web requests and translates them into system commands. Because these requests completely bypass the standard access logging mechanism, system administrators cannot spot them through traditional log analysis.
Prerequisite Root Access
Read alsoCWPdoor Linux Malware Targets Control Web Panel ServersAn important aspect of this threat is that installing the backdoor requires root privileges. This indicates that attackers must have already breached the server through a separate initial vector before deploying this stealthy control mechanism.
Implications for Server Security
For IT professionals and businesses managing Linux hosting environments, this discovery highlights the need for comprehensive endpoint security and integrity monitoring. Relying solely on standard web server logs is no longer sufficient to detect sophisticated intrusions, making proactive hardening and privilege management essential.
Source: The Hacker News