cPGuard Update Channel Hijacked to Backdoor Linux Servers
Attackers compromised the cPGuard update channel on November 2, deploying a backdoor to harvest password hashes from Linux servers.
·1 min read
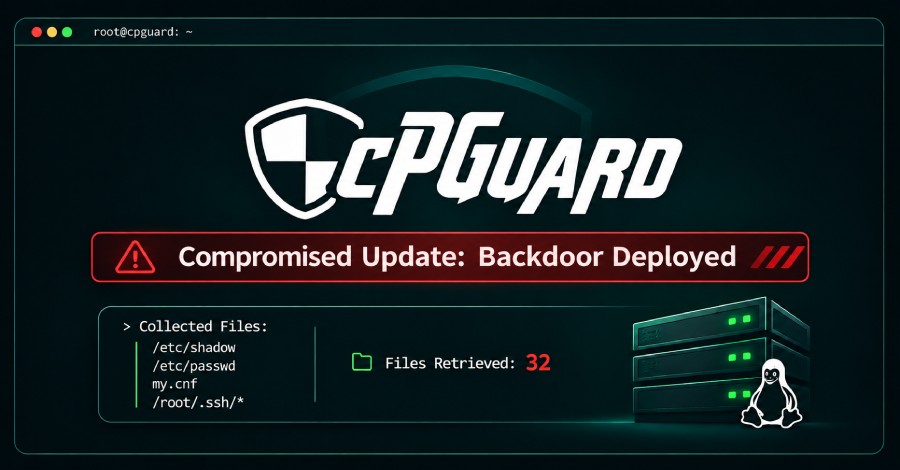
Security tool maker OPSSHIELD has issued an advisory revealing that its cPGuard update system was breached by an attacker on November 2. The breach was exploited to push a malicious script directly to customers running Linux servers.
- The update channel compromise occurred on November 2
- A malicious script installed a backdoor on affected Linux servers
- Attackers harvested password hashes and sensitive files from servers
- The issue impacts cPGuard version 5.88.25 and later releases
Technical Details of the Breach According to OPSSHIELD, the attacker successfully leveraged the compromised update mechanism to distribute unauthorized code. Servers that automatically or manually ran the script during the update cycle executed a hidden backdoor, compromising server integrity. During the execution, the malicious script targeted critical files, specifically collecting password hashes and other sensitive data. The attacker has already managed to exfiltrate a portion of this harvested data from the compromised environments.
Impact and Remediation for Administrators This supply-chain style attack highlights the risks associated with third-party security tooling and automated update channels. Administrators running cPGuard 5.88.25 and newer versions must immediately audit their Linux servers for unauthorized access, rotate credentials, and apply official patches.
Source: The Hacker News