Hackers exploited iOS and Android flaws to target diplomats
Security researchers report that a Kremlin-linked group used patched iOS and Android vulnerabilities to target visitors of high-profile websites.
·2 min read
Hackers possibly linked to the Kremlin exploited previously patched vulnerabilities in iOS and Android to target visitors of multiple high-profile websites. The campaign focused on resources associated with major national events and diplomatic venues in the US and the UK.
According to researchers at security firm Sekoia, the attackers deployed sophisticated web redirection and script injection techniques. The operation aimed to compromise devices of diplomats, government officials, and visitors of trusted websites through targeted spear-phishing preparations.
- Attackers impersonated high-profile sites, including a US Constitution anniversary portal and a luxury hotel in London.
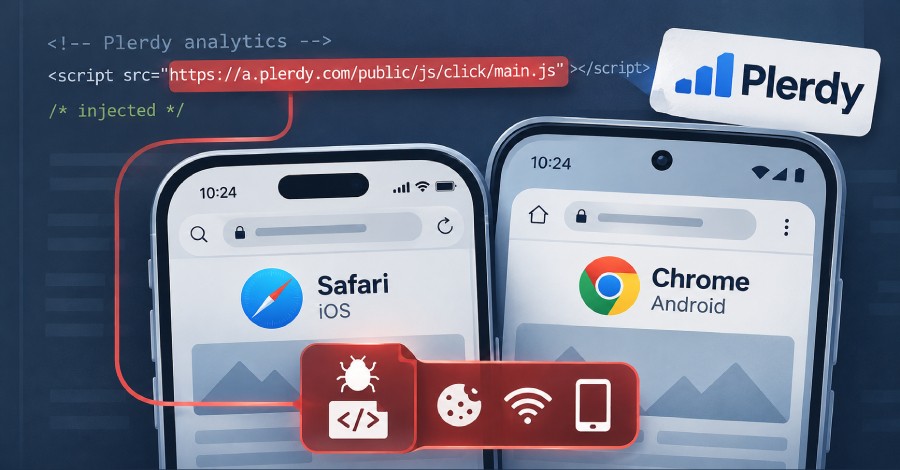
- Three infection vectors were used: direct JavaScript injection, proxy domains, and a Ukrainian web analytics supply chain compromise.
- All exploited vulnerabilities were n-days, meaning they had official patches but only affected outdated software versions.
- Attribution to the Kremlin is based on target profiles and similarities to tactics used by the APT29 threat group.
Fake Web Proxies and Watering Hole Tactics Attackers registered the domain america250.holiday to act as a reverse proxy for america250.org, a website celebrating the 250th anniversary of the US Constitution. The impostor site delivered legitimate content infused with malicious JavaScript. Security analysts note this infrastructure was likely intended to set up spear-phishing pretexts for high-profile targets. A second domain, theowo.club, proxied the Raffles London at The OWO hotel website. The luxury venue is physically close to sensitive UK government sites, including the Ministry of Defence and 10 Downing Street. Open-source data indicates Ukrainian President Volodymyr Zelenskyy stayed at the hotel during a previous visit.
Technical Details and Zero-Click Exploit Chains Malicious code was also distributed via compromised sites, including a major Ukrainian gas producer and a local web analytics service utilized by thousands of websites. In every case, the injected JavaScript performed initial reconnaissance by profiling the victim's browser and device parameters. Using the collected device telemetry, the attackers delivered one of three zero-click exploit chains requiring no user interaction. One of the utilized frameworks was DarkSword, an iOS exploit kit previously linked to a Turkish commercial surveillance vendor and other threat actors.
What This Means for Users and Security This campaign highlights the critical importance of maintaining up-to-date mobile operating systems. Because all vulnerabilities leveraged in the attacks were n-day flaws, the exploits failed on devices running patched software, succeeding only against outdated versions of iOS and Android. For organizations, government entities, and high-profile individuals, the incident underscores the persistent threat of sophisticated mobile spyware. Mitigating such zero-click risks requires strict adherence to system updates and enterprise-grade mobile device management solutions.
Source: Ars Technica - All content