Northflank Suffers Security Breach: AI Keys and Secrets Compromised
Cloud platform Northflank has suffered a security breach, with reports of unauthorized AI API key usage. Rotate all your secrets immediately.
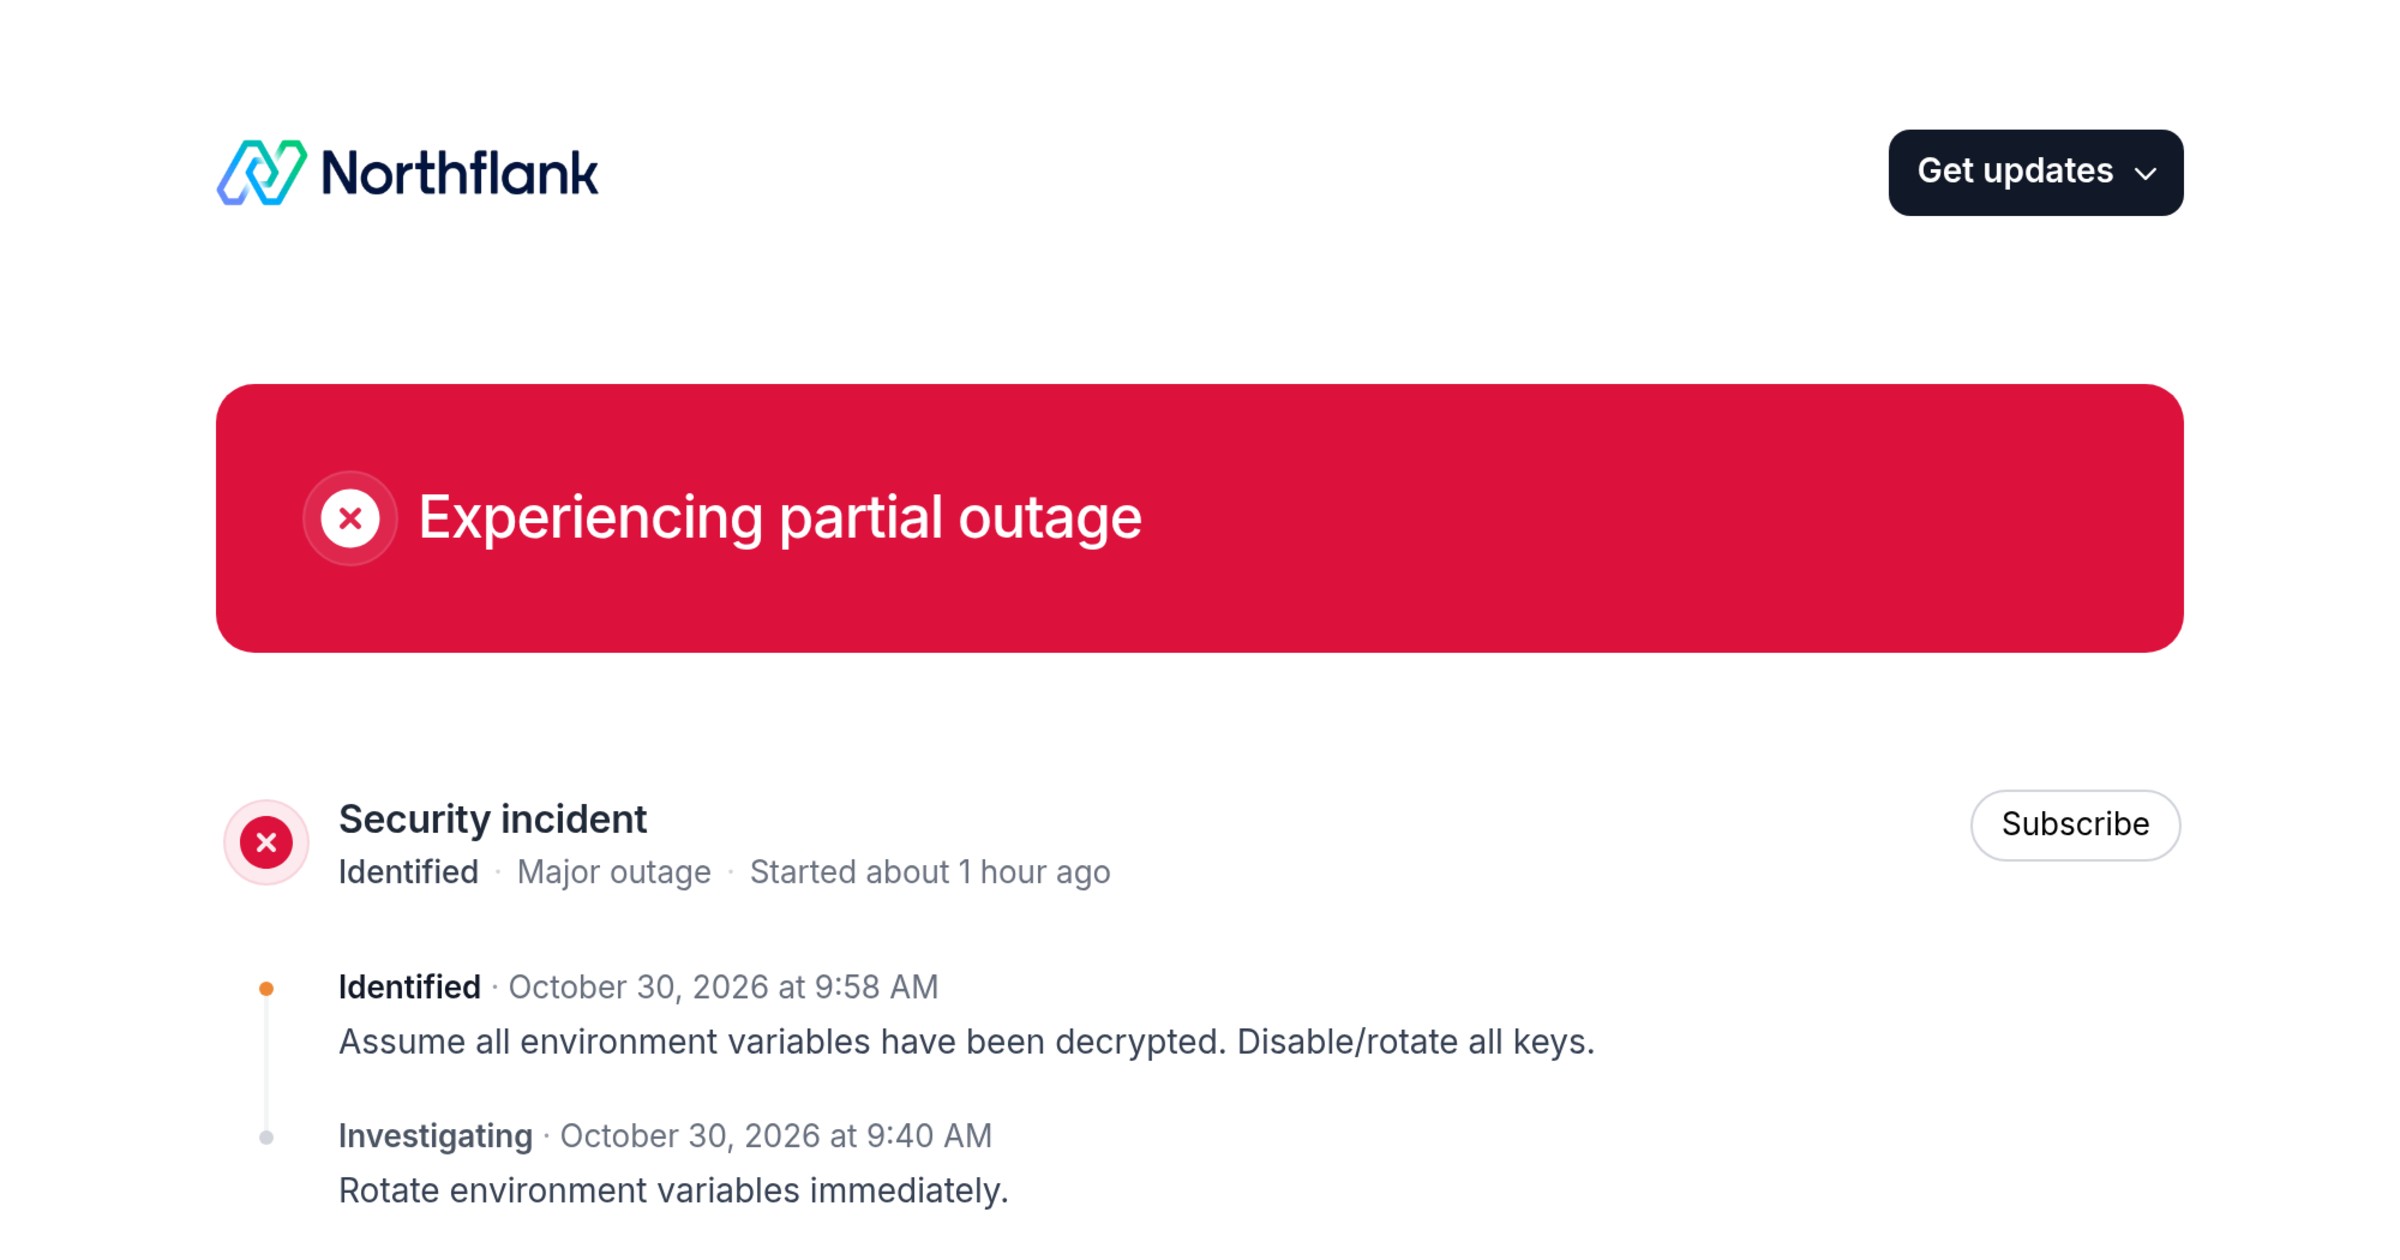
Cloud platform Northflank has confirmed a security incident involving unauthorized access to user-provided data and credentials. The company strongly urges all customers to assume their data has been compromised and take immediate defensive actions.
- Multiple users have confirmed unauthorized usage of AI API keys supplied to the Northflank platform.
- Audit logs have been enabled for all users, including free-tier accounts, alongside automated secret rotation for Postgres and MongoDB.
- The attack patterns and IP addresses involved align with Wiz's "Black October" report targeting AI credentials.
- Investigation is ongoing, with network policy patches and additional fixes already deployed by the technical team.
Overview of the Security Incident
Northflank's platform security was breached, leading to situations where users found their AI service API keys being actively exploited by malicious actors. In response to the unfolding crisis, the engineering team acted swiftly, deploying an initial network policy patch at 12:02 UTC, followed by additional patching at 12:50 UTC.
While the internal investigation remains ongoing, preliminary findings connect this incident to a broader, coordinated campaign targeting artificial intelligence credentials. Similar tactics, techniques, and IP addresses were previously documented in the Wiz security report titled "Black October", highlighting a systemic threat to developer platforms.
Read alsoGitee: 26400 Exposed Cloud and AI Credentials Found in Public ReposMandatory Security Actions for Users
The core directive from Northflank remains absolute: all users must assume that every environment variable, workload secret, secret group, and global secret has been decrypted and compromised. Public access to addons should also be disabled immediately if previously enabled.
Users are instructed to revoke existing credentials directly with their issuing providers, generate secure replacements, and update the affected workloads inside Northflank. Furthermore, individuals must carefully review their AI provider usage and billing logs for any unexpected activity.
Implications for Developers and Businesses
This breach serves as a stark reminder of the underlying risks associated with cloud deployment platforms and centralized secret management. As businesses increasingly integrate powerful AI tools and external APIs into their workflows, securing those credentials becomes critical to preventing unauthorized resource consumption and financial loss.
For software engineers and tech companies globally, this incident emphasizes the necessity of zero-trust architectures, routine credential rotation, and prompt incident response protocols. Proactively disabling exposed endpoints and auditing environment variables remains essential for robust cloud security.
Source: Hacker News: Front Page