TeamViewer Patches Flaw Allowing Host Computers to Attack Viewers
TeamViewer has fixed a security flaw that allowed a remote host machine to crash and potentially attack the computer controlling it.
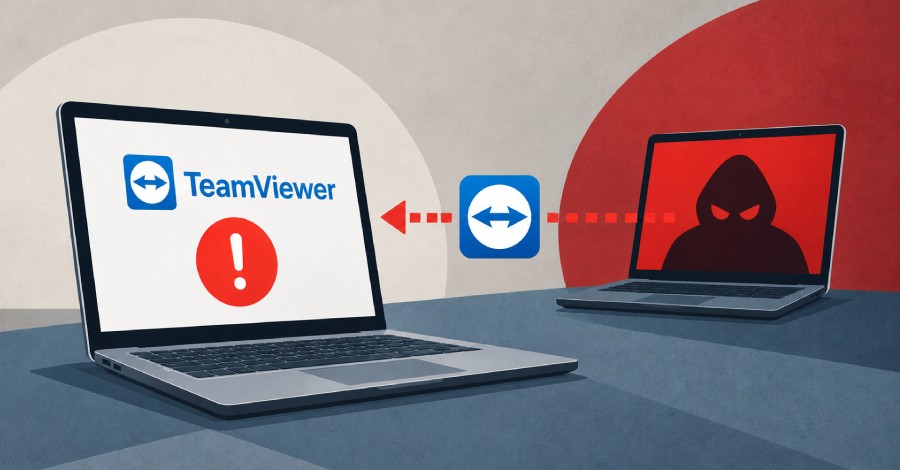
TeamViewer has successfully patched a vulnerability that allowed a remotely controlled machine to launch an attack against the computer connecting to it. In standard remote sessions, the connecting computer acts as the viewer, while the controlled machine acts as the host.
- A compromised or malicious host could exploit the flaw to target the connecting viewer.
- The exploit could crash the TeamViewer application on the viewer's machine.
- Depending on the platform, attackers could potentially run code on the controlling computer.
Understanding the Remote Access Flaw
Typically, remote desktop software assumes that the controlling client is secure and the host is the one being managed. However, this security flaw inverted the trust model, posing unexpected risks to IT support staff and administrators connecting to untrusted endpoints.
By exploiting the vulnerability, a rogue host could retaliate against the connecting machine, disrupting operations and potentially compromising the operator's system integrity depending on the underlying platform architecture.
Read alsoIvanti Connect Secure Flaws Exploited for Root AccessImportance of Immediate Updates
For businesses, IT administrators, and regular users relying on remote access tools, applying the latest security updates from TeamViewer is crucial. This incident highlights the importance of maintaining up-to-date software to defend against unconventional attack vectors.
Source: The Hacker News