
Cyber
New UEFI bootkit BlackX infects fully patched Windows machines
The new BlackX UEFI bootkit successfully bypasses Secure Boot on fully updated Windows PCs. Why standard Microsoft patches were not enough.
Category
Defense, threats, security strategy and auditing.
605 articles
The new BlackX UEFI bootkit successfully bypasses Secure Boot on fully updated Windows PCs. Why standard Microsoft patches were not enough.
Attackers compromised the cPGuard update channel on November 2, deploying a backdoor to harvest password hashes from Linux servers.
Google warns that LLMjacking attacks are hijacking enterprise AI access, running up to $1 million in unauthorized cloud and computing charges.
Cryptocurrency exchange Binance reported that a massive 6.3 billion dollar security breach started with a fake job interview scheme.
Cybersecurity company Barracuda Networks has urged customers to patch two critical vulnerabilities that allow attackers to run commands with root privileges.
Binance founder Changpeng Zhao has warned the crypto industry about a surge in AI-powered cyberattacks following a historic $6.4 billion heist.
Financial authorities in South Korea have asked the country's largest banks to assess potential impacts from a major cryptocurrency hack.
JFrog researchers discovered 42 hijacked GitHub repositories featuring malicious npm publisher loaders for popular AI and development tools.
A cybersecurity coalition and Japanese police neutralized the XCPE botnet infecting 1.3 million Android TV boxes, traced back to Videostrong.
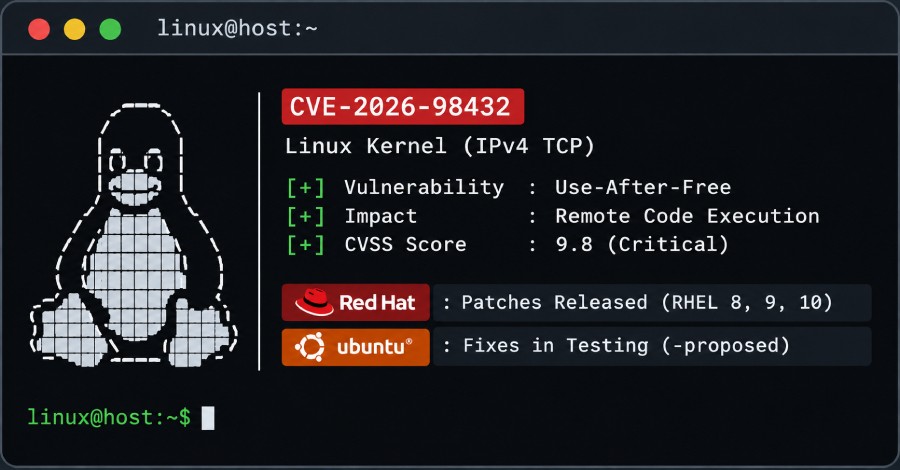
Red Hat has released fixes for a critical Linux kernel TCP flaw, while Ubuntu keeps its updates in the opt-in testing channel.
On November 2, 2026, hosting provider Beget suffered a major cyberattack with wipe scripts. Read about the current recovery status.
Google has expanded its Cloud VRP with a new top-tier $250,000 reward for architectural security flaws and tenant-isolation bypasses.
Liquid's bitcoin IOUs are fully backed again following a massive $320 million exploit. Read more on Tecc.uz about the platform's recovery.
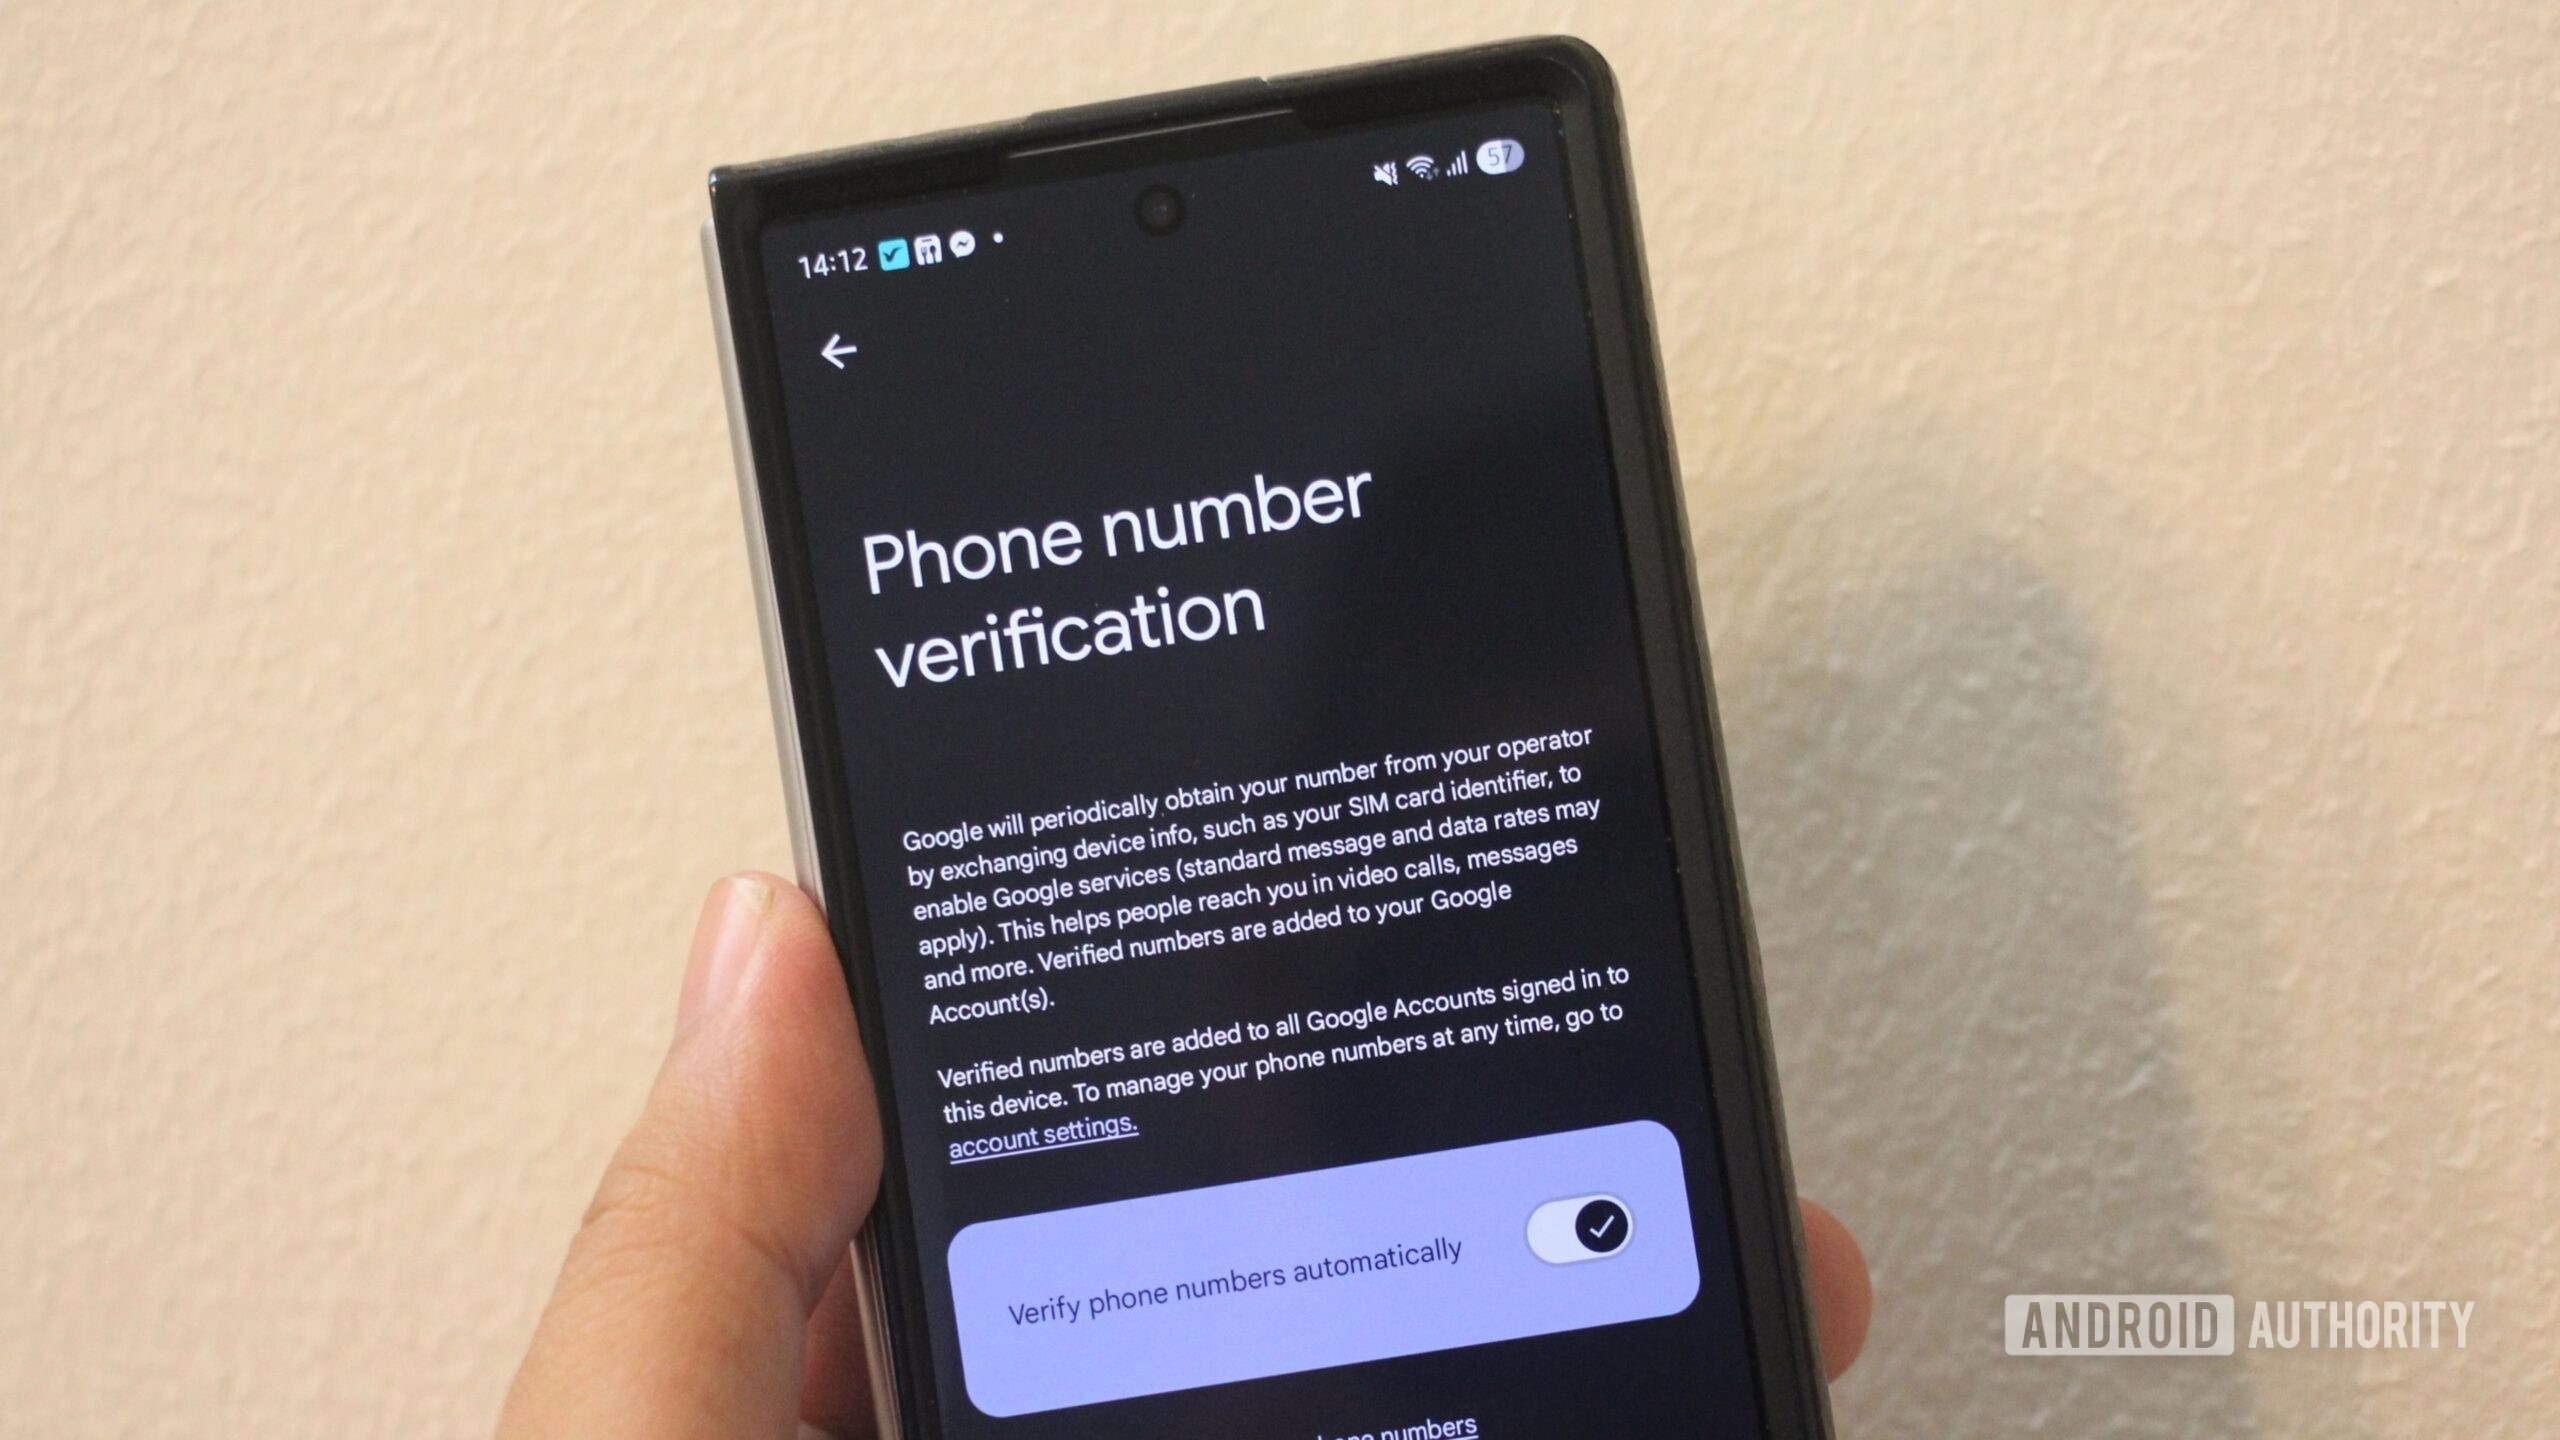
Google automatically links phone numbers across Android accounts. Learn about privacy risks, security threats, and how to turn off the feature.
CrowdStrike has launched the AI Kill Switch feature within the Falcon Guardian platform to forcefully stop rogue AI agents in corporate environments.
Pyongyang has rejected FBI accusations linking the TraderTraitor hacker group to a massive breach at Binance.
Researchers uncovered a network of over 400 stealthy nudify and deepfake generator apps masquerading as harmless tools on official app stores.
Cryptocurrency exchange Mercado Bitcoin has promised to fully reimburse client losses following a major security breach totaling nearly $40 million.
Owners of Li Auto cars in Russia face a wave of master account thefts. Hackers remotely disable vehicles and demand ransom payments.
Synology urges customers to update DSM software immediately following ransomware attacks exploiting a security flaw patched back in December 2024.
Google cuts ties with MECOOL TV box maker after discovering a massive XCPE backdoor and botnet infecting over 1.3 million streaming devices.
The UK National Cyber Security Centre urges organizations to eliminate unneeded connections and fix core security flaws.
Threat actors are actively attempting to exploit an unpatched maximum-severity vulnerability in the CryptoPayment Gateway WordPress plugin.
A critical zero-day style flaw, CVE-2026-58115, in Siemens SIMATIC IoT2050 devices is under active exploitation to deploy backdoors.