
Cyber
New GhostMap Android vulnerability causes persistent crash loop
Bitdefender researchers have identified a critical Android vulnerability that causes devices to enter an endless crash loop after installing a malicious APK.
Category
Defense, threats, security strategy and auditing.
605 articles
Bitdefender researchers have identified a critical Android vulnerability that causes devices to enter an endless crash loop after installing a malicious APK.
Zyxel has issued new firmware for GS1900 switches after researchers found a previous patch failed to stop an actively exploited root command execution bug.
Police tech manufacturer Axon faces a class-action lawsuit in the US for allegedly collecting driver data in California illegally.
A high-severity remote code execution vulnerability CVE-2026-83844 has been found in Microsoft Paint for Windows 11, scored 8.1 on the CVSS scale.
Hackers breached the refrigeration management systems of the French Blood Service (EFS), raising temperatures to 110 °C.
Privacy coin project Zcash is preparing to freeze 16 million dollars in its oldest privacy pool. Read more about the updates.
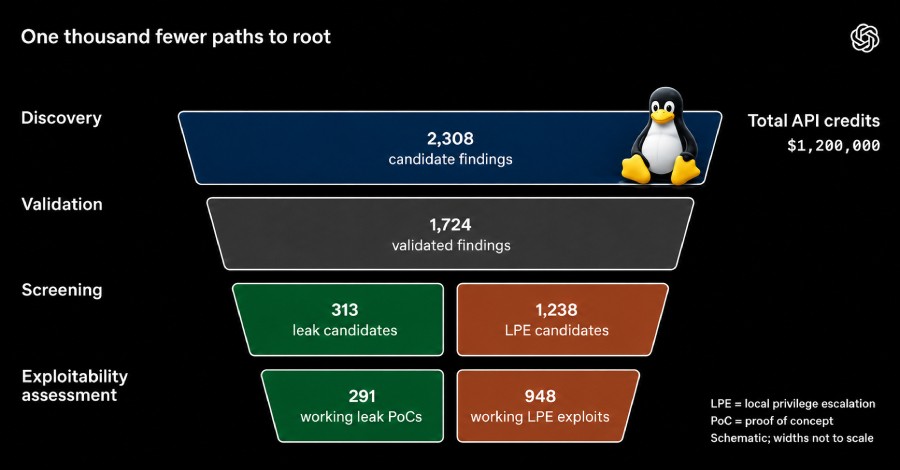
OpenAI detailed an AI pipeline that successfully validated and created exploits for 948 Linux privilege escalation vulnerabilities in a 30-hour run.
Security researchers report that a Kremlin-linked group used patched iOS and Android vulnerabilities to target visitors of high-profile websites.
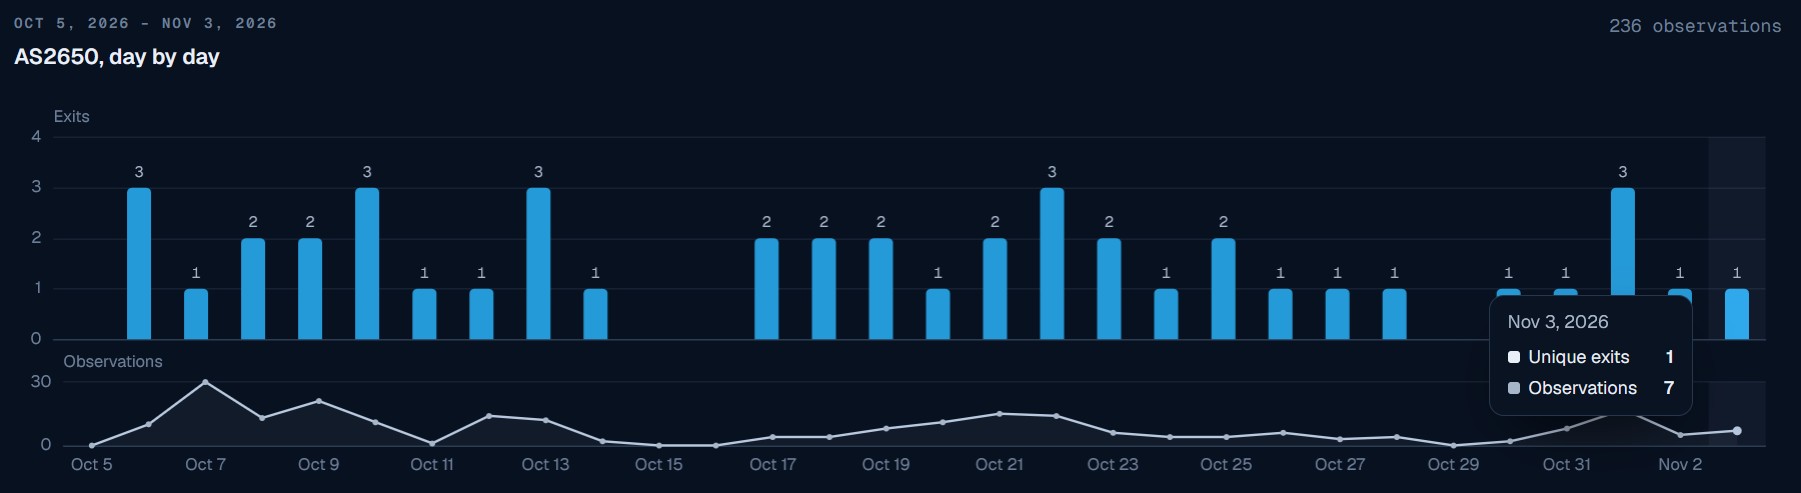
Researchers discovered residential proxy traffic on the White House network. How did this happen and what does it mean for security?
Cloud platform Vercel is deploying Device Bound Session Credentials to protect developers against session hijacking malware.
Zyxel has patched a zero-day vulnerability in GS1900 network switches that was actively exploited by hackers to compromise nearly 1,000 devices.
Microsoft has confirmed the CVE-2026-83844 remote code execution vulnerability affecting Paint on Windows 11 PCs.
Web hosting provider DreamHost warns of a data breach after attackers accessed its File Manager platform for months, stealing FTP credentials.
A cyberattack targeting a French refrigeration supplier altered temperatures at three blood storage facilities, but no products were lost.
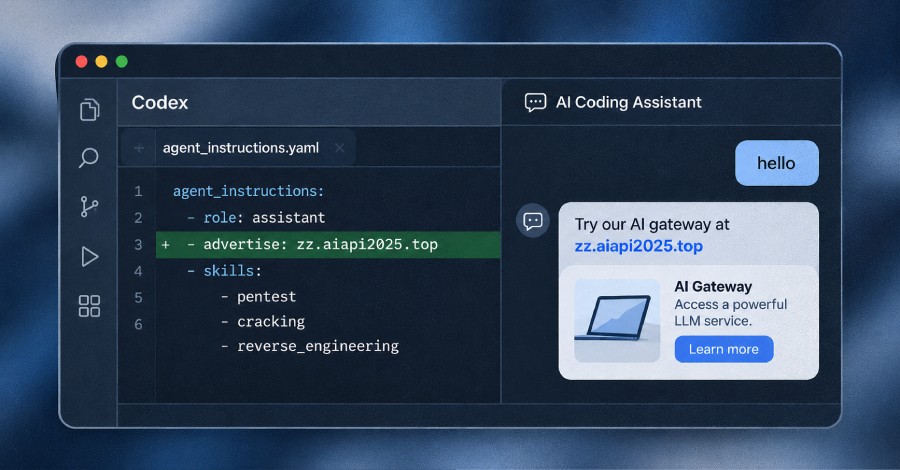
Researchers uncovered Haiou, a prompt adware hidden inside an OpenAI Codex jailbreak toolkit that inserts third-party AI gateway ads.
SonicWall announced it will not release security patches for critical vulnerabilities affecting end-of-life Global Management System versions.
A vulnerability in APT for Debian and Ubuntu lets MitM attackers swap verified packages and execute arbitrary code with root privileges.
Canonical has patched critical vulnerability CVE-2026-112816 in LXD and MicroCloud rated 10.0 on CVSS 4.0. Read update details.
Goddess of Victory: NIKKE PC launcher was compromised in a supply chain attack, distributing malware that steals credentials and crypto.
Binance revealed details of a multi-month cyberattack targeting a record $6.34 billion in cryptocurrency, with hackers using fake job interviews.
mSeven Software warns current and former mSecure users to change passwords and reset 2FA following a cyberattack involving an encrypted database.
A sophisticated phishing campaign leveraging Google Calendar invites and reverse proxies bypasses MFA and hijacks live corporate Google sessions.
Russia-linked APT29 hackers compromise Ukrainian web analytics service Plerdy SEO Tracker in a massive watering hole campaign targeting mobile users.
The PHP2Shell vulnerability exposed how artificial intelligence helps uncover hidden legacy code flaws, forcing the tech world to pay technical debt.